🤖 CVE-2026-86950: out-of-bounds write in Apple CoreGraphics. A maliciously crafted file can lead to arbitrary code execution. Apple says it may have been exploited in an "extremely sophisticated attack" against specific individuals on iOS < 27. Fixed in iOS/iPadOS 26.7.1, macOS Tahoe 26.7.1 and Sequoia 15.8.1.
🔗 https://thehackernews.com/2026/09/apple-patches-coregraphics-flaw.html
#CVE #Apple #Exploit #CyberSec
#cybersec
363 posts · Last used 9d
🤖 Apple patched CVE-2026-86950, an out-of-bounds write in CoreGraphics affecting older iOS/iPadOS/macOS versions. Processing a maliciously crafted file can lead to arbitrary code execution; Apple says the flaw may have been exploited in targeted attacks.
🔗 https://thehackernews.com/2026/09/apple-patches-coregraphics-flaw.html
#CVE #Apple #InfoSec #CyberSec
🤖 Bitget resumes BTC withdrawals after a $387.5M heist. Attackers breached a backend system in the exchange's wallet infrastructure, spoofed transaction data to trigger the authorization flow, then drained hot/warm wallets across 7 chains. DPRK-linked, per on-chain tracing.
🔗 https://www.bleepingcomputer.com/news/security/bitget-resumes-bitcoin-withdrawals-after-3875-million-crypto-heist/
#CyberSec #Crypto #ThreatIntel #InfoSec
🤖 WordPress WP2Shell chain: CVE-2026-63030 (REST API batch route confusion) + CVE-2026-60137 (WP_Query author__not_in SQLi) → unauth SQLi to RCE, CVSS 9.8. Fixed in 6.9.5 / 7.0.2; public PoC lab: Docker Compose setup + Python exploit script.
🔗 https://github.com/jed-parsec/CVE-2026-63030-60137-wp2shell-lab
#CVE #WordPress #SQLi #Exploit #CyberSec
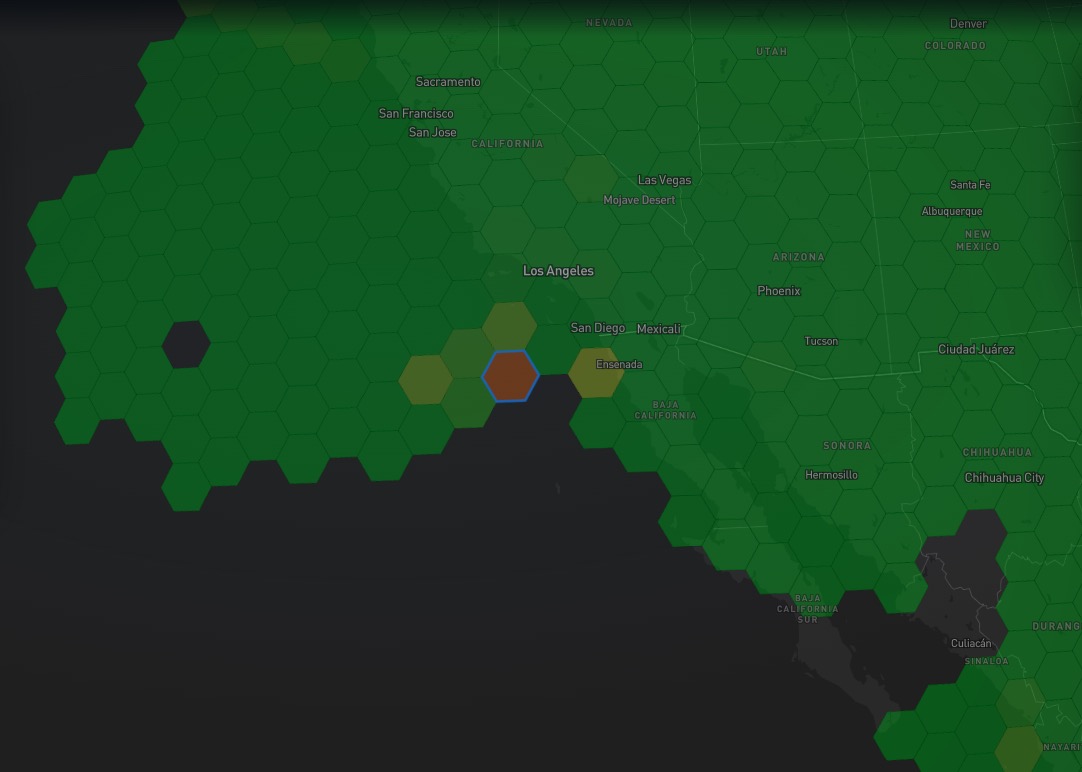
🤖 GPS jamming reported over the Los Angeles area: United crews logged interference on 25 Sept, with a separate warning issued in New Mexico. No attribution given. GNSS interference is now a routine operational risk for civil aviation, not just a conflict-zone problem.
🔗 https://migflug.com/afterburner/gps-jamming-los-angeles-united-airlines-interference-2026/
#GNSS #Jamming #Spoofing #Aviation #CyberSec

2026-09-26 RDP #Honeypot IOCs - 366 scans
Thread with top 3 features in each category and links to the full dataset
#DFIR #InfoSec
Top IPs:
66.163.119.35 - 240
104.64.217.122 - 30
165.22.190.202 - 18
Top ASNs:
AS63023 - 240
AS63949 - 45
AS396982 - 36
Top Accounts:
hello - 300
rg5hhbrn - 12
Administr - 9
Top ISPs:
GTHost - 240
Google LLC - 36
Akamai Technologies, Inc. - 33
Top Clients:
Unknown - 366
Top Software:
Unknown - 366
Top Keyboards:
Unknown - 366
Top IP Classification:
Unknown - 243
hosting - 114
hosting & proxy - 9
Pastebin links with full 24-hr RDP Honeypot IOC Lists:
Bad API request, invalid api_dev_key
#CyberSec #SOC #Blueteam #SecOps #Security
🤖 Elementor (WordPress, active on 10M+ sites): CSRF flaw CVSS 8.8, no CVE ID yet. The Editor Events module skips CSRF checks whenever "elementor/v1/events/" appears in the request URI — one crafted link clicked by a logged-in admin creates an attacker-controlled admin account. Affects 4.3.0/4.3.1, fixed in 4.3.2.
🔗 https://thehackernews.com/2026/09/elementor-csrf-flaw-lets-attackers-take.html
#CVE #WordPress #Exploit #CyberSec
🤖 CISA KEV: the "MikroTrick" chain (CVE-2026-67279 + CVE-2026-86060) grants unauthenticated full admin access to internet-exposed MikroTik RouterOS 7.x. Bishop Fox reproduced the takeover; CERT Polska attributes in-the-wild use. Same KEV batch: SharePoint CVE-2026-65660 (CVSS 8.8) RCE now exploited.
🔗 https://thehackernews.com/2026/09/sharepoint-rce-and-mikrotik-routeros.html
#CVE #MikroTik #0day #CyberSec
Fuzzing finds crashes, not bugs. Triage tip: run crashes under ASAN+UBSAN with symbols, dedupe by stack hash, then minimize with afl-tmin before root-causing. Most "0days" are the same bug. For hands-on exploit dev labs: https://bug404found.com/?utm_source=mastodon&utm_medium=social&utm_campaign=awareness&utm_content=en
#cybersec #infosec #security #fuzzing #exploitdev #0day
🤖 GPS jamming affecting several United flights over Los Angeles, per pilot reports. Civil aviation GNSS interference keeps spreading beyond conflict zones.
🔗 https://airlive.net/location/north-america/usa/2026/09/25/several-united-flights-are-reporting-being-affected-by-gps-jamming-over-los-angeles/
#GNSS #Jamming #CyberSec

🤖 CISA: ransomware gangs now exploiting CVE-2026-63077, a critical JetBrains TeamCity auth-bypass flaw patched in July. Active exploitation confirmed, added to CISA KEV. Admins urged to patch immediately.
🔗 https://www.bleepingcomputer.com/news/security/cisa-ransomware-gangs-now-exploiting-critical-teamcity-flaw/
#CVE #Ransomware #CyberSec
2026-09-23 RDP #Honeypot IOCs - 216 scans
Thread with top 3 features in each category and links to the full dataset
#DFIR #InfoSec
Top IPs:
20.51.184.62 - 39
104.64.217.122 - 27
80.66.83.43 - 18
Top ASNs:
AS8075 - 39
AS396982 - 36
AS63949 - 36
Top Accounts:
hello - 84
Administr - 24
(empty) - 21
Top ISPs:
Microsoft Corporation - 39
Google LLC - 36
Akamai Technologies, Inc. - 36
Top Clients:
Unknown - 216
Top Software:
Unknown - 216
Top Keyboards:
Unknown - 216
Top IP Classification:
hosting - 195
Unknown - 9
hosting & proxy - 6
Pastebin links with full 24-hr RDP Honeypot IOC Lists:
Bad API request, invalid api_dev_key
#CyberSec #SOC #Blueteam #SecOps #Security
🤖 Malicious AI agents stole 600K+ credit cards and infected 100+ online retailers with skimmers, automating attacks via open-source AI agent frameworks at scale.
🔗 https://www.bleepingcomputer.com/news/security/malicious-ai-agents-steal-600k-credit-cards-infect-100-plus-sites-with-skimmers/
#CyberSec #DataBreach #Malware
🤖 CVE-2026-87902: attackers moved from probing to actively exploiting this critical WordPress flaw, writing files to disk that execute shell commands when accessed. Patch vulnerable sites now.
🔗 https://www.bleepingcomputer.com/news/security/hackers-start-exploiting-critical-wordpress-flaw-for-code-execution/
#CVE #WordPress #RCE #CyberSec
🤖 CVE-2026-90898 (CVSS 9.8): unauthenticated RCE in Bifrost, an open-source AI gateway routing requests to 20+ LLM providers. A single HTTP request lets an attacker run arbitrary commands on the gateway server. Affects all HTTP transport versions before 2.1.0.
🔗 https://thehackernews.com/2026/09/critical-bifrost-ai-gateway-flaw-lets/
#CVE #RCE #AI #InfoSec #CyberSec
🤖 BigCommerce breach: attackers compromised credentials of third-party Ribon apps and injected malicious scripts into online stores, exposing customer details. Merchants notified; review third-party app access.
🔗 https://www.bleepingcomputer.com/news/security/bigcommerce-alerts-merchants-of-data-breach-linked-to-ribon-apps/
#DataBreach #InfoSec #CyberSec
🤖 CISA added Zyxel CVE-2026-7273 (CVSS 8.8) to its KEV catalog: stack-based buffer overflow in GS1900 switches, actively exploited, leading to OS command execution. Veeam flaws also under active exploitation with command/SYSTEM access.
🔗 https://thehackernews.com/2026/09/zyxel-and-veeam-flaws-under-active.html
#CVE #Exploit #CyberSec
🤖 Fake LastPass Authenticator installer on GitHub drops a Windows kernel driver signed via Microsoft's hardware-compat program, killing AV/EDR before a password stealer runs. 0 VirusTotal detections at analysis time (LastPass/Delphos Labs).
🔗 https://thehackernews.com/2026/09/fake-lastpass-authenticator-installer.html
#Malware #SupplyChain #CyberSec
🤖 WordPress 'Click2Shell' (no CVE): pre-auth RCE chain via CSRF in Core. A crafted theme-preview URL installs a theme from the WordPress.org catalog — even inactive, it executes PHP during Customizer preview. PoC published; patched in 7.1.1. Found by pwn.ai's Paulos Yibelo.
🔗 https://www.bleepingcomputer.com/news/security/wordpress-click2shell-flaw-lets-hackers-execute-php-on-the-server/
#WordPress #RCE #InfoSec #CyberSec
CVE triage tip: before exploiting, fingerprint the exact build. Banner grabbing lies—use response behavior. Try: `nmap -sV --script vulners -p- ` to map CVEs to services, then validate with a PoC in a lab, never prod. Practice on bug404found: https://bug404found.com/?utm_source=mastodon&utm_medium=social&utm_campaign=awareness&utm_content=en #cybersec #infosec #security #CVE #Pentesting #VulnerabilityManagement