#databreach
301 posts · Last used 2d
Boosted by @trending@homestead.social
I fell for the Booking.com WhatsApp scam today. There has apparently been a #databreach at #bookingcom, which provides a little bit of truth to this "please verify your credit card now" scam. They knew my name, my phone number, the hotel I was staying at and the exact dates. That, a little bit of time pressure and a potential quick solution got me.
I managed to complete the flow once, which according to them would only reserve the money. Something failed and I tried again. This time they were asking me to confirm the balance of my account for verification, and that finally triggered the alert for me.
I'm retrospect, the originating WhatsApp number was located in Brazil (which was not where I was going). The name didn't match the name of the Hotel representative in the message, and the website's title was Booking.com, which didn't match the actual host name in the URL. I didn't notice.
Approach shit like this calmly and don't let people push you to rash decisions.
#Phishing #scam
Replying to
Reward: You've received the Fossil Record Badge — a commemorative exhibit of everything that used to be private.
https://securityboulevard.com/2026/10/ransomware-data-theft-surged-275-in-2026-schools-hospitals-and-government-agencies-had-some-of-the-largest-claims
#Ransomware #CyberSecurity #DataBreach #InfoSec #CriticalInfrastructure #AchievementUnlocked (3/3)
Vista Del Mar Child and Family Services Reports Data Breach Involving Personal and Health Information
Vista Del Mar Child and Family Services disclosed a data breach after an unauthorized actor accessed systems containing personal and protected health information. The organization took its network offline, engaged cybersecurity experts, and is reviewing affected files to identify and notify potentially impacted individuals.
****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/vista-del-mar-child-and-family-services-reports-data-breach-involving-personal-and-health-information-c-o-8-r-w/gD2P6Ple2L
Park Place Behavioral Healthcare Data Breach Exposes Personal, Health, and Financial Information
Park Place Behavioral Healthcare disclosed a data breach after an unauthorized party accessed its systems and copied files containing personal, health, and financial information. The organization reset account credentials and strengthened remote access controls. Park Place Behavioral Healthcare is offering complimentary credit monitoring and identity theft restoration services to affected individuals.
****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/park-place-behavioral-healthcare-data-breach-exposes-personal-health-and-financial-information-e-4-z-n-o/gD2P6Ple2L
🛡 THREAT INTEL | Ar Valve Resources
🟢 Actor "Wallstreet" claims Undisclosed
Allegedly exposed
• Customer data
⚠️ Unverified claim
https://www.yazoul.net/intel/claim/2026-09-27-ar-valve-resources-ransomware-claim-by-wallstreet-sep-2026
by Yazoul AI
#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec
FBI reportedly declares 'cyber security incident' after hackers steal agents' personal data
https://techcrunch.com/2026/09/28/fbi-reportedly-declares-cyber-security-incident-after-hackers-steal-agents-personal-data/
#CyberSecurity #DataBreach #TechNews
Government activity topped our tracking this week with 284 stories, including 33 today. Some call this a coordinated attack on the state. I think that misses the point.
https://theperimetersite.com/report/311
#vulnerability #databreach #infosec
Some #Supabase customers are publicly exposing reams of people’s data to the web
https://techcrunch.com/2026/09/25/some-supabase-customers-are-publicly-exposing-reams-of-peoples-data-to-the-web/
#privacy #cybersecurity #DataBreach
So one FBI breach led to this. And it's only early Saturday 😅 .
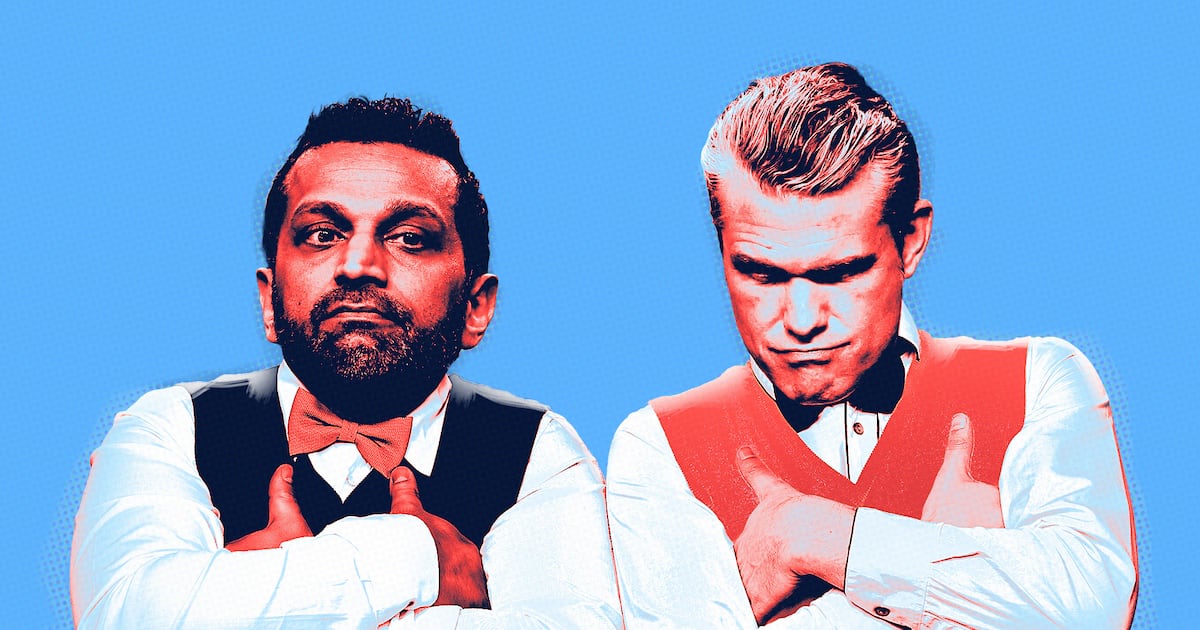
The Daily Beast: Keystone Kash and Pentagon Pete Hit by Twin Humiliations https://www.thedailybeast.com/keystone-kash-and-pentagon-pete-hit-by-twin-humiliations/ @thedailybeast@newsie.social
Reuters had more about the files that were affected.
Reuters, from yesterday: ShinyHunters attackers say they stole psychiatric and medical records of FBI staff https://www.reuters.com/world/shinyhunters-hackers-say-they-stole-psychiatric-medical-records-fbi-staff-2026-09-25/ @Reuters@flipboard.com #infosec #databreach #cyberattack
Replying to
Reward: You've received a Leaky Lanyard — equip it to automatically badge into rooms you shouldn't be in.
https://www.reuters.com/world/hacked-fbi-data-has-sensitive-information-about-employees-intelligence-roles-2026-09-23
#CyberSecurity #DataBreach #FBI #InfoSec #GovernmentSecurity #AchievementUnlocked (3/3)
🛡 THREAT INTEL | Westside GI
🔴 Actor "pear" claims Undisclosed
⚠️ Unverified claim
https://www.yazoul.net/intel/claim/2026-09-25-westside-gi-ransomware-claim-by-pear-sept-2026
by Yazoul AI
#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec
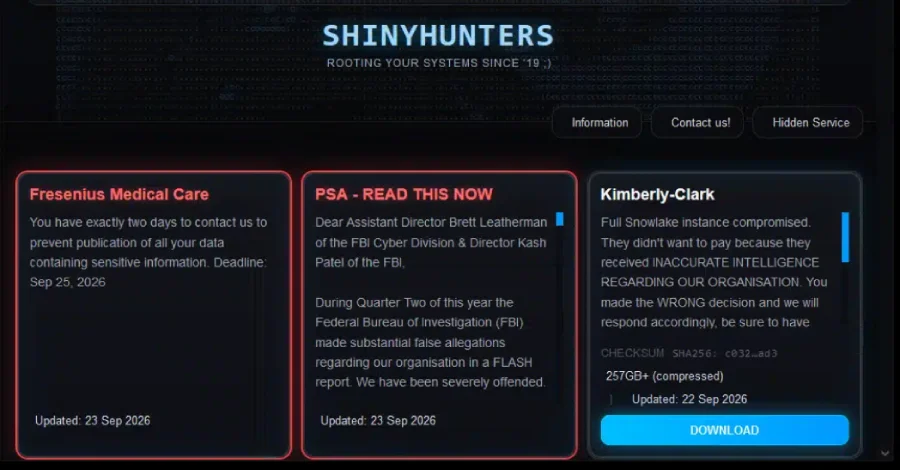
The FBI ShinyHunters breach may expose staff of the FBI's Remote Operations Unit hacking team, via a claimed Oracle PeopleSoft zero-day. FBI confirms probe.
#FBI #ShinyHunters #RemoteOperationsUnit #DataBreach #PeopleSoft #CyberSecurity
https://meterpreter.org/fbi-breach-shinyhunters-remote-operations-unit/?utm_source=mastodon&utm_medium=jetpack_social
@XposedOrNot@infosec.exchange += Fanlore Data Breach
The Fanlore #databreach occurred in August 2026 when the fan culture wiki operated by the Organization for Transformative Works was compromised. The incident exposed 145K unique email addresses and associated account credentials.
Exposed data: Email addresses, Usernames, MD5 password hashes, and PBKDF2 password hashes
Potential risks: Account takeover, Credential stuffing, Phishing, Targeted scams, and Privacy breaches
The FBI is investigating claims by hacker group ShinyHunters that it exploited a zero-day bug in software used by FBIJobs and stole 2–3 TB of data, potentially including personal information on current/former employees and applicants. #databreachhttps://arstechnica.com/tech-policy/2026/09/fbi-rushes-to-investigate-if-shinyhunters-hack-of-thousands-of-employees-is-real/
🛡 THREAT INTEL | www.francare.com
🔴 Actor "ZaWoo" claims Undisclosed
Allegedly exposed
• Health records
• Customer data
⚠️ Unverified claim
https://www.yazoul.net/intel/claim/2026-09-24-francare-ransomware-claim-by-zawoo-aug-2026
by Yazoul AI
#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec
🛡 THREAT INTEL | The Merrimack County
🟢 Actor "Booba Project" claims 3GB
⚠️ Unverified claim
https://www.yazoul.net/intel/claim/2026-09-23-merrimack-county-ransomware-claim-by-booba-project-sep-2026
by Yazoul AI
#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec
CTOS Digital Discloses Unauthorized Access to Consumer Business Environment
CTOS Digital disclosed unauthorized access to an environment supporting its consumer business, where a limited subset of processed consumer information was accessed. The company contained the incident, notified authorities, and temporarily disrupted some credit reporting services while an independent forensic investigation continues.
****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/ctos-digital-discloses-unauthorized-access-to-consumer-business-environment-1-g-4-n-s/gD2P6Ple2L
Discover how autonomous AI agents executed 105 cyberattacks in 5 days, stealing over 600,000 credit cards using tools like Strix, Cairn, and Hermes.
#CyberSecurity #ArtificialIntelligence #DataBreach #Carding #TechNews
https://meterpreter.org/autonomous-ai-agents-steal-credit-cards/?utm_source=mastodon&utm_medium=jetpack_social
🤖 Malicious AI agents stole 600K+ credit cards and infected 100+ online retailers with skimmers, automating attacks via open-source AI agent frameworks at scale.
🔗 https://www.bleepingcomputer.com/news/security/malicious-ai-agents-steal-600k-credit-cards-infect-100-plus-sites-with-skimmers/
#CyberSec #DataBreach #Malware