#passkeys
23 posts · Last used 12d

The FIDO Alliance publishes certificates for "Device attestation" for Passkeys through something called the FIDO Metadata Service(MDS). The idea here is that a service can restrict the use of passkeys to certain vendors. (One can argue whether that's a problematic, user-hostile feature to begin with.)
Looking through the certificates, we find this "interesting" cert:
"CN=FIDO2 Enterprise Attestation BATCH KEY prime256v1, emailAddress=tools@fidoalliance.org, O=FIDO Alliance, OU=Authenticator Attestation, C=US, ST=MY, L=Wakefield"
Its Issuer looks even more interesting:
"CN=FIDO2 Enterprise Attestation TEST ROOT, emailAddress=tools@fidoalliance.org, O=FIDO Alliance, OU=CWG, C=US, ST=CA, L=Mountain View"
It's not the only one in there that implies it's some form of "test" cert. However, this one is particularly interesting, as... it's also, apparently, using a "test" private key, which you can find here:
https://github.com/fido-alliance/conformance-test-tools-resources/blob/main/docs/FIDO2/Authenticator/README.md
In case you want to pretend that you're building a "KQC QuKey Bio FIDO2 Authenticator", that may come in handy.
It's not the only odd issue in that list, there are also plenty of certs with encoding errors. See, e.g.: https://github.com/fido-alliance/fido-device-onboard-feedback/issues/5
(Found together with @duesee@norden.social )
#0day #passkeys #fido

Replying to
@14mission@sfba.social @morgan@sfba.social for reference:
"From February 1, 2027, Microsoft-provided telecom delivery for SMS and voice will be retired for all users except Global Administrators and external users. For Global Administrators and external users, Microsoft-provided SMS and voice authentication will be retired on July 1, 2027."
https://learn.microsoft.com/en-us/entra/identity/authentication/concept-sms-voice-retirement
#Microsoft #EntraID #MFA #Passkeys #SMS


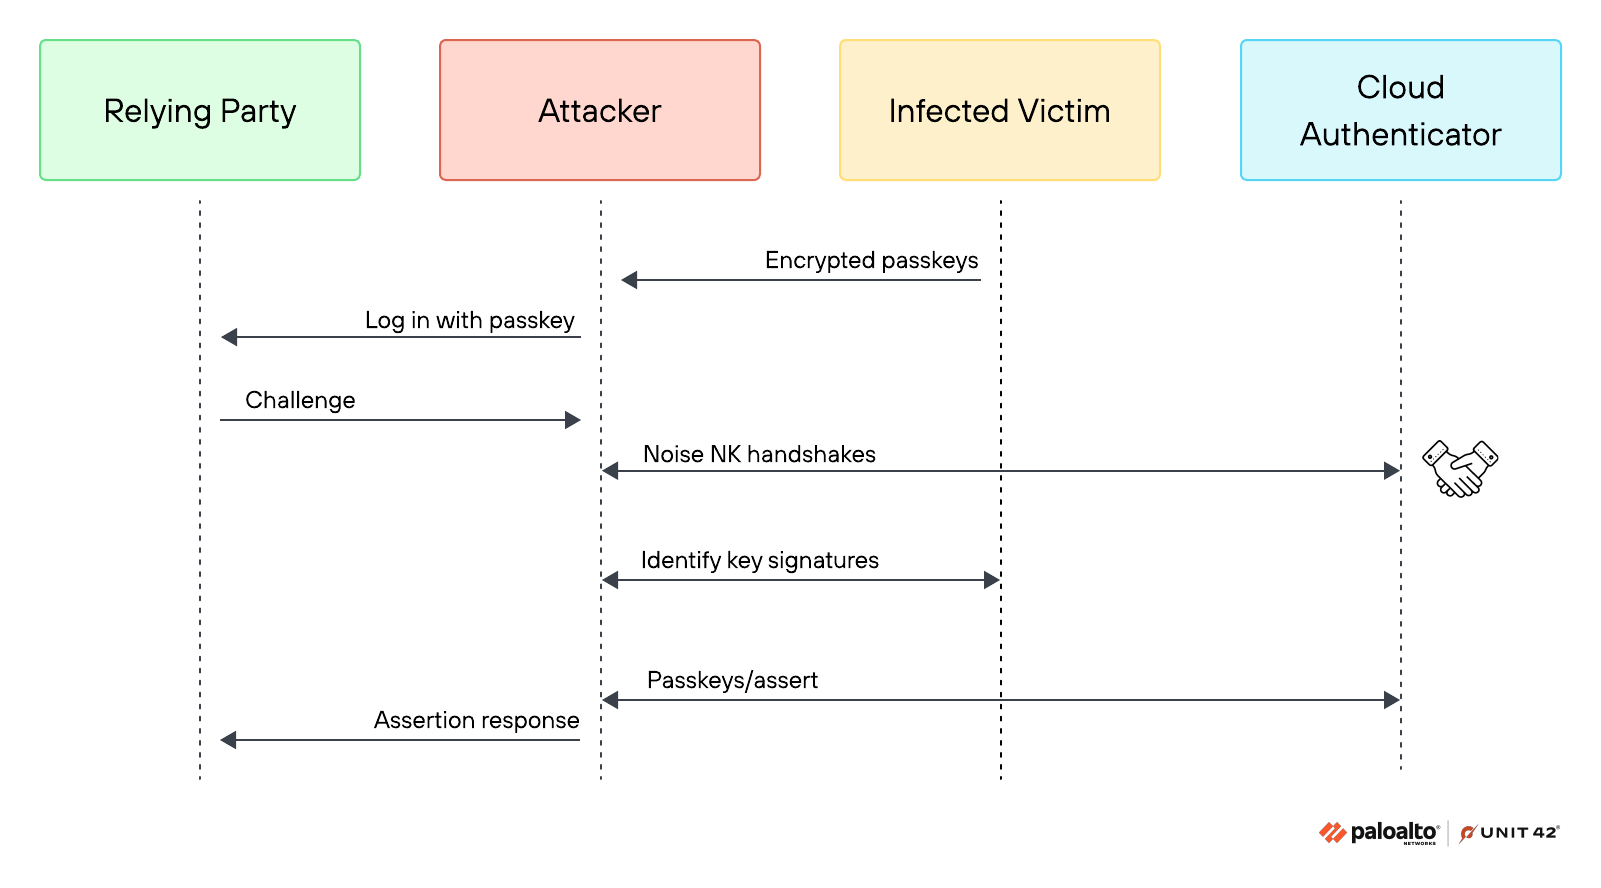
Mit #PassTaKey wurden 3 schwere Sicherheitslücken in Verbindung mit #Google #Chrome und #Passkeys veröffentlicht, die unter #Windows eine komplette Übernahme aller Passkeys ermöglichen.
Inwiefern sich das Risiko einer fehlerhaften Softwareimplementierung kompensieren lässt, habe ich auf meinem Blog beschrieben:
Authentifizierung mit FIDO2 und Passkeys
https://karl-voit.at/FIDO2-vs-Passkeys/
Kurz: nach wie vor ist das non-plus-ultra ein bis zwei #FIDO2 Hardware-Tokens: Ziemlich sicherer Schutz gegen #Phishing, wohingegen Passkeys leider nicht immer helfen, obwohl es fälschlicherweise oft anders behauptet wird.
#20241005_FIDO2VsPasskeys #publicvoit #Authentifizierung #TOTP #GoogleAuthenticator #MicrosoftAuthenticator #Sicherheit
So #passkeys They are the "new" thing (yes they have been here for quite some time already). And whilst being phishing resistant, the usage and making your phone not a SPOF is not user-friendly either right?
I mean, how do I explain this new tech to my older parents?
Who has dealt with this already?
#passkey #passkeys #oldergenerations

Unit 42 researchers exposed three bypass methods targeting Google Password Manager passkeys on Windows devices, enabling silent authentication.
#Passkeys #Cybersecurity #GooglePasswordManager #Unit42 #Windows
https://meterpreter.org/google-password-manager-passkeys/?utm_source=mastodon&utm_medium=jetpack_social

Auth0's Passkey APIs let you build passkey sign-in directly into your own UI instead of redirecting to Universal Login. Wrote up how the two fit together, hand-rolled vs pre-built self-service passkey management, and one Allowed Origins (CORS) setting worth checking before you go chasing a WebAuthn bug that isn't there.
https://tobytes.com/articles/building-embedded-passkey-login-with-auth0
#auth0 #passkeys #identity
Hopefully, the fixes aren't too far behind.
Google Password Manager passkeys could be at risk with new 'Pass-ta-key' attack
https://9to5google.com/2026/08/04/google-password-manager-passkeys-could-be-at-risk/
#Google #passwordManager #Passkeys #Vulnerabilities #Security #Tech

🤖 Pass-ta-key: three new attacks let malware on compromised Windows devices hijack Google-synced passkeys via Google Password Manager, bypassing user verification and extracting private keys (Unit 42).
🔗 https://www.bleepingcomputer.com/news/security/new-pass-ta-key-attacks-let-malware-hijack-google-synced-passkeys/
#Passkeys #Malware #CyberSec #InfoSec
Friends, I need some help and advice.
Microsoft recently announced retirement of Microsoft-provided SMS and voice authentication in Entra ID.
Of course, "good", you say -- me, too. But I'm working with an organization that has some extremely non-techie employees, and I've got to figure out the easiest path to help them get properly on-boarded with Passkeys.
Microsoft Authenticator seems to support Passkeys natively (the key is stored IN MS Authenticator). Is this the best way to do this? My non-techie users are primarily mobile phone users on Exchange Plan 1 (no "fat" client).
Help!
#passkeys #webauthn #fido #microsoft #mfa #lazyweb #help
References:
https://www.microsoft.com/en-us/security/blog/2026/07/13/microsoft-entra-id-security-updates-passkeys-are-the-default-authentication-method-in-entra-id/
https://mc.merill.net/message/MC1426371

Google selfie video sign-in lets you record guided head movements to regain account access, with liveness checks that block deepfakes and photos.
#Google #AccountSecurity #SelfieVideo #Biometrics #Deepfake #Passkeys
https://securityonline.info/google-selfie-video-sign-in/?utm_source=mastodon&utm_medium=jetpack_social

I don't like #Passkeys over #Passphrase and #MFA (edit: specifically, rotating pin codes via a password manager or dedicated auth app)
Am I wrong? or is it the children who are wrong. #Security #Privacy

Two of my banks recently implemented #passkeys, and the contrast between them is stark.
I went to log in to one and they wouldn’t let me in until I “verified my identity” using a text message code to a phone number they apparently got from some data broker or by uploading my government ID and a video (obviously not happening). When I eventually got their support to let me in, the site forced passkey setup with no options at all. There’s no way to set up more than one passkey, no way to revoke access from the one I set up, and no way to log in via password anymore. They made every single decision in the most incorrect way possible. Utter garbage. Unfortunately, they’re the only option available to me for the particular account I have, so I’m stuck with them.
Meanwhile, Wealthfront reopened a support ticket I filed years ago requesting passkey support to let me know they had added it. I logged in with a password, and the site offered to set up a passkey. In my user profile’s authentication page, there’s a section listing all my passkeys (and app-specific password names, etc.). It allows me to specify friendly names to track which is which, add more, and remove keys I no longer control. It’s pretty much perfect!
#passkey #webauthn

Opaque, Interoperable Passkey Records
https://words.filippo.io/passkey-record/
#Security #Passkeys #Cryptography

Microsoft is making passkeys the default authentication experience in Entra ID, while Google is expanding FIDO2 security key support for Workspace users on Windows—another step toward phishing-resistant, passwordless authentication.
#Passkeys #Cybersecurity #DigitalIdentity

#AirPlus bietet als erste Bank, mit der ich eine Geschäftsbeziehung unterhalte (und ich bin Kunde bei mehreren Dutzend Banken!), #TOTP und sogar #Passkeys.
Das ist sehr, sehr lobenswert #Sicherheit #ITSicherheit #2FA #TFA. Ich frage mich, wieso andere Banken das nicht auch machen?
(Passkeys allerdings scheinen zurzeit "defekt" zu sein, beim Versuch einen #Passkey zu registrieren, werde ich ausgeloggt...)
Clear 🤝 #passkeys
Replying to
@mkristensson@thepit.social True.
However, some megacorps are extending passkeys to allow for sharing and moving keys. Unfortunately, you lose the phishing protection with that as well.
So yes, some passkeys setups aren't protection against phishing any more. 😞
Therefore, I use user/password + #FIDO2 hardware token when it *really* needs to be secure and #TOTP for the rest.
Even with passkeys, FIDO2 hardware tokens don't support those convenience features where #passkeys lose #phishing protection.
More on https://karl-voit.at/FIDO2-vs-Passkeys/ (German)
#security #publicvoit
RE: https://infosec.exchange/@hcf/116766730950368400
The year is 2028. Through-Skin-DNA-Sequencing has supplanted Brain-Waves-Pattern-Matching, which has supplanted Intestinal-Fauna-Surveying, which has supplanted #passkeys as “the last authentication factor you’ll ever need.” Logging in to your bank requires a username, account number, password, one-time SMS code, passkey, vomit sample, 5-minute EEG and 3-minute arm scan.
Incoming money transfers still take two working days to show up on your account. Tuesdays and Thursdays are bank holidays.