#openthreatexchange

13 posts · Last used Sep 08

Contagious Interview steps outside the developer workflow Pulse ID: 6a9f9497e3279459528af385 Pulse Link: https://otx.alienvault.com/pulse/6a9f9497e3279459528af385 Pulse Author: Tr1sa111 Created: 2026-09-08 04:52:39 Be advised, this data is unverified and should be considered preliminary. Always do further verification. #CyberSecurity #InfoSec #OTX #OpenThreatExchange #bot #Tr1sa111
0
0
0
0
ASCII smuggling crosses over from AI prompt injection to phishing evasion Pulse ID: 6a9f94de75e1687221b3fb6f Pulse Link: https://otx.alienvault.com/pulse/6a9f94de75e1687221b3fb6f Pulse Author: Tr1sa111 Created: 2026-09-08 04:53:50 Be advised, this data is unverified and should be considered preliminary. Always do further verification. #CyberSecurity #InfoSec #OTX #OpenThreatExchange #Phishing #bot #Tr1sa111
0
0
0
0
Chinese-Speaking Operator Uses AI Agents to Target Government and Education Systems Across Asia Pulse ID: 6a9f95581dc4c6de1b0540b2 Pulse Link: https://otx.alienvault.com/pulse/6a9f95581dc4c6de1b0540b2 Pulse Author: Tr1sa111 Created: 2026-09-08 04:55:52 Be advised, this data is unverified and should be considered preliminary. Always do further verification. #Asia #Chinese #CyberSecurity #Education #Government #InfoSec #OTX #OpenThreatExchange #RAT #bot #Tr1sa111
0
0
0
0
Malicious Chrome Extension Can Steal Login Sessions and Turn PCs Into Remote Backdoors Indicators extracted from public reporting. Source: https://socradar.io/blog/peep-browser-rat-chrome-extension/ Pulse ID: 6a9e7c2ce1129dcc5ae37c04 Pulse Link: https://otx.alienvault.com/pulse/6a9e7c2ce1129dcc5ae37c04 Pulse Author: CyberHunter_NL Created: 2026-09-07 08:56:12 Be advised, this data is unverified and should be considered preliminary. Always do further verification. #BackDoor #Browser #Chrome #ChromeExtension #CyberSecurity #HTTP #HTTPS #InfoSec #OTX #OpenThreatExchange #RAT #RCE #bot #CyberHunter_NL
1
0
0
0
Hackers Actively Exploiting PaperCut Servers Command Execution Vulnerabilities Indicators extracted from public reporting. Source: https://cybersecuritynews.com/papercut-command-execution-flaws-exploited/ Pulse ID: 6a9e6e1a6891a0ac0d93faec Pulse Link: https://otx.alienvault.com/pulse/6a9e6e1a6891a0ac0d93faec Pulse Author: CyberHunter_NL Created: 2026-09-07 07:56:10 Be advised, this data is unverified and should be considered preliminary. Always do further verification. #AWS #CyberSecurity #HTTP #HTTPS #InfoSec #OTX #OpenThreatExchange #RCE #bot #CyberHunter_NL
0
0
0
0
BGP Hijack Diverts Softaculous Traffic to Deliver Malicious Virtualizor Update Indicators extracted from public reporting. Source: https://www.virtualizor.com/blog/security-incident-bgp-hijacking/ Pulse ID: 6a965ad3c05038d75e980a31 Pulse Link: https://otx.alienvault.com/pulse/6a965ad3c05038d75e980a31 Pulse Author: CyberHunter_NL Created: 2026-09-01 04:55:46 Be advised, this data is unverified and should be considered preliminary. Always do further verification. #CyberSecurity #HTTP #HTTPS #InfoSec #OTX #OpenThreatExchange #RCE #bot #CyberHunter_NL
0
0
0
0
Popular npm Package With 150K+ Weekly Downloads Hit by Credential-Stealing Supply-Chain Worm Indicators extracted from public reporting. Source: https://research.jfrog.com/post/shai-hulud-trinitite/ Pulse ID: 6a956bc92f739d8a0e243dd2 Pulse Link: https://otx.alienvault.com/pulse/6a956bc92f739d8a0e243dd2 Pulse Author: CyberHunter_NL Created: 2026-08-31 11:55:53 Be advised, this data is unverified and should be considered preliminary. Always do further verification. #CyberSecurity #HTTP #HTTPS #InfoSec #NPM #OTX #OpenThreatExchange #RCE #Worm #bot #CyberHunter_NL
0
0
0
0
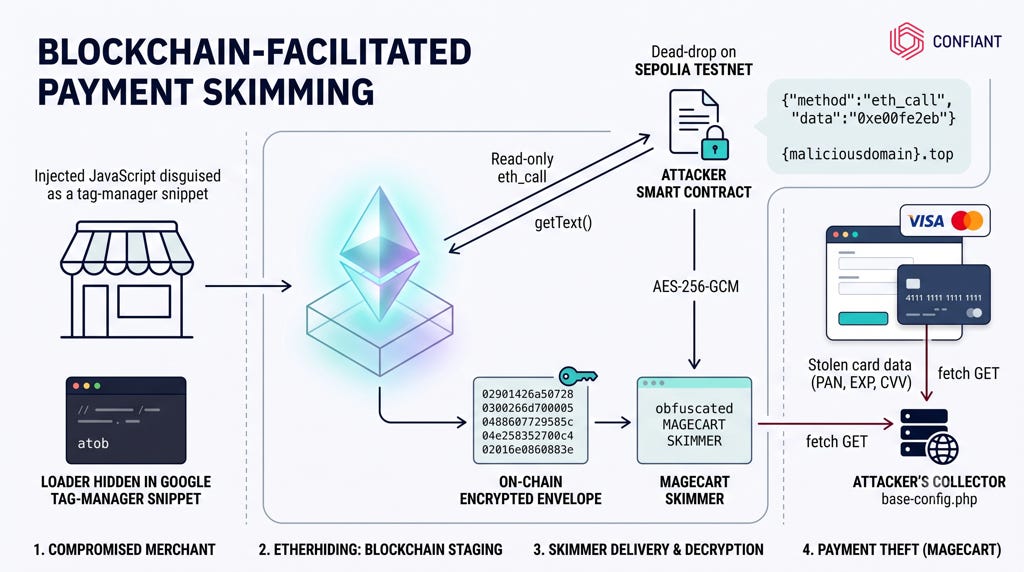
Hackers Use Ethereum Blockchain to Steal Credit Card Data From Online Shoppers Indicators extracted from public reporting. Source: https://blog.confiant.com/p/skimming-on-the-blockchain-a-magecart Pulse ID: 6a956bcebf30addf06a8d0a2 Pulse Link: https://otx.alienvault.com/pulse/6a956bcebf30addf06a8d0a2 Pulse Author: CyberHunter_NL Created: 2026-08-31 11:55:58 Be advised, this data is unverified and should be considered preliminary. Always do further verification. #BlockChain #CreditCard #CyberSecurity #HTTP #HTTPS #InfoSec #Magecart #OTX #OpenThreatExchange #RCE #bot #CyberHunter_NL
0
0
0
0
Security Update – August 2, 2026 Pulse ID: 6a740db739f5ddf6e048bf0a Pulse Link: https://otx.alienvault.com/pulse/6a740db739f5ddf6e048bf0a Pulse Author: Tr1sa111 Created: 2026-08-06 04:29:43 Be advised, this data is unverified and should be considered preliminary. Always do further verification. #CyberSecurity #InfoSec #OTX #OpenThreatExchange #bot #Tr1sa111
0
0
0
0
Analysis of BlueShell Variants Used by APT Groups BlueShell is an open-source remote access trojan developed in Go language, primarily used by Chinese-based threat actors. A variant of BlueShell has been identified in post-intrusion activities by APT groups including BlackTech, targeting organizations in Japan, South Korea, and Thailand. This variant differs from the original through a dedicated dropper mechanism, proxy server-based C2 communication, and anti-forensic capabilities. The dropper deploys the variant to /tmp/kthread, disguises it as a Linux kernel worker process, and removes filesystem traces. Recent variants observed since 2024 include XOR-encoded configuration data and proxy functionality, indicating continuous development. The malware performs hostname verification, validates C2 certificates, and implements commands for file transfer, remote shell, and SOCKS5 proxy capabilities. Pulse ID: 6a69c06b441d532a963887ee Pulse Link: https://otx.alienvault.com/pulse/6a69c06b441d532a963887ee Pulse Author: AlienVault Created: 2026-07-29 08:57:15 Be advised, this data is unverified and should be considered preliminary. Always do further verification. #Chinese #CyberSecurity #InfoSec #Japan #Korea #Linux #Malware #OTX #OpenThreatExchange #Proxy #RAT #RCE #RemoteAccessTrojan #SouthKorea #Thailand #Trojan #bot #socks5 #AlienVault
0
0
0
0
Contagious Interview malware in SVG images: DPRK campaign A DPRK-aligned threat group is targeting developers through fake job postings and coding challenges in a campaign tracked as REF9403. Attackers post fake job offers in developer forums, then send trojanized repositories containing fully functional e-commerce projects with malicious code hidden using steganography inside SVG flag images. When developers run these projects, the malware deploys four-stage payloads aligned with OTTERCOOKIE: a browser credential and cryptocurrency wallet stealer, a file exfiltration module, a Socket.IO-based remote access trojan, and a clipboard stealer. The campaign was discovered after targeting Elastic's community Slack workspace. Multiple trojanized repositories were found with zero antivirus detections at the time of discovery, demonstrating the sophistication of this supply chain attack vector against software developers. Pulse ID: 6a5a8ba0229db5a5b2686baa Pulse Link: https://otx.alienvault.com/pulse/6a5a8ba0229db5a5b2686baa Pulse Author: AlienVault Created: 2026-07-17 20:08:00 Be advised, this data is unverified and should be considered preliminary. Always do further verification. #Browser #Clipboard #CyberSecurity #DPRK #InfoSec #Malware #OTX #OpenThreatExchange #RAT #RCE #RemoteAccessTrojan #SVG #Steganography #SupplyChain #Trojan #bot #cryptocurrency #developers #AlienVault
1
0
1
0
Analysis of Gamaredon campaign targeting Ukraine weaponizing CVE-2025-8088 A campaign exploiting the WinRAR path-traversal vulnerability CVE-2025-8088 has been actively targeting Ukraine since February 2026, with ongoing activity through June 2026. The operation uses Ukrainian military and conscription-themed documents as lures, distributed as RAR archives. The malicious archives contain NTFS alternate data streams with path-traversal sequences that automatically place LNK files into the Windows Startup folder upon extraction. These shortcuts execute hidden PowerShell stagers incorporating anti-analysis techniques including debugger checks, disk-space verification, and sleep delays to evade sandbox detection. The persistent nature of the attacks demonstrates continuous targeting of Ukrainian entities over a four-month period using social engineering focused on military documentation themes. Pulse ID: 6a34c6344468a941c924c02c Pulse Link: https://otx.alienvault.com/pulse/6a34c6344468a941c924c02c Pulse Author: AlienVault Created: 2026-06-19 04:31:48 Be advised, this data is unverified and should be considered preliminary. Always do further verification. #CyberSecurity #Gamaredon #InfoSec #LNK #Military #OTX #OpenThreatExchange #PowerShell #RAT #SocialEngineering #UK #Ukr #Ukraine #Ukrainian #Vulnerability #WinRAR #Windows #bot #AlienVault
0
1
1
0
You've seen all posts