#otx
23 posts · Last used 20d
Beware the SparroWock: The backdoor that bites, the commands that catch
Indicators extracted from public reporting. Source: https://www.eset.com/int/business/services/threat-intelligence/?utm_source=welivesecurity.com&utm_medium=referral&utm_campaign=wls-research&utm_content=beware-sparrowock-backdoor-bites-commands-catch&sfdccampaignid=7011n0000017htTAAQ
Pulse ID: 6aad0a9f11a363a15814494b
Pulse Link: https://otx.alienvault.com/pulse/6aad0a9f11a363a15814494b
Pulse Author: CyberHunter_NL
Created: 2026-09-18 09:55:43
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#BackDoor #OTX #CyberHunter_NL
ThreatsDay: Self-Rewriting Agents, 800+ Flaws Patched, Insider SIM Swaps and 22 More New Stories
Indicators extracted from public reporting. Source: https://thehackernews.com/2026/09/threatsday-self-rewriting-agents-800.html
Pulse ID: 6aacb63e160b1f1ab8d3a1fd
Pulse Link: https://otx.alienvault.com/pulse/6aacb63e160b1f1ab8d3a1fd
Pulse Author: CyberHunter_NL
Created: 2026-09-18 03:55:42
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#OTX #CyberHunter_NL
PIVOTPIPE: A New .NET-based Unofficial Beacon Payload
Pulse ID: 6aab7c429cbc2675255fd261
Pulse Link: https://otx.alienvault.com/pulse/6aab7c429cbc2675255fd261
Pulse Author: Tr1sa111
Created: 2026-09-17 05:36:02
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#NET #OTX #Tr1sa111
The banana stand: brokering and managing infections across Asia using MQTT
Pulse ID: 6aab7c49da521a5fde002948
Pulse Link: https://otx.alienvault.com/pulse/6aab7c49da521a5fde002948
Pulse Author: Tr1sa111
Created: 2026-09-17 05:36:09
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#Asia #MQTT #OTX #Tr1sa111
The extension you never installed: KREMLIN forges Chrome's own integrity checks to steal banking sessions
Pulse ID: 6aab7c54a7d3b34045501163
Pulse Link: https://otx.alienvault.com/pulse/6aab7c54a7d3b34045501163
Pulse Author: Tr1sa111
Created: 2026-09-17 05:36:20
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#Chrome #OTX #Tr1sa111
StyleSmuggler: Magento and Adobe Commerce 0-day RCE under active attack
Pulse ID: 6aa8f78f28a8d7073b557898
Pulse Link: https://otx.alienvault.com/pulse/6aa8f78f28a8d7073b557898
Pulse Author: Tr1sa111
Created: 2026-09-15 07:45:19
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#0Day #Adobe #Magento #RCE #OTX #Tr1sa111
Phishing Attacks Serve Browser-in-the-Browser Pages, Rogue RMM Persistence
Pulse ID: 6aa8d48bb9571ef6455a21c6
Pulse Link: https://otx.alienvault.com/pulse/6aa8d48bb9571ef6455a21c6
Pulse Author: Tr1sa111
Created: 2026-09-15 05:15:55
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#Phishing #Browser #OTX #Tr1sa111
Gaming the system: how a Chinese-speaking actor turned Brazilian government sites into an SEO weapon
Pulse ID: 6aa8d28c00a1fa0064105d5e
Pulse Link: https://otx.alienvault.com/pulse/6aa8d28c00a1fa0064105d5e
Pulse Author: Tr1sa111
Created: 2026-09-15 05:07:24
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#Chinese #Government #OTX #Tr1sa111
Financially Motivated Threat Actor BREEZE COMET Targets Brazil
Pulse ID: 6aa8d24632573b2a3c81b5f6
Pulse Link: https://otx.alienvault.com/pulse/6aa8d24632573b2a3c81b5f6
Pulse Author: Tr1sa111
Created: 2026-09-15 05:06:14
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#Brazil #OTX #Tr1sa111
Hackers Exploit FortiGate SSL-VPN Vulnerability to Attack Broadband Provider
Indicators extracted from public reporting. Source: https://cybersecuritynews.com/fortigate-ssl-vpn-vulnerability/
Pulse ID: 6aa835ee9dc88a53daa3efde
Pulse Link: https://otx.alienvault.com/pulse/6aa835ee9dc88a53daa3efde
Pulse Author: CyberHunter_NL
Created: 2026-09-14 17:59:10
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#SSL #VPN #Vulnerability #OTX #CyberHunter_NL
Contagious Interview steps outside the developer workflow
Pulse ID: 6a9f9497e3279459528af385
Pulse Link: https://otx.alienvault.com/pulse/6a9f9497e3279459528af385
Pulse Author: Tr1sa111
Created: 2026-09-08 04:52:39
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#CyberSecurity #InfoSec #OTX #OpenThreatExchange #bot #Tr1sa111
ASCII smuggling crosses over from AI prompt injection to phishing evasion
Pulse ID: 6a9f94de75e1687221b3fb6f
Pulse Link: https://otx.alienvault.com/pulse/6a9f94de75e1687221b3fb6f
Pulse Author: Tr1sa111
Created: 2026-09-08 04:53:50
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#CyberSecurity #InfoSec #OTX #OpenThreatExchange #Phishing #bot #Tr1sa111
Chinese-Speaking Operator Uses AI Agents to Target Government and Education Systems Across Asia
Pulse ID: 6a9f95581dc4c6de1b0540b2
Pulse Link: https://otx.alienvault.com/pulse/6a9f95581dc4c6de1b0540b2
Pulse Author: Tr1sa111
Created: 2026-09-08 04:55:52
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#Asia #Chinese #CyberSecurity #Education #Government #InfoSec #OTX #OpenThreatExchange #RAT #bot #Tr1sa111
Malicious Chrome Extension Can Steal Login Sessions and Turn PCs Into Remote Backdoors
Indicators extracted from public reporting. Source: https://socradar.io/blog/peep-browser-rat-chrome-extension/
Pulse ID: 6a9e7c2ce1129dcc5ae37c04
Pulse Link: https://otx.alienvault.com/pulse/6a9e7c2ce1129dcc5ae37c04
Pulse Author: CyberHunter_NL
Created: 2026-09-07 08:56:12
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#BackDoor #Browser #Chrome #ChromeExtension #CyberSecurity #HTTP #HTTPS #InfoSec #OTX #OpenThreatExchange #RAT #RCE #bot #CyberHunter_NL
Hackers Actively Exploiting PaperCut Servers Command Execution Vulnerabilities
Indicators extracted from public reporting. Source: https://cybersecuritynews.com/papercut-command-execution-flaws-exploited/
Pulse ID: 6a9e6e1a6891a0ac0d93faec
Pulse Link: https://otx.alienvault.com/pulse/6a9e6e1a6891a0ac0d93faec
Pulse Author: CyberHunter_NL
Created: 2026-09-07 07:56:10
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#AWS #CyberSecurity #HTTP #HTTPS #InfoSec #OTX #OpenThreatExchange #RCE #bot #CyberHunter_NL
BGP Hijack Diverts Softaculous Traffic to Deliver Malicious Virtualizor Update
Indicators extracted from public reporting. Source: https://www.virtualizor.com/blog/security-incident-bgp-hijacking/
Pulse ID: 6a965ad3c05038d75e980a31
Pulse Link: https://otx.alienvault.com/pulse/6a965ad3c05038d75e980a31
Pulse Author: CyberHunter_NL
Created: 2026-09-01 04:55:46
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#CyberSecurity #HTTP #HTTPS #InfoSec #OTX #OpenThreatExchange #RCE #bot #CyberHunter_NL
Popular npm Package With 150K+ Weekly Downloads Hit by Credential-Stealing Supply-Chain Worm
Indicators extracted from public reporting. Source: https://research.jfrog.com/post/shai-hulud-trinitite/
Pulse ID: 6a956bc92f739d8a0e243dd2
Pulse Link: https://otx.alienvault.com/pulse/6a956bc92f739d8a0e243dd2
Pulse Author: CyberHunter_NL
Created: 2026-08-31 11:55:53
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#CyberSecurity #HTTP #HTTPS #InfoSec #NPM #OTX #OpenThreatExchange #RCE #Worm #bot #CyberHunter_NL
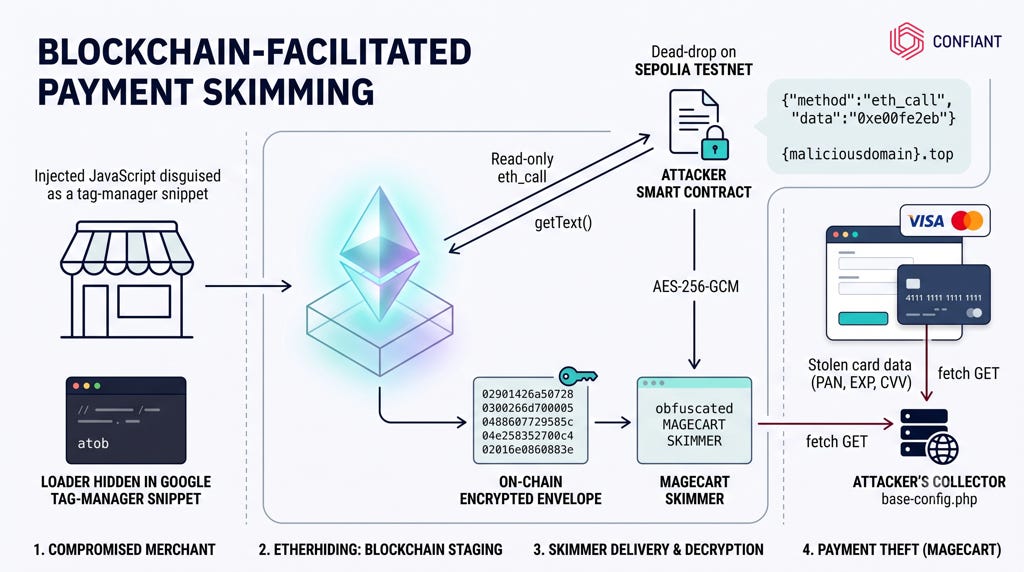
Hackers Use Ethereum Blockchain to Steal Credit Card Data From Online Shoppers
Indicators extracted from public reporting. Source: https://blog.confiant.com/p/skimming-on-the-blockchain-a-magecart
Pulse ID: 6a956bcebf30addf06a8d0a2
Pulse Link: https://otx.alienvault.com/pulse/6a956bcebf30addf06a8d0a2
Pulse Author: CyberHunter_NL
Created: 2026-08-31 11:55:58
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#BlockChain #CreditCard #CyberSecurity #HTTP #HTTPS #InfoSec #Magecart #OTX #OpenThreatExchange #RCE #bot #CyberHunter_NL
Dark Caracal Hackers Use Ethereum Blockchain to Keep New Malware Connected After C2 Disruption
Indicators extracted from public reporting. Source: https://arcticwolf.com/resources/blog/dark-caracal-reloaded-new-malware-same-hunting-grounds/
Pulse ID: 6a913f0e09f2b3ab49915028
Pulse Link: https://otx.alienvault.com/pulse/6a913f0e09f2b3ab49915028
Pulse Author: CyberHunter_NL
Created: 2026-08-28 07:55:58
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#BlockChain #CyberSecurity #HTTP #HTTPS #InfoSec #Malware #OTX #OpenThreatExchange #RCE #bot #CyberHunter_NL
Security Update – August 2, 2026
Pulse ID: 6a740db739f5ddf6e048bf0a
Pulse Link: https://otx.alienvault.com/pulse/6a740db739f5ddf6e048bf0a
Pulse Author: Tr1sa111
Created: 2026-08-06 04:29:43
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#CyberSecurity #InfoSec #OTX #OpenThreatExchange #bot #Tr1sa111