#vmware
26 posts · Last used 14d
Hot off the press:
#Broadcom reps confirmed a recent change in the availability of the #VMware #VDDK library that had other ecosystem players crying foul last week.
Find out what they had to say about the change here: https://www.techtarget.com/it-infrastructure/news/366648768/Broadcom-confirms-change-in-VMware-migration-tool-access
Broadcom has quietly stopped offering public downloads for VMware's Virtual Disk Development Kit (VDDK), a key tool for VM backup and management. New users can no longer easily access it without an account.
Proprietary ecosystems always tighten the loop eventually. It's a concrete reason why open-source virtualization platforms like Proxmox and KVM are seeing so much momentum.
https://itsfoss.com/news/broadcom-removes-vmware-vddk-downloads/
#vmware #opensource
🆕 Check out how my time at VMware Explore 2026 was!
https://thedxt.ca/2026/09/i-went-to-vmware-explore-2026/
#VMware #VMwareExplore #VMwareExplore2026 #vExpert
CVE-2026-59346, a critical VMware Workstation vulnerability, lets an attacker escape a guest VM and execute code on the host. Broadcom rates it 9.3 CVSS.
#VMware #Workstation #Fusion #CVE202659346 #VMXNET3 #Broadcom #InfoSec #PatchNow
https://securityonline.info/vmware-cve-2026-59346-code-execution-host/?utm_source=mastodon&utm_medium=jetpack_social
HostDzire suffered a critical ransomware attack on its VMware infrastructure, encrypting virtual disks and causing total data loss for affected VPS users.
#HostDzire #Ransomware #VPS #VMware #Cybersecurity
https://securityonline.info/hostdzire-ransomware-attack/?utm_source=mastodon&utm_medium=jetpack_social
#VMware: three critical #vulnerabilities in VMware vCenter, ESX, Workstation, and Fusion, allow attackers to bypass authentication, execute arbitrary code, or escape from a virtual machine to the host. Patches released by Broadcom - it's time to patch!
👇
https://www.bleepingcomputer.com/news/security/vmware-fixes-three-critical-flaws-allowing-auth-bypass-vm-escapes/
🤖 VMware patches three critical flaws in vCenter, ESX, Workstation, and Fusion. Two allow authentication bypass, one enables VM escape to the host OS. Broadcom recommends immediate patching.
🔗 https://www.bleepingcomputer.com/news/security/vmware-fixes-three-critical-flaws-allowing-auth-bypass-vm-escapes/
#VMware #Virtualization #CyberSec
🚨 Critical VMware Advisory
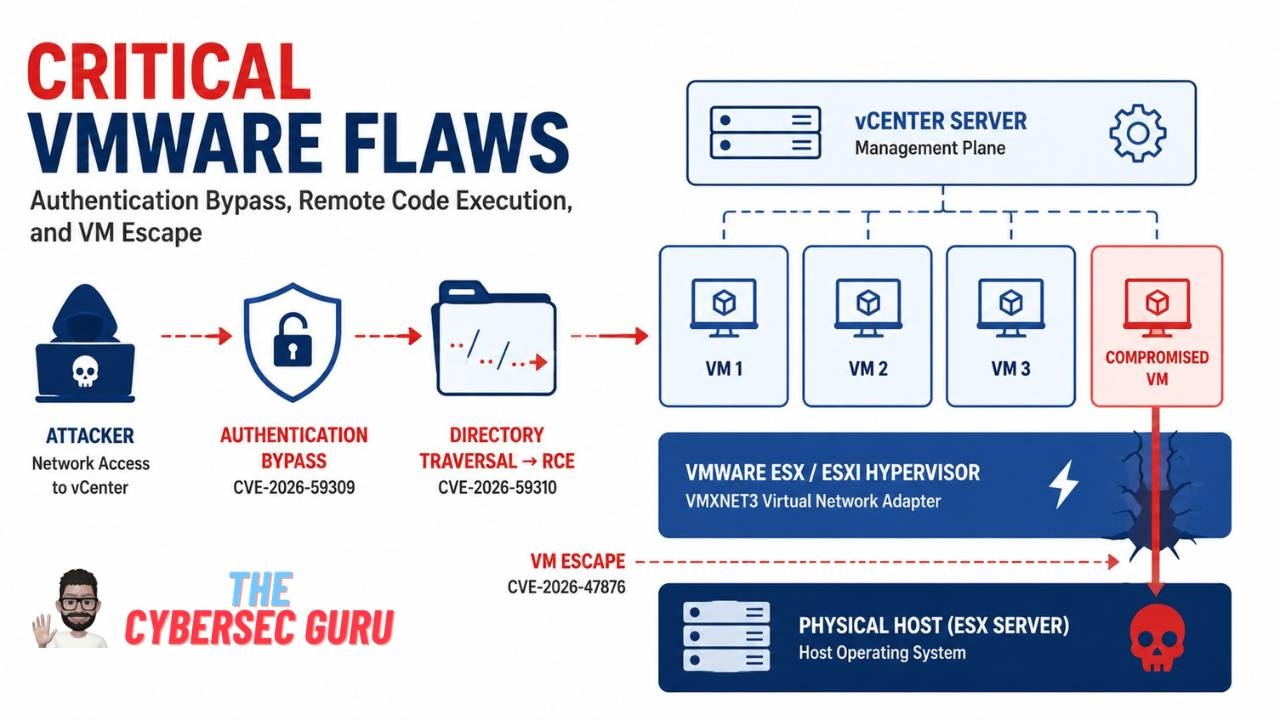
Broadcom has patched multiple critical VMware vulnerabilities affecting vCenter Server and ESXi, including an authentication bypass (CVSS 9.8), directory traversal leading to RCE (CVSS 9.8), and a VM escape via VMXNET3 (CVSS 9.3). Organizations should prioritize patching vCenter and ESXi infrastructure as soon as possible.
Technical breakdown, affected versions, and mitigation:
https://thecybersecguru.com/news/critical-vmware-vcenter-auth-bypass-rce-vm-escape-vulnerabilities/
#InfoSec #CyberSecurity #VMware #vCenter #ESXi #Virtualization #RCE #ThreatIntel #BlueTeam #SysAdmin #CVE
Broadcom Patches Critical #VMware #ESXi Vulnerability Enabling Host Code Execution
https://securityaffairs.com/196231/security/broadcom-patches-critical-vmware-esxi-vulnerability-enabling-host-code-execution.html
#securityaffairs #hacking
Broadcom patched a critical VMware vCenter vulnerability. CVE-2026-59309 and CVE-2026-59310 both score 9.8 CVSS and allow auth bypass or code execution.
#VMware #vCenter #CVE202659309 #CVE202659310 #ESXi #InfoSec
https://meterpreter.org/vmware-vcenter-cve-2026-59309/?utm_source=mastodon&utm_medium=jetpack_social
Broadcom released updates to fix a critical VMware authentication bypass (CVE-2026-59309). A directory traversal flaw (CVE-2026-59310) was also patched.
#VMware #CyberSecurity #CVE202659309 #InfoSec
https://securityonline.info/vmware-authentication-bypass-cve-2026-59309/?utm_source=mastodon&utm_medium=jetpack_social
Gotta love Broadcom.
Several examples are now making circles, where ex. VMware users are getting contacts from them, telling they're having a win-back campaign with incredible offers.
Just how stupid they think we are? When they started to squeeze blood from stone, having to move to something else cost time and money for a lot of companies. Small businesses and hobbyists got shafted even harder.
Now that their customers have gone elsewhere, there's been increased interest, development and funding to a lot of options and the "but what if they cause horrible problems" FUD has been laid to rest.
#vmware #it
I’m excited to be attending VMware Explore this year in Las Vegas. Here are some of the sessions I am looking forward to attending.
https://thedxt.ca/2026/07/im-going-to-vmware-explore-2026/
#VMware #VMwareExplore #vExpert
I like a fresh lab. I do not like building one for the umpteenth time, especially when the build takes longer than the thing I actually wanted to test.
build-lab is the final piece in a three-script set, and the one that ties the other two together. One command, an ISO, and roughly half an hour later you have a Windows Server 2025 domain controller. Log on once and the domain populates itself with a directory that looks lived in, nested groups and GPOs and an Enterprise CA included. No GUI, no answer file to hand-edit, no clicking Next.
This is an orchestrator. It calls New-VMwareWorkstationVM to build and start the VM, pushes the new-AdDomain payload into the guest over vmrun, and kicks off the promotion. Still PowerShell 5.1, still nothing outside what Microsoft and VMware already ship.
One thing is deliberately manual. Directory population runs from a scheduled task that fires at your first Administrator logon, so you do have to log into the console once. I could automate it by storing a domain Administrator password under a startup-triggered task. That's the one compromise I decided not to make, even in a lab, and I'm still not certain it was the right call.
The interesting problem was verification. A successful AD promotion reboots Windows immediately, which tears down the vmrun guest-operations channel mid-call. A blocking call hung on that reboot and never came back. So the guest script gets launched fire-and-forget, which means there is no exit code to read. Just silence.
Instead, build-lab confirms success by polling for ntds.dit in the guest, and pulls the guest's deployment logs back to the host either way, because the run you need logs from is the one that failed.
https://github.com/0x44616e69656c/build-lab
What's the step in your lab build that you've rebuilt by hand so many times you've stopped noticing it?
#PowerShell #ActiveDirectory #WindowsServer #Automation #HomeLab #VMware #InfoSec
VMware Avi Load Balancer: Kritische Lücke erlaubt Umgehung von Anmeldung
VMware warnt vor zum Teil kritischen Lücken im Avi Load Balancer. Angreifer können Authentifizierung und Autorisierung umgehen.
https://www.heise.de/news/VMware-Avi-Load-Balancer-Kritische-Luecke-erlaubt-Umgehung-von-Anmeldung-11368661.html?wt_mc=sm.red.ho.mastodon.mastodon.md_beitraege.md_beitraege&utm_source=mastodon
#IT #Security #Sicherheitslücken #Updates #VMware #news
Got tired of clicking through Windows Server Setup for every disposable lab VM, so I automated it.
New-VMwareWorkstationVM takes a Windows Server 2025 ISO and gives you back a running, network-reachable VM. It generates an autounattend.xml, builds a bootable ISO with IMAPI2, creates a sparse VMDK, writes the VMX, and drops everything into your Workstation library.
MIT licensed. Requires VMware Workstation 17+ and a Windows Server 2025 ISO. Nothing else.
https://github.com/0x44616e69656c/New-VMwareWorkstationVM
#PowerShell #VMware #HomeLab
So what's the deal with #vmware ? Back in the day, they were fire.
https://arstechnica.com/information-technology/2026/07/sheetz-moves-838-stores-off-vmware-broadcom-created-too-much-uncertainty/
If you missed the patches:
The Hacker News: Firefox, Chrome, Adobe, and VMware Updates Fix Multiple Critical Security Flaws https://thehackernews.com/2026/07/firefox-chrome-adobe-and-vmware-updates.html @thehackernews@social.tchncs.de #infosec #vulnerability #Mozilla #Google #Adobe #VMWare
VMware Avi Load Balancer patches CVE-2026-47865 (CVSS 9.8), a critical authentication bypass, plus six more flaws. Upgrade the Avi Controller now.
#VMware #AviLoadBalancer #CVE202647865 #AuthenticationBypass #CyberSecurity
https://securityonline.info/vmware-avi-load-balancer-cve-2026-47865/?utm_source=mastodon&utm_medium=jetpack_social
VMware: 159 CVEs tracked, 86% unpatched. 10 CISA KEV exploited in wild. Avg CVSS 7.14, max 10. Trust Score: C. Virtualization isn't invulnerable. #VMware #cybersecurity #infosec
https://www.valtersit.com/vendors/vmware/