#tls
24 posts · Last used 9d
Skeptische Blicke beim #Stalwart-Vortrag am #LinuxDayAT – denn Mailserver-Installation und -Betrieb gelten als kompliziert. Bei Stalwart offenbar nicht. 😉
@opensourceuser@mastodon.social, 16 Jahre alt, hatte meinen Vortrag beim #CLT26 gesehen und die Installation direkt ausprobiert. Ergebnis: ein eigener, funktionierender Mailserver! 🎉
Anschließend haben wir anhand von https://www.hardenize.com noch den letzten Feinschliff besprochen: #DNSSEC, #MTA-STS, #TLS-RPT und #DANE.
Gerade nachgeschaut: Alles umgesetzt! 🎉 Besser geht's nicht.
Solche Erfolgserlebnisse geben Energie für die nächsten Vorträge. ❤️
wolfSSL 5.9.4 patches 10 wolfSSL vulnerabilities, including TLS authentication bypass flaws CVE-2026-93302 and CVE-2026-89136. Upgrade now.
#wolfSSL #wolfSSLVulnerabilities #TLS #AuthenticationBypass #EmbeddedSecurity #Cryptography #IoTSecurity #PatchNow
https://securityonline.info/wolfssl-5-9-4-vulnerabilities/?utm_source=mastodon&utm_medium=jetpack_social
Hab da mal was gebastelt... man hat am Wochenende ja nichts Besseres zu tun:
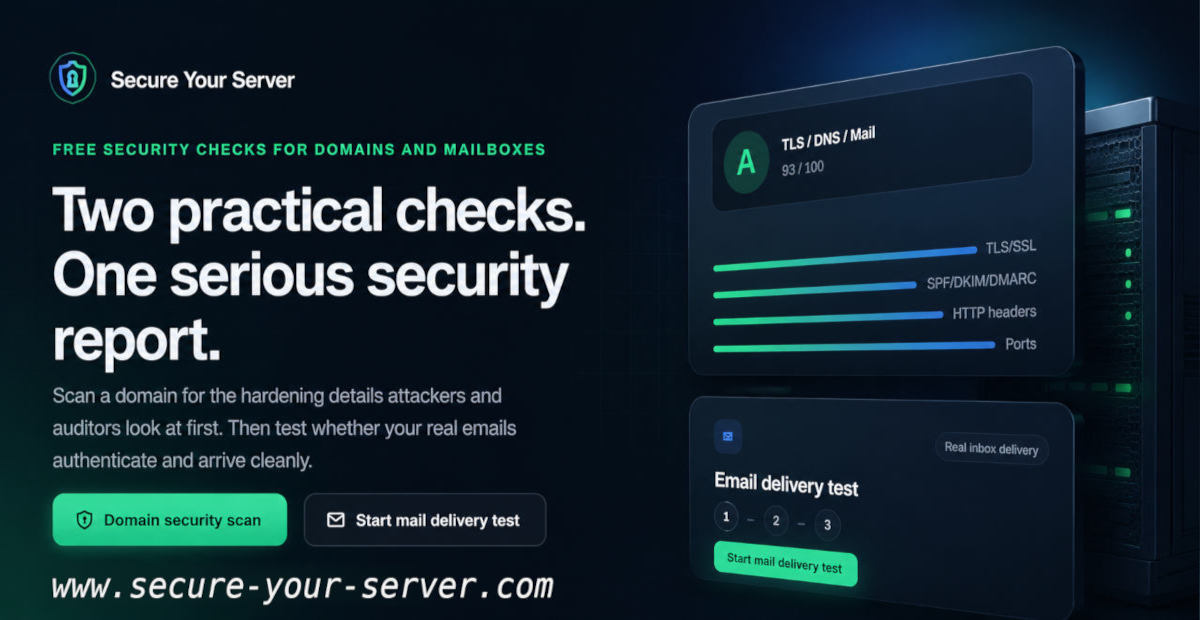
Secure Your ServerZwei praktische Checks. Ein seriöser Sicherheitsbericht.
Prüfe eine Domain auf die Härtungsdetails, auf die Angreifer und Audits zuerst schauen. Teste danach, ob deine echten E-Mails sauber authentifiziert und zugestellt werden. Kein Konto, kein Tracking, keine Bezahlschranke.
Domain-Sicherheitsscan
Vollständige externe Sicht auf TLS/SSL, SSH, offene Ports, DNS, SPF, DKIM, DMARC, MTA-STS, HTTP-Security-Header, WHOIS und PGP/WKD.
Mail-Zustellungstest
Erzeuge eine einmalige Testadresse, schick eine Mail aus deinem Postfach und sieh SPF, DKIM, DMARC, TLS, rDNS, Spam-Signale und Zustellungsdetails.
Bugs, Verbesserungswünsche bitte an "hallo [at] chrislo.de"
Mehr Infos:
https://www.sichere-deinen-server.de/
#chrislo #sys #secureyourserver #sicheredeinenserver #sicherheit #security #server #domain #tls #ssh
Nice bit of storytelling about the history of #TLS and the CA forum.
https://youtu.be/-9KiLFr8_hI?si=Rdf27a96oBwk_fh2
Replying to
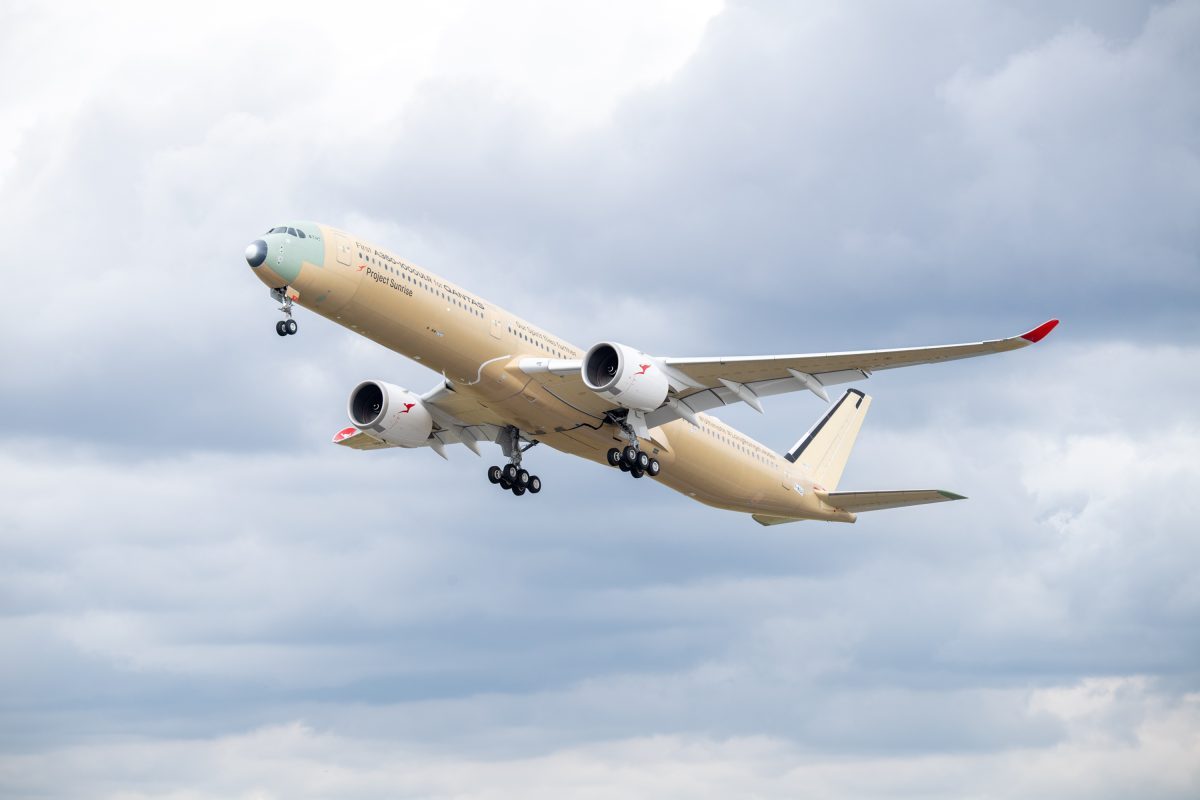
#Airbus A350-1000ULR test flight is currently returning from Melbourne🇦🇺 #MEL / #YMML to Toulouse🇫🇷 #TLS / #LFBO going eastbound with favorable winds to make a one-stop-around-the-world test. Later they will also need to test westbound Australia to Europe against unfavorable winds. https://www.flightaware.com/live/flight/AIB35LR/history/20260727/0700Z/YMML/LFBO #aviation #travel #avgeek
"Airbus Tests A350-1000ULR With First Flight to Australia" by AirlineGeeks / Zach Vasile - #Airbus test pilots flew a prototype A350-1000ULR (ultra long range) from the Airbus factory in Toulouse🇫🇷 #TLS / #LFBO non-stop for 19 hours to Melbourne🇦🇺 #MEL / #YMML. This test verifies ULR can achieve its purpose for launch customer Qantas🦘: non-stop flight between Western #Europe and Eastern #Australia with margin to route around weather and war zones. https://airlinegeeks.com/2026/07/27/airbus-tests-a350-1000ulr-with-first-flight-to-australia/ #aviation #travel #avgeek
Can't migrate everything to PQC at once. Which layer first?
TLS at the load balancer, IPsec at the tunnel, or application-layer encryption - each covers different threat surfaces. Six enterprise architecture scenarios, one recommendation per scenario.
https://postquantum.com/post-quantum/pick-one-pqc-layer-migration/
#PQC #TLS #IPsec #infosec #cryptography
I've republished to Codeberg my ca-incidents list, a permanent record of security/trust incidents involving SSL/TLS Certificate Authorities, because continuous scrutiny is important for the trust in the system: https://codeberg.org/joepie91/ca-incidents
It hasn't been updated in quite a while (last update was in 2016), and I'm sure that more things will have happened since, so please submit a PR if you know of any incidents to add!
#ProjectToot #TLS
Weekend Reads
- PQC for the RPKI https://labs.ripe.net/author/dirk/pqc-for-the-rpki/
- Big tech in Taiwan https://cset.georgetown.edu/publication/big-tech-in-taiwan/
- China's Internet Control https://locknet.chinafile.com/the-locknet/intro/
- Smartwatch security and privacy https://arxiv.org/abs/2507.07210
- App-layer desync attack TLS attack https://opossum-attack.com
#TLS question: when using mutual authentication (ie. server and client certs), is it possible for an MITM to spoof the client certificate when the server doesn't know the correct fingerprint yet, while presenting the correct server certificate to the client in the same connection, so without the client knowing anything is wrong?
Two critical RabbitMQ flaws allow authentication bypass. One forges TLS client certs; the other tricks OAuth2 JWKS to accept any JWT.
#RabbitMQ #AuthBypass #TLS #OAuth2 #InfoSec
https://securityonline.info/rabbitmq-authentication-bypass-flaws/?utm_source=mastodon&utm_medium=jetpack_social
If you learned the TLS handshake from a textbook, half the steps no longer happen.
No ClientKeyExchange. No 37 cipher suites. No secret on the wire. Attacks removed them one by one.
https://www.certkit.io/blog/tls-handshake-explained
#TLS #SysAdmin
We have better #security and #performance standards than most online banking sites, offering #0-RTT + #QUIC + #Post-Quantum #Cryptography. #tls #ssl #mastodon #instance
A widespread OpenSSL error handling flaw makes apt fail HTTPS in FIPS mode. A stale error queue entry gets misread as fatal. Audit your code.
#OpenSSL #ErrorHandling #FIPS #apt #Debian #TLS #CyberSecurity #InfoSec
https://securityonline.info/openssl-error-handling-apt-fips/?utm_source=mastodon&utm_medium=jetpack_social
hp z4 g4 is the go to but i have to do a bit more research, my cost will be 3500-4k, 1 k margin maybe, ongoing support/upsells/addons but not too much - the basics and focus is what it is all about - big mkt out there - with warm leads from splash/squeeze pages conversion rates go up #tls proxy #central logging #dashboards #arkime #structured data
Replying to
@djb@mastodon.cr.yp.to
They're also getting really testy about us "regular Joes" showing up and voting against publication of the deliberately-weak solo PQ recommendation.
You can practically feel their frustration - "We stuffed this list to pass this vote, and they're stuffing it against us!".
The blatant hypocrisy of the "not standards-track" thing bugged me too when it came through the list.
Anyone who follows me and cares about cryptography or their privacy: read djb's short blurb here:
https://nsa.2026.action.cr.yp.to/
There's action you can take to try to prevent the NSA's attempt to get the world to standardize on deliberately weakened cryptography in TLS - i.e. the thing that protects every important web connection on the planet. They have form for doing this in the past, and are trying again.
There are other links in the above page for more information.
#TLS #HTTP #HTTPS #cryptography #privacy
RE: https://mas.to/@nemo/116864001224955528
NSA involved in "off the rails" warrant-less mass surveillance. This (and the fact that their chain of command was purged by the Trump regime) should be factored into the debate around the IETF relying on the NSA's input.
If your position is that a simple RFC is "not a big deal" then IDK why you're making a big deal out of people like @djb@mastodon.cr.yp.to being against it.
#FISA #crypto #ietf #tls #pqc #privacy #surveillance
Call to act to reject draft-ietf-tls-mlkem-08 (Ends 2026-07-08)
https://nsa.2026.action.cr.yp.to/
#Security #Crypto #TLS