Still one of the best explanations about SELinux, that I know:
https://github.com/mairin/selinux-coloring-book/blob/master/PDF/en/selinux-coloring-book_A4-Stapled.pdf
#linux #selinux #learning
#selinux
6 posts · Last used Aug 08
Nur 2 von 100 #Linux-Distributionen sind tatsächlich sicher vorkonfiguriert: #Fedora und #openSUSE. In diesem Video (Englisch) wird es genauer erklärt.
https://redirect.invidious.io/watch?v=dt-YepVq9Es
#security #sicherheit #selinux #AppArmor
Neuer Tip im Blog :
Letztens haben wir den pod komplett automatisiert - als Service, mit auto-update. läuft. Nur auf Alma / Rocky / etc grätscht beim bind-mount dann SELinux dazwischen.
Der neue Quick-Tipp: bind-mount oder named volume, wie man das Label sauber setzt (chcon/semanage) - und warum das auf Debian mit AppArmor kein Thema ist.
https://just-stuff.blog/podman-bind-mount-selinux/
#Podman #SELinux #AppArmor #Debian #Linux #AlmaLinux #Blog
Neuer Artikel im Blog. :)
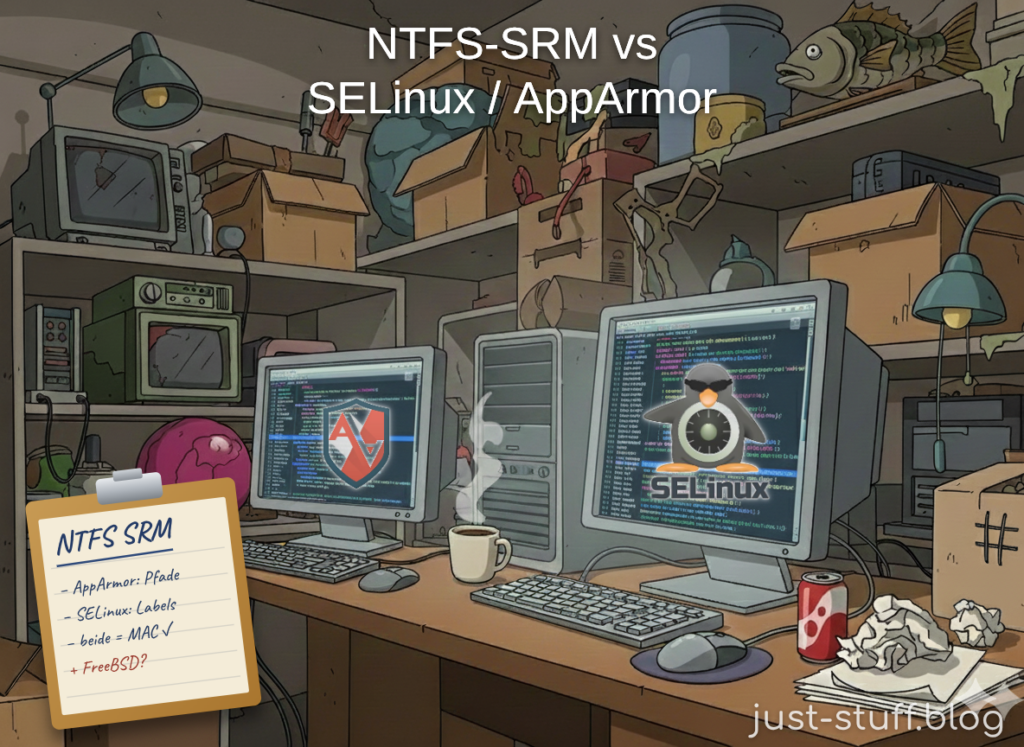
NTFS-ACL , SELinux und AppArmor: ACLs, SIDs und MIC auf Windows, Type Enforcement und Profile auf Linux – technischer Vergleich der Sicherheitsmodelle beider Betriebssysteme
https://just-stuff.blog/ntfs-srm-vs-selinux-apparmor-wer-darf-was-und-warum/
#acl #selinux #apparmor #security #blog #windows #linux
Stop running setenforce 0 and pretending SELinux doesn't exist.
I wrote a practical guide to actually working with SELinux on Fedora and RHEL: Contexts, booleans, troubleshooting denials, container volume labels, and the commands you'll actually use.
No policy theory rabbit holes. Just the stuff that gets you unstuck.
https://blog.hofstede.it/selinux-a-practical-guide-for-fedora-and-rhel/
#SELinux #Fedora #RHEL #Linux #sysadmin #infosec #itsec
You've seen all posts