Elektrine
EN
Log in Register
Paige Chat Timeline Gallery Friends Lists Email Drive DNS Resolver Domains VPN Kairo Nerve
Remote

Brian Clark

@deepthoughts10@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

#InfoSec #Cybersecurity #threatintel and Politics. I try my best.
Also @deepthoughts10@twitter.com

Searchable

0 Followers
0 Following
50 Posts
Joined November 05, 2022
Verified by Twittodon:
https://twittodon.com/share.php?t=Deepthoughts10&m=deepthoughts10@infosec.exchange
Find my toots:
Tootfinder
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 6d ago
Replying to @gayint@infosec.exchange
@gayint@infosec.exchange Seriously though, this is great. How do you decide which ASNs get put into the "Bulletproof" category?
1
1
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1w ago
Replying to @chrismerkel@infosec.exchange
@chrismerkel@infosec.exchange @BlueTeamCon@infosec.exchange I’ll be there! If I see you I’ll say hello.
1
1
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1w ago
Replying to @rmceoin@infosec.exchange
@rmceoin@infosec.exchange 🤪
1
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1mo ago
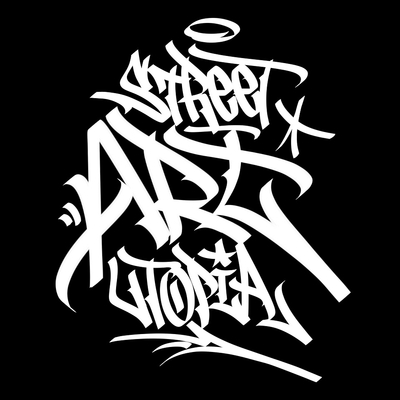
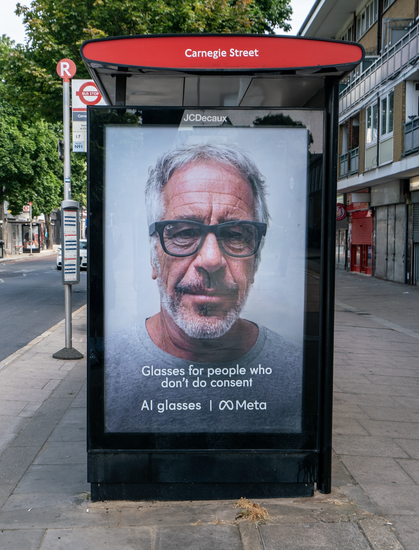
RE: https://mastodon.online/@streetartutopia/116999561247400940 Perfect timing! See my earlier posts on this topic #cybersecurity
Open quoted post
Quoting
Street Art Utopia
@streetartutopia@mastodon.online
The collective everyonehateselon_ made this in London, UK. 👾😆
Open quoted post
8
0
7
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @euroinfosec@infosec.exchange
@euroinfosec@infosec.exchange @GossiTheDog@cyberplace.social seriously though, I can see how it could be effective, using AI or standard data analytics tools. You could focus on the users who are using the most tokens, and/or search the logs for common keywords or patterns to, for example, see how often “compare” and “pdf” show up in the same prompt. But as Kevin says, you have to have people who have the time to do the analysis. Regarding tools that can log prompt use, many security and compliance tools are adding this functionality (which you may have to pay for) and may require technical integration before they work properly.
3
1
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 3mo ago
Replying to @WildEyedBoyFromFreecloud@masto.ai
@WildEyedBoyFromFreecloud@masto.ai @mattblaze@federate.social @GossiTheDog@cyberplace.social the Dark Blockchain already has AI 😉
4
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @spaf@mstdn.social
@spaf@mstdn.social hopefully not getting tacos at Taco Bell 🤢 https://www.usatoday.com/story/news/health/2026/07/15/taco-bell-pulls-ingredients-menu-cyclosporiasis-outbreak/90929207007/
1
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @badsamurai@infosec.exchange
@badsamurai@infosec.exchange @huronbikes@cyberplace.social I don’t get why companies stick with products from firms like Progress, Fortinet and Ivanti. How many times do they have to prove to us that they only do the bare minimum from a security perspective?
1
0
1
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @badsamurai@infosec.exchange
@badsamurai@infosec.exchange cool! Didn’t know about this one: Block (or limit) access to the login at dash.cloudflare.com. Especially if you are not a Cloudflare customer. This is a low-regret technique to reduce shadow cloud and dev sprawl on Cloudflare. #cybersecurity
1
1
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @badsamurai@infosec.exchange
@badsamurai@infosec.exchange @tek@freeradical.zone Thanks! My existing block of *.workers.dev already yeets this service into the void
1
1
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @iampytest1@infosec.exchange
@iampytest1@infosec.exchange @burritosec@infosec.exchange seems that this protection applies to uBlock Origin Lite users too!
1
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @cR0w@infosec.exchange
@cR0w@infosec.exchange @darkuncle@infosec.exchange and hopefully not “get the enhanced version of the product you already have with quantum-ready encryption for only $XXX per year”
1
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @lerg@infosec.exchange
@lerg@infosec.exchange all of them?
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1mo ago
Replying to @timb_machine@infosec.exchange
@timb_machine@infosec.exchange for most organizations I agree. Patch your Apps and OS and update relevant app libraries and frameworks (if you do custom software development) and you’ll be fine. In most cases, the software will automatically use the best available algorithms.
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @ifin@infosec.exchange
@ifin@infosec.exchange that sounds like a great idea! Not even joking a little bit.
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1mo ago
Happy to be at @BSidesLV@infosec.exchange #bsideslv
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1mo ago
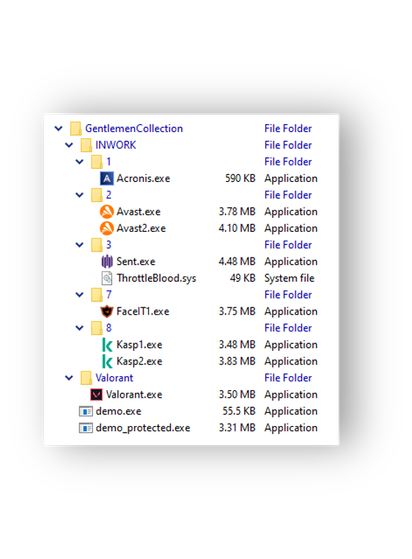
RE: https://infosec.exchange/@ESETresearch/116996496516280171 For defenders, take a look at the free https://loldrivers.io to build automatic detection capabilities for vulnerable driver use in your organization. To move to prevention, take a look at https://magicsword.io to help you create Windows Defender Application Control policies that prevent the execution of vulnerable drivers on your systems. #cybersecurity
Open quoted post
Quoting
ESET Research
@ESETresearch@infosec.exchange
In H1 2026, #ESETresearch continued tracking a growing number of #EDR killers, currently counting 100+ such tools. The dominant approach is still BYOVD, with 60+ of the EDR killers abusing legitimate yet vulnerable drivers. We expect those numbers to keep growing, as threat actors can weaponize any of thousands of available vulnerable drivers – some with public PoC exploits – while leveraging AI coding tools to adapt them, giving them a virtually endless supply. The report also details #ESETresearch findings from the Gentlemen leak. We found the gang uses a shared defense-evasion layer across its EDR killer suite – spanning in-house GentleKiller, third-party, and leaked tools – and can operationalize new BYOVD PoCs within days. While ransomware gangs are ramping up attacks (+50% YoY) only a minority of victims are willing to pay, with public reports putting that figure at just 14–28%. The total sum of ransom payments is also trending down, falling 8% from 2024 to 2025. For more on developments across the ransomware scene in H1 2026 – including gang infighting and successes in the fight against the gangs – read the full report: https://web-assets.esetstatic.com/wls/en/papers/threat-reports/eset-threat-report-h12026.pdf
Open quoted post
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Think I can still use these? 😉 I played a lot of coin-operated video games in my youth. #ChuckECheese #MalibuFunCenter
0
1
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1mo ago
RE: https://infosec.exchange/@SecureOwl/117032579489312068 FFS
Open quoted post
Quoting
Mike Sheward
@SecureOwl@infosec.exchange
ah yes crowdsourcing warcrimes
Open quoted post
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @paul_ipv6@infosec.exchange
@paul_ipv6@infosec.exchange @da_667@infosec.exchange @yala@degrowth.social @Viss@mastodon.social uBlock Origin Lite for Safari on iOS
0
1
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @tychotithonus@infosec.exchange
@tychotithonus@infosec.exchange @onewheelgeek@social.onewheelgeek.me Cloudflare's free offerings are heavily abused (workers.dev, pages.dev, r2.dev). They don't make it easy to get malicious content taken down either, which extends the time that content helps phishers and scammers -- and they seem proud of that fact. It's easy to block those .dev domains in most web security appliances or services these days. Just put the known good/user-requested URLs in a rule above your block rule. I've never had a problem doing that in my org. As for Telegram, I'm no fan of that either and it absolutely should be blocked on an enterprise network. That's not to say it has no legit use -- it absolutely does -- but control access to it to save headaches later on.
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
RE: https://infosec.exchange/@CDubbs/116847680945065797 Create a group called "Device Code Users" and a CA policy that blocks the use of the Device Code authentication flow except for those in the group. #cybersecurity #entraID
Open quoted post
Quoting
SIEM Shady
@CDubbs@infosec.exchange
EntraID PSA: Disable OAuth Device Code flow in your default conditional access policy. You can search sign-on logs for people using this method to baseline and manage exceptions where appropriate.
Open quoted post
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1mo ago
RE: https://infosec.exchange/@wdormann/117039138203111701 Many @defcon@defcon.social and @BSidesLV@infosec.exchange talks are recorded and eventually posted to YouTube. If you can’t make it, follow those accounts to get notified when they post the recordings.
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
RE: https://infosec.exchange/@jaythvv/116858665927371933 Unbelievable game! #worldcup
Open quoted post
Quoting
Jay Thoden van Velzen ⚽ ☁️​🛡️​:lolsob:
@jaythvv@infosec.exchange
Vozinha saves a proper Messi free kick from edge of the box BELIEVE ... ad break #ARGCPV #FIFAworldcup
Open quoted post
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 5mo ago
Replying to @carnage4life@mas.to
@carnage4life Anthropic loses a lot of money on each of their subscriptions—no matter the level of payment. They’ve got to figure out how to deliver their services more economically or they won’t make it. Same for all other AI companies.
0
0
1
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @onewheelgeek@social.onewheelgeek.me
@onewheelgeek@social.onewheelgeek.me @tychotithonus@infosec.exchange Regarding DDOS protect, did you know that Cloudflare protects both the DDOS attackers too? And they don’t care. I guess DDOS counts as free speech? Here’s one recent example: https://www.webpronews.com/cloudflares-dual-role-in-the-ubuntu-ddos-crisis-protection-or-pressure/
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Yuck #canadawildfires #smoke
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 5mo ago
Replying to @gumnos@mastodon.bsd.cafe
@gumnos it’s a niche joke but I’ll allow it 😉
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1mo ago
RE: https://infosec.exchange/@DarkWebInformer/116999813453991351 I’ve been waiting for this to be published …. #cybersecurity
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Saturday #bloomscrolling in Lake Geneva, WI
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @GossiTheDog@cyberplace.social
@GossiTheDog@cyberplace.social I’m starting to see some companies log all AI prompts and review them to see what people are using AI to do. The ones I’ve seen do this are positioning it as a way to discover additional training opportunities for their staff — to train them that they gave other, better tools to compare PDFs, for example. It makes sense if you have the tools and resources to put together this kind of analysis.
0
1
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @paul_ipv6@infosec.exchange
@paul_ipv6@infosec.exchange @yala@degrowth.social @Viss@mastodon.social @da_667@infosec.exchange uBlock Origin Lite is available for Safari
0
1
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Saturday #bloomscrolling in Lake Geneva, WI
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1mo ago
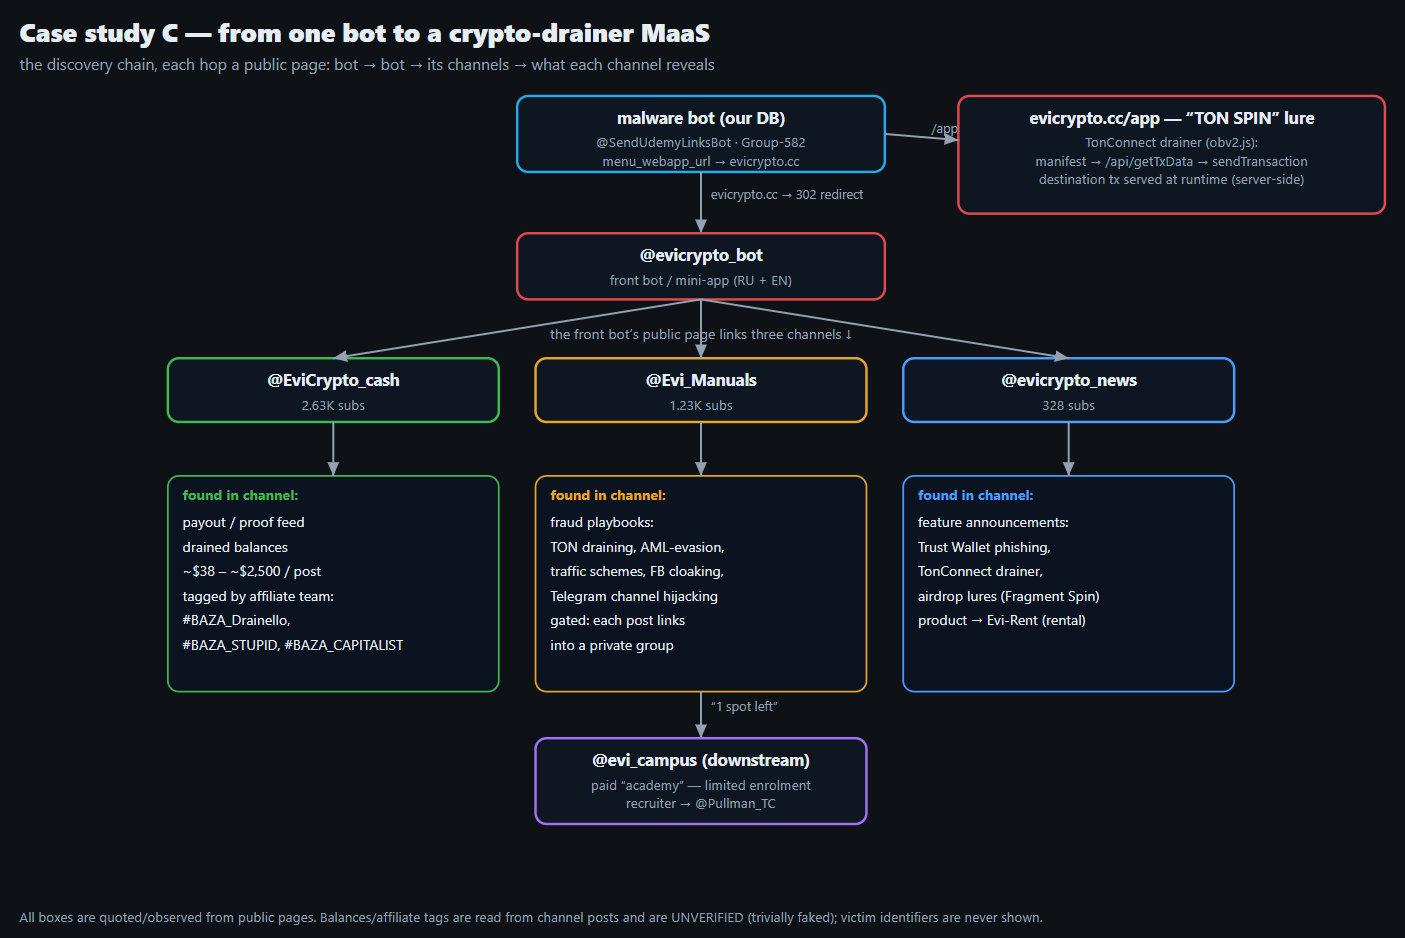
RE: https://infosec.exchange/@VirusBulletin/116996988073045096 This is exactly why you should block access to Telegram from business networks. It’s too risky. If you have users that want or need it, create a Wi-Fi network that only has access to the Internet (no internal network access) to which they can connect their smartphones. #cybersecurity
Open quoted post
Quoting
Virus Bulletin
@VirusBulletin@infosec.exchange
Ransom-ISAC examines Telegram's role in the malware ecosystem. Its Bot API gives malware authors a free, TLS-protected, globally reachable message bus, with no infrastructure to rent, no domain to burn, and no certificate to manage. https://ransom-isac.org/blog/the-telegram-malware-ecosystem/
Open quoted post
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1mo ago
RE: https://defcon.social/@defcon/116993849606697118 DEF CON doesn’t want you wearing Meta glasses to their events either. Please just don’t. #cybersecurity
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1mo ago
Replying to @Shdwdrgn@tech.lgbt
@Shdwdrgn@tech.lgbt @maunzCache@ruhr.social @arstechnica@mastodon.social their position is that once you get local admin, you’ve already crossed their security boundaries.
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @jadevol@mastodon.world
@jadevol@mastodon.world same here in Northern Illinois 😷
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @devopscats@toot.cat
@devopscats@toot.cat that’s a quality day!
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @cenobyte@mastodon.thirring.org
@cenobyte@mastodon.thirring.org @mttaggart@infosec.exchange @thedarktangent@defcon.social https://defcon.social/@thedarktangent/116823710775702749
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @mttaggart@infosec.exchange
@mttaggart@infosec.exchange @simonzerafa@infosec.exchange @ifin@infosec.exchange working on a better set of uBlock rules or an actual extension? I would think a ruleset would be better because if you got the uBlock maintainers to adopt it, it would be pushed out to millions.
0
1
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @ddayen.bsky.social@bsky.brid.gy
@ddayen.bsky.social that’s a hot take if if ever heard one 😂
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @tychotithonus@infosec.exchange
@tychotithonus@infosec.exchange @onewheelgeek@social.onewheelgeek.me I agree with many of your points and second Royce’s opinion on this being a thoughtful analysis. I also want to point out something about Cloudflare that is different than most other hosting providers—they do not have relationships with the security community. Most companies (even Microsoft!) have developed trusted relationships with the people and organizations that secure the Internet. When they receive information from those entities about malware of phishing content being hosted, they immediately suspend the account or at least suspend access to the reported content. They feel comfortable doing this because of the trust that has been built up over time (the last XXXX number of submissions received have proven to be valid.) But Cloudflare won’t do that. They make every submission meet a high bar of evidence before taking any action. That sounds nice, but it doesn’t scale and results in malware and malicious content staying up for extended periods of time. That causes real harm to ordinary people who just want to use the internet without being scammed.
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @badsamurai@infosec.exchange
@badsamurai@infosec.exchange notice the url redirect on this cred stealer page goes to a domain already on the Geoshitties list!
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @siliconshecky@infosec.exchange
@siliconshecky@infosec.exchange I’ve read or listened (audiobooks) to all of them. It’s quite a trip!
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1mo ago
RE: https://mastodon.social/@zackwhittaker/117039173900529368 Maybe @wdormann@infosec.exchange was right about not using apps and only using websites #cybersecurity
Open quoted post
Quoting
Zack Whittaker
@zackwhittaker@mastodon.social
An EFF investigation has found that some advertising SDKs enable location data collection by default. The findings aim to warn app developers that some of the third-party code they place in their apps may also collect their users’ location data when they grant permission to the app. More: https://www.eff.org/deeplinks/2026/07/developers-beware-ad-libraries-betray-your-users-location-privacy
Open quoted post
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @mttaggart@infosec.exchange
@mttaggart@infosec.exchange see @thedarktangent@defcon.social recent post on the difficulties of hosting email and VPN services.
0
1
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @ashok@mstdn.ca
@ashok@mstdn.ca @SwiftOnSecurity@infosec.exchange I’ve never even seen one of these before
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 2mo ago
Replying to @blowdart.me@bsky.brid.gy
@blowdart.me I think Trump invited them here 😡
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1mo ago
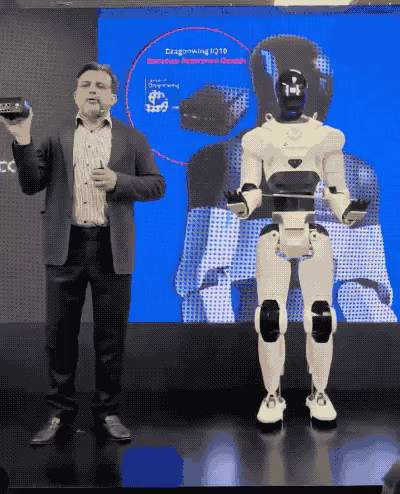
RE: https://mastodon.social/@zackwhittaker/116986783278293072 OMG the collapsing robot is spot on for this tech right now #cybersecurity
Open quoted post
Quoting
Zack Whittaker
@zackwhittaker@mastodon.social
Also: A bunch of data breaches that you might've missed, why paying a hacker's ransom can be a costly mistake, the Clop extortion gang appears to be back, and come and find out why wrench attacks are called that. Plus: Come for the collapsing robot, stay for the brand-new reader-submitted cyber cat. More: https://this.weekinsecurity.com/this-week-in-security-july-26-2026-edition/ Please share! 🐈‍⬛
Open quoted post
0
0
0
0
Open post
Brian Clark @deepthoughts10@infosec.exchange
· 1mo ago
Replying to @defcon@defcon.social
@defcon@defcon.social nice 👍
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)
  • Source code

Legal

  • Terms of Service
  • Privacy Policy
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 16:26:15 UTC