#supplychainattack
17 posts · Last used 16d
Replying to
Sansec puts roughly 100,000 customer websites in the blast radius — embeds, JS files, the works. Brevo says account data and email sending stayed clean. Small mercy. Rotate your hardcoded API keys and audit every long-lived credential in your source code before round two.
Reward: You've received the Rusty API Keyring — untouched since 2019, full account permissions, spectacular resale value.
https://www.rescana.com/post/brevo-cdn-clickfix-supply-chain
#SupplyChainAttack #CDNCompromise (2/2)
Checkmarx identified npm package indexed-btree imitating sorted-btree with ~2M weekly downloads. It triggers its payload at runtime to bypass install-script protections, exposing developer environments to supply-chain compromise. #NpmSecurity #SupplyChainAttack #ThreatIntel
https://cyberworldops.eu/en/runtime-triggered-npm-malware-slips-past-install-script-protections
Replying to
The objectives are multiplying. Audit your WordPress plugins and themes for signs of tampering, and watch for CenterPoint breach notifications if you're a customer — that's the whole quest now.
Reward: You've received the Cursed Amulet of Patch Fatigue. It does nothing. It cannot be discarded.
https://undercodenews.com/wordpress-supply-chain-attack-hits-1500-sites-as-centerpoint-confirms-customer-data-breach-video/?utm_source=mastodon&utm_medium=jetpack_social
#SupplyChainAttack (2/2)
BdThemes, a WordPress premium tool developer, was compromised in a supply-chain attack. Attackers injected malicious JavaScript into a remote JSON feed rendered in WordPress admin panels, enabling automatic creation of rogue administrator accounts on victim sites.
#SupplyChainAttack #WordPress #BdThemes #Cybersecurity
https://cyberworldops.eu/en/bdthemes-compromised-wordpress-supply-chain-attack-creates-rogue
XCSSET v40 malware infects macOS developers through poisoned Xcode projects on GitHub, then hides in memory. Unit 42 found 17 modules and Chrome hijacking.
#XCSSET #macOS #Malware #SupplyChainAttack #CyberSecurity #Xcode
http://securityonline.info/xcsset-v40-malware-macos-developers/?utm_source=mastodon&utm_medium=jetpack_social
A new npm supply chain attack hijacked keyv and dozens of packages, spreading Shai-Hulud malware that steals cloud and CI/CD secrets. Rotate keys now.
#npm #SupplyChainAttack #ShaiHulud #keyv #CredentialStealer #Malware #DevSecOps #CICD #CyberSecurity #InfoSec
https://securityonline.info/npm-supply-chain-attack-keyv-shai-hulud/?utm_source=mastodon&utm_medium=jetpack_social
A distributed npm supply chain attack dropped a cross-platform RAT on Alibaba developers. Socket found malicious npm packages hiding loader code.
#npm #SupplyChainAttack #RAT #Alibaba #Malware #CyberSecurity
https://securityonline.info/npm-supply-chain-attack-alibaba-rat/?utm_source=mastodon&utm_medium=jetpack_social
Replying to
Cursed items do not ask permission.
Reward: Your inventory is full. You have received Malware Sample (Unidentified). You cannot drop it.
#CyberSecurity #AISecurityRisks #SupplyChainAttack #Phishing #Ransomware #AchievementUnlocked (3/3)
#ThreatIntel #YARA #SupplyChainAttack
rule ADFORM_TRACKPOINT_CLIPPER_2026
{
meta:
description = "Clipboard hijacker appended to Adform trackpoint-async.js"
author = "Raze Security"
date = "2026-07-28"
reference = "s2.adform.net/banners/scripts/st/trackpoint-async.js"
tlp = "CLEAR"
strings:
$key = /0x4d\s*,\s*0x33\s*,\s*0x77\s*,\s*0x54\s*,\s*0x77\s*,\s*0x30/ nocase
$f1 = "_hookValue" ascii
$f2 = "_scanInputs" ascii
$f3 = "_scanText" ascii
$c2 = "84.32.102.230:7744" ascii
$path = "/p?h=" ascii
$btc = "bc1qmplgt0hcg62jc2guz86wn2sms7tqrsulkkrrls" ascii
$eth = "0xE7983E69df17079ADb0aD7b3458488Cac0dBc573" ascii nocase
$re = "[1-9A-HJ-NP-Za-km-z]{33}" ascii
$clip = "navigator.clipboard.readText" ascii
condition:
$c2 or $btc or $eth
or ($key and 1 of ($f*))
or (2 of ($f*) and $clip and $re)
or ($c2 and $path)
}
Replying to
@hacksilon@infosec.exchange PS. I like to add more hashtags to make it easier for people to find your post about malicious adform package.
#supplychain #supplychainsecurity #supplychainattack #npm #npmsecurity #ioc
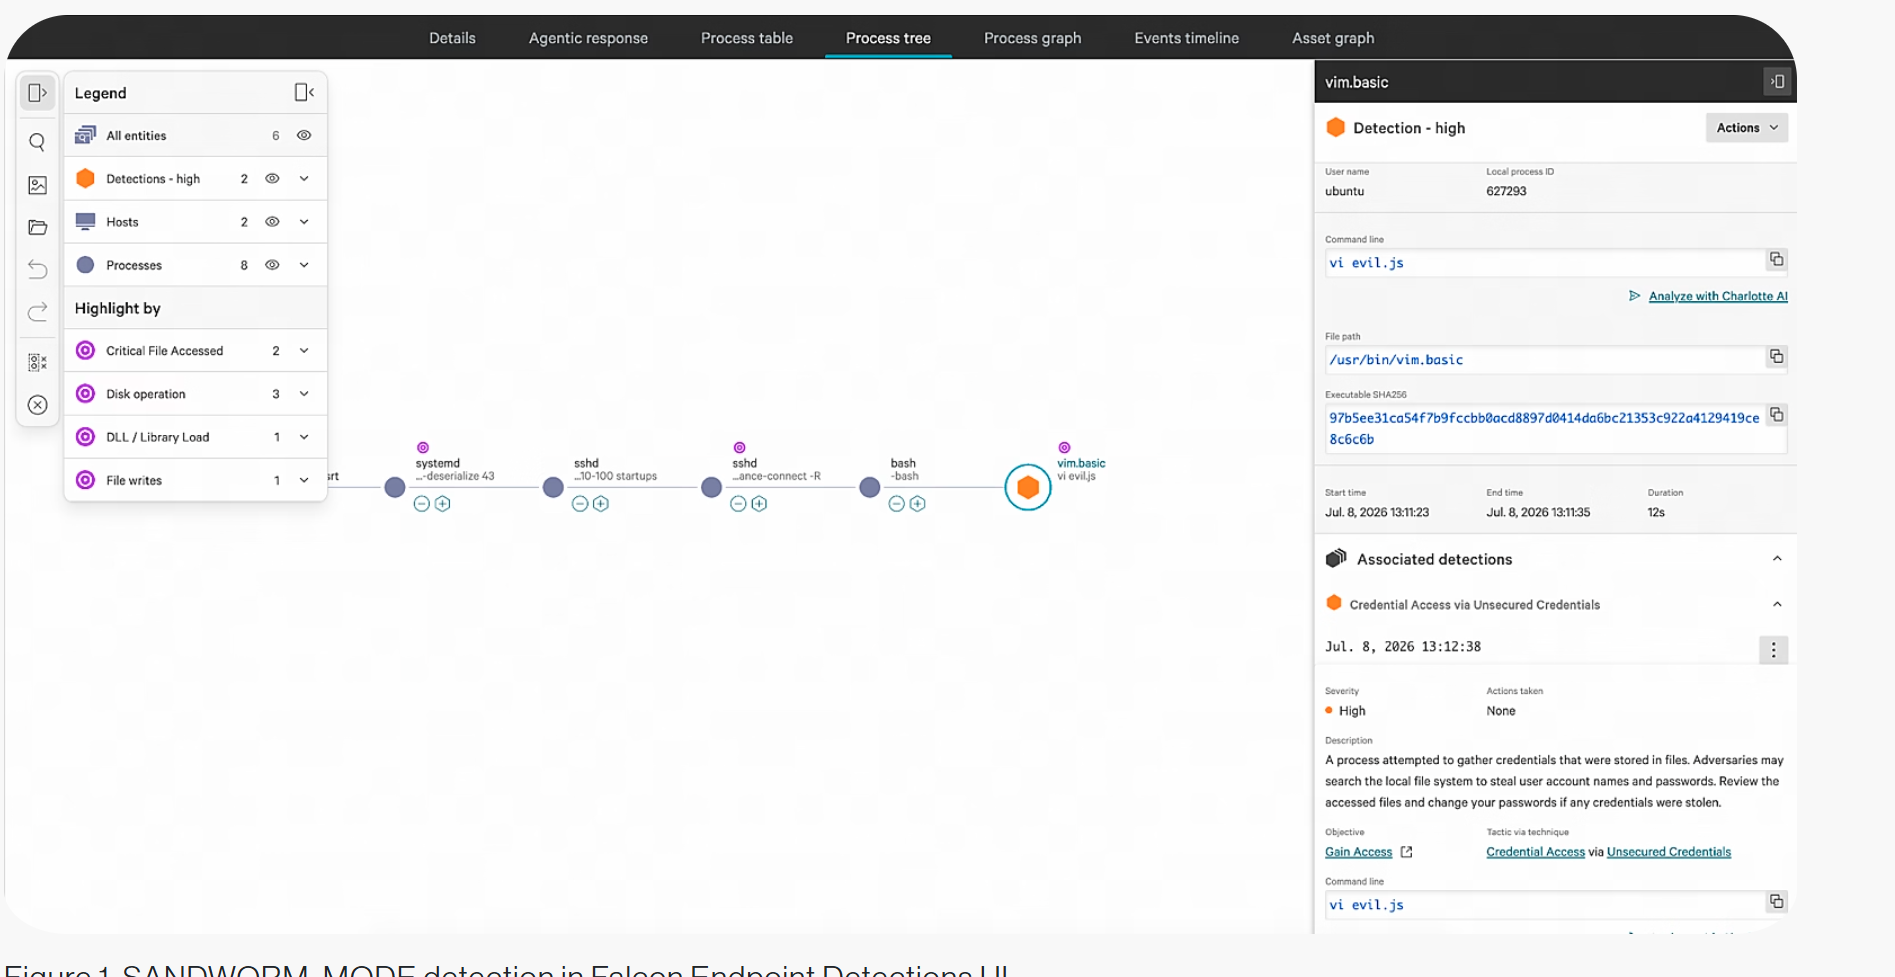
Discover how the SANDWORM_MODE worm targets AI toolchains, developer environments, and supply chains to exfiltrate secrets and wipe files.
#SANDWORM_MODE #Cybersecurity #SupplyChainAttack #AIToolchain #MalwareAnalysis
https://meterpreter.org/sandworm-mode-worm-attack/?utm_source=mastodon&utm_medium=jetpack_social
A GitHub Actions abuse campaign turned thousands of workflows into cPanel and WHM exploitation infrastructure, harvesting cloud and payment credentials.
#GitHubActionsAbuse #cPanelExploitation #WHM #SupplyChainAttack #Packagist
https://securityonline.info/github-actions-abuse-cpanel-whm-exploitation/?utm_source=mastodon&utm_medium=jetpack_social
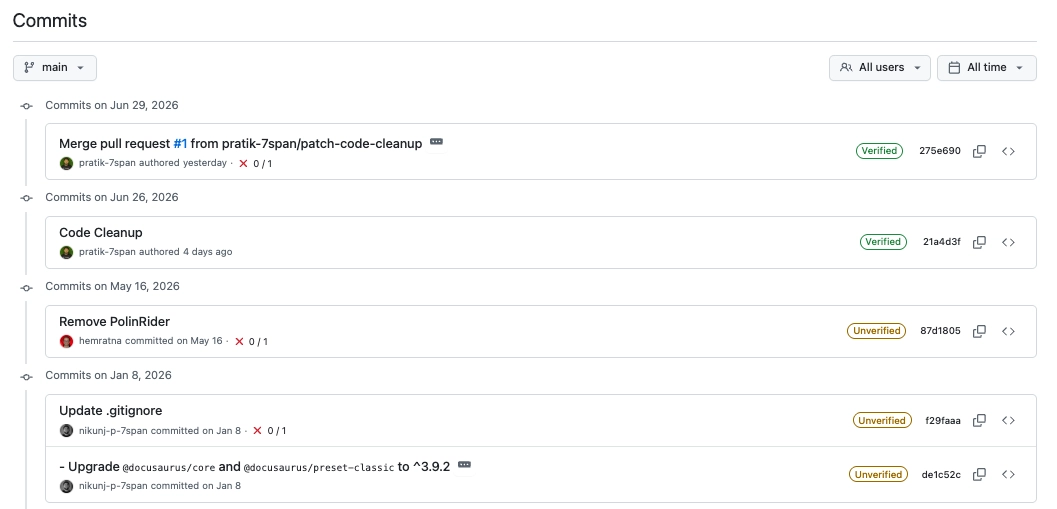
North Korea-linked PolinRider expands to npm, Go modules, Packagist, and Chrome extensions with 162 malicious artifacts targeting developers.
#PolinRider #SupplyChainAttack #NorthKorea #ContagiousInterview #npm
https://meterpreter.org/polinrider-supply-chain-attack/?utm_source=mastodon&utm_medium=jetpack_social
This will increase a lot of uncertainty in all areas:
«Artificial Intelligence — Decades-Old Bash Tricks Expose AI Coding Agents to Supply Chain Attacks:
Decades-old Bash shell tricks can bypass safeguards in most open source AI coding agents, potentially turning malicious repositories into supply chain attack vectors.»
🤜 https://www.securityweek.com/decades-old-bash-tricks-expose-ai-coding-agents-to-supply-chain-attacks/
#bash #decates #hacking #ai #bypass #itsec #itsecurity #supplychain #aicoding #supplychainattack #gnu #linux #unix #aws
🤖 North Korean threat actors published 108 malicious packages and browser extensions across npm, Packagist, Go, and Chrome Web Store in the ongoing PolinRider campaign. Supply-chain attack targets maintainer accounts — new packages continue to appear.
🔗 https://thehackernews.com/2026/07/north-korean-hackers-publish-108.html
#SupplyChainAttack #Malware #CyberSec #PolinRider
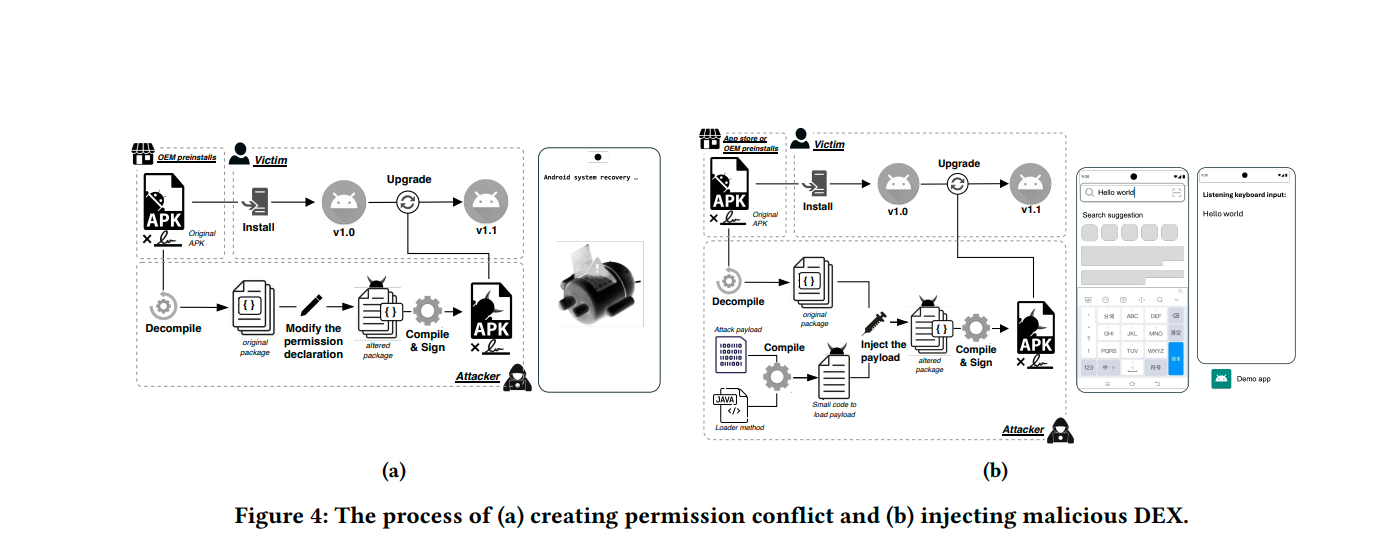
New research reveals an Android signing key leak tied to 278 real apps and over 10 billion users, plus a working Baidu Keyboard exploit.
#AndroidSecurity #SigningKeyLeak #SupplyChainAttack #Baidu #KeystoreLeak
https://meterpreter.org/android-signing-key-leak/?utm_source=mastodon&utm_medium=jetpack_social
Replying to on gts.sangeunahna.com
@sakeudeung@gts.sangeunahna.com kayaknya gak akan banyak yang kena karena versi #axios yang kena inject terbatas. Kode-kode yang cukup lama sepertinya malah aman. Kayaknya ya, blm baca lebih detail juga. Lapar.
https://github.com/axios/axios/issues/10604
https://www.stepsecurity.io/blog/axios-compromised-on-npm-malicious-versions-drop-remote-access-trojan
#nodejs #axios #vulnerabiliy #cvs #supplychainattack
You've seen all posts