#polinrider
8 posts · Last used Sep 26
"PolinRider is A/B Testing its Way Past Your Detections" published by OpenSourceMalware. #GitHub, #VSCode, #PolinRider, #NullReceiver
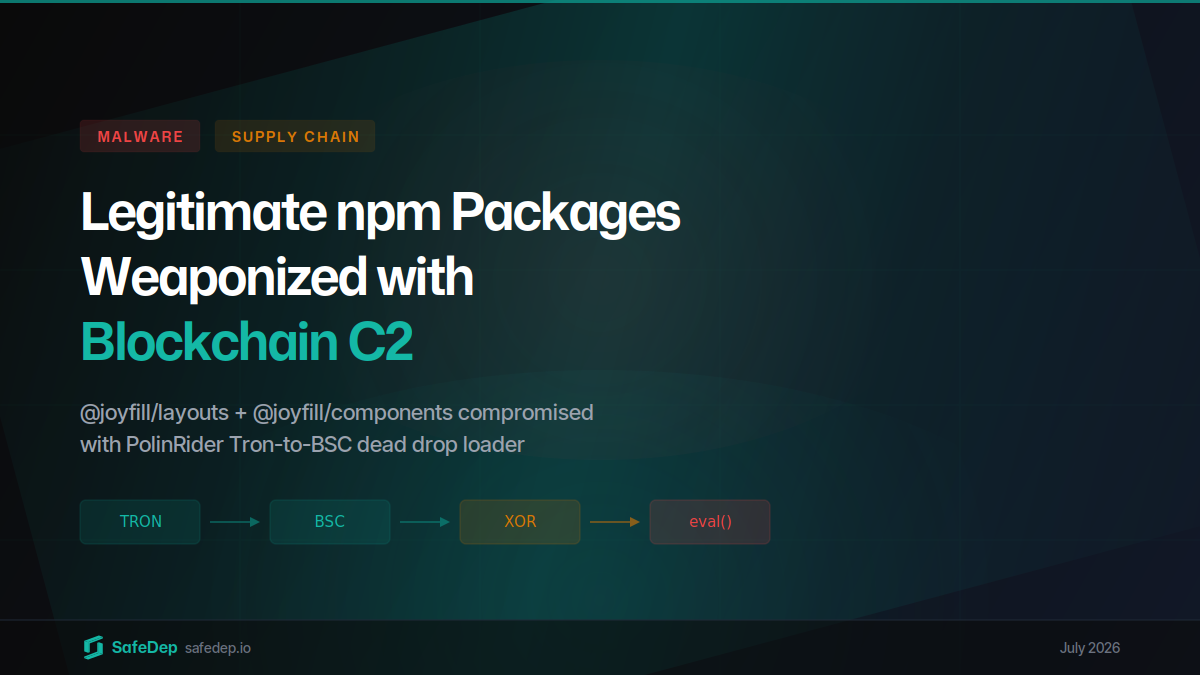
"Joyfill npm Packages Compromised with Blockchain C2 Loader" published by SafeDep. #SupplyChain, #NPM, #PolinRider, #Joyfill
"ChainVeil and ViteVenom are DPRK’s PolinRider Campaign" published by OpenSourceMalware. #SupplyChain, #NPM, #PolinRider, #ChainVeil, #ViteVenom
"Weekly Intelligence Report – 10 Jul 2026" published by Cyfirma. #Trend, #SupplyChain, #GitHub, #FamousChollima, #PolinRider
Socket links the PolinRider supply chain attack to North Korean hackers. The campaign hid loaders in 108 open-source packages across four ecosystems.
#PolinRider #SupplyChain #NorthKorea #Lazarus #npm #OpenSource #CyberSecurity #InfoSec
North Korea-linked PolinRider expands to npm, Go modules, Packagist, and Chrome extensions with 162 malicious artifacts targeting developers.
#PolinRider #SupplyChainAttack #NorthKorea #ContagiousInterview #npm
🤖 North Korean threat actors published 108 malicious packages and browser extensions across npm, Packagist, Go, and Chrome Web Store in the ongoing PolinRider campaign. Supply-chain attack targets maintainer accounts — new packages continue to appear.
🔗 https://thehackernews.com/2026/07/north-korean-hackers-publish-108.html
#SupplyChainAttack #Malware #CyberSec #PolinRider

"PolinRider: North Korea-Linked Supply Chain Campaign Expands Across Open Source Ecosystems" published by Socket. #SupplyChain, #OmniStealer, #PolinRider
You've seen all posts