MetaCPAN @metacpan@fosstodon.org now displays security advisories when you are viewing a module with advisories.
Remote
"Mutant Rob" Robert Rothenberg
@rrwo@infosec.exchange
 mastodon 4.8.0-alpha.3+glitch
I was born on the Moon but kidnapped by astronauts and raised in the suburbs of Grumman. Eventually, I drifted along the Gulf Stream to Northern Europe.
0 Followers
0 Following
30 Posts
Joined April 22, 2025
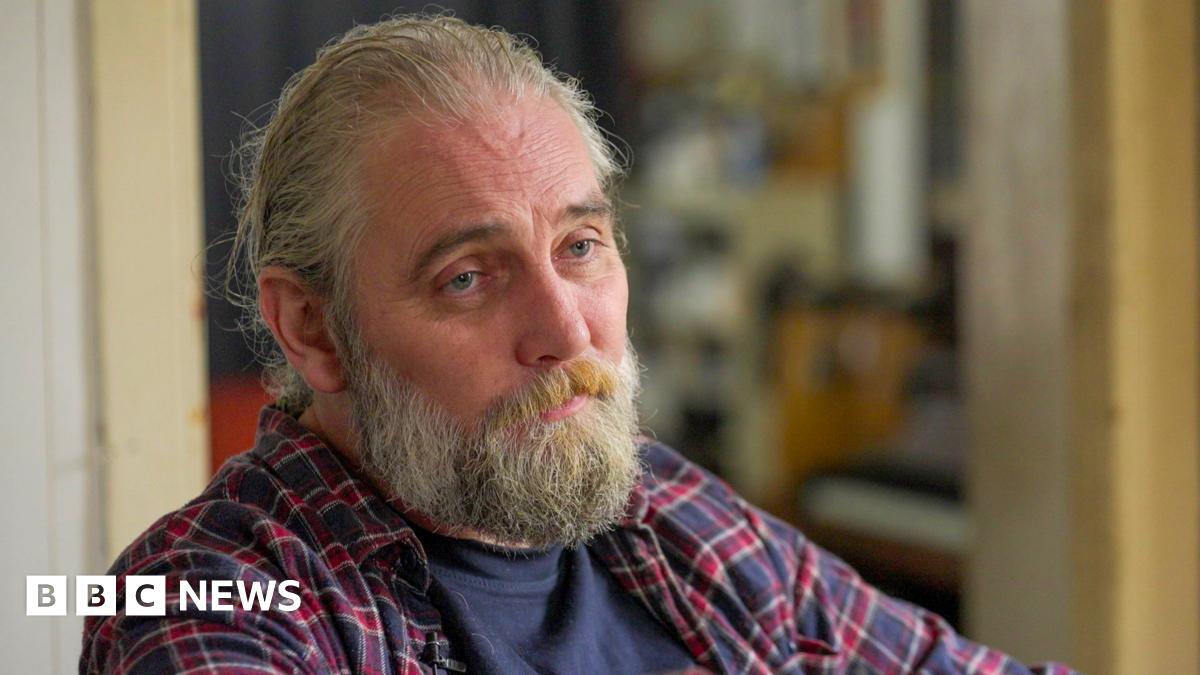
"Musk's AI told me people were coming to kill me. I grabbed a hammer and prepared for war"
Adam is one of 14 people the BBC has spoken to who have experienced delusions after using AI. They are men and women from their 20s to 50s from six different countries, using a wide range of AI models.
https://www.bbc.co.uk/news/articles/c242pzr1zp2o
In case you know of someone caught up in LLM mania https://www.thehumanlineproject.org/

I've uploaded a new version of Plack-App-Prerender to #CPAN
This is a #Plack #Perl application for a pre-rendering proxy using Chrome.
This version fixes a potentially critical security issue, so if you use it, please upgrade ASAP.
https://metacpan.org/release/RRWO/Plack-App-Prerender-v0.3.0
So Google decides to rebrand and change the app icons again... and I will be confused for a few days because marketing is more important than usability.
@lucydev Saying AI democratises art, writing or programming is like saying that a chef democratises cooking, or a maid democratises house cleaning.
Replying to
@kimcrawley @davidgerard
The shoe event horizon pivots to AI.
It's 2026 and the solution to many software issues is still "make backups, erase all of the data and reinstall".
The @cpansec@fosstodon.org CPAN Author's Guide to Random Data for Security has been updated.
https://security.metacpan.org/docs/guides/random-data-for-security.html

There's nothing like starting service with a new company only to receive an email threatening to cancel service within 48 hours because if a payment problem.
Bonus: the billing link is at a different website than the company, so it makes one wonder if it's a very good phishing attempt because your name, email and invoice number might be have been leaked.
Extra Bonus: clicking on the link shows an error message that the payment is being processed.
Double-Plus-Ungood Bonus: calling customer service gets a recorded message that they are very busy so please email instead and then it hangs up.
I should add that none of this was by choice. My ISP decided to "exit the market" and transferred service to another provider.
Nothing like losing 10-20 minutes of your time to a corporation's fuck up.
#TIL that
both My Neighbor Totoro and Grave of the Fireflies were released on the same bill in 1988. The dual billing was considered "one of the most moving and remarkable double bills ever offered to a cinema audience".
https://en.wikipedia.org/wiki/My_Neighbor_Totoro#Releaae
I'm not sure that I could have watched both films in the same sitting.
Are you still using the 2-argument open?
(A short post on @cpansec@fosstodon.org by me.)

The tech industry habit of asking"Do you consent? Yes or Maybe Later" started in the 1990s with web browsers complaining that they weren't the default app.
Replying to
@rfc1036@hostux.social
I don't know any developers who believed they could "do without" sysadmins. I know of many who did both roles because their teams were too small to differentiate. (And sometimes that was due to managers who have probably moved on to vibe coding....)
There's nothing more that a "full stack developer" wants to do than drop a software project for a couple of days while they diagnose problems with a samba share only to end up replacing a faulty network card and oh wait where was I with that project....
But DevOps originally meant applying software development techniques to operations: repeatable system deployment and configuration by scripts that are kept in version control, with tests. (It makes sense when you're an op in charge of a data centre with dozens, maybe hundreds or thousands of machines.)
Replying to
Vulnerabilities in the #Perl JSON::XS, Cpanel::JSON::XS and JSON::SIMD modules via @cpansec@fosstodon.org
If you have applications that handle JSON from untrusted sources (e.g. a web API), then you need to upgrade.

A variation of the "make money by not doing what we promised the customer and hope they give up on calling customer service after several tries" business steategy is the "pretend we never received the payment" strategy.
I've wasted two hours fighting with one company about this.
"We bill for the previous month. You owe for January."
"Yes, I paid you in February."
"No, that was the previous month."
"No, December was paid. The bill for January says so. And several weeks ago one of your colleagues told me that everything was all paid."
"But we can't find the payment"
"My bank says you received it. Here is the confirmation..."
"But...."
It goes in circles.
This is for a fairly small amount. Out of principle I won't re-pay it. But they are more than willing to spend infinite amounts of employee time to retrieve it. So it's a battle of wills.
I got fed up, and asked for an email address instead of sitting on the telephone.
And this seems to be with actual human beings. I'm loathing to think what will happen if the company replaces employees with LLMs. But maybe it will be easier to convince an LLM that they should compensate you for the trouble.
CVE-2025-40925: Starch versions 0.14 and earlier generate session ids insecurely
https://lists.security.metacpan.org/cve-announce/msg/32910601/
I came across a bug report that I filed 20+ years ago for some software... and I don't remember what that software even did. I don't use it anymore.
It seems that the residential proxies have shifted to using Dominican IP addresses for the past few days.
I guess when they've destroyed the online reputation of one country, they need another to trash.
Replying to
@petergleick
People will describe things as a "musk up"
Replying to
@maehw an "exe" TLD would make life miserable for a lot of people.
What's worse than an inconsistent API?
How about one that doesn't behave as documented?
What's worse than that?
Getting AI slop response from support that ignores the question and refers to the incorrect documentation.
Edit: I suspect the API and the docs have been written by "AI".
I've uploaded a new #Perl module to #CPAN https://metacpan.org/release/RRWO/Dist-Zilla-Plugin-AutomationPolicy-v0.1.1
I received one of my favourite* kind of bug report emails today. The entire message was:
"The website doesn't work"
Why it's obvious. I'll fix that error right away.
- Not really but it's Thursday and I want to seem cheerful.
I have a question about potential #Perl search modules to use.
Search::Xapian is no longer being actively maintained.
Lucy is retired.
Are there good replacements?
Back in April the #Perl NOC turned off the #CPAN mail forwarding.
https://log.perl.org/2026/04/cpanorg-email-forwarding-has-been-shut.html
If you're like me, you've been using that for 25+ years, and it's everywhere (and unfortunately that includes spammer lists).
Here's what you can do in the meantime, via @timlegge@mas.to @cpansec@fosstodon.orghttps://security.metacpan.org/2026/06/14/cpan.org-email-forwarding-shutdown.html
I've taken over maintenance of Catalyst::View::Wkhtmltopdf, and released a new version with a security fix, among other changes.
This is a view that returns a PDF instead from a HTML template.
https://metacpan.org/release/RRWO/Catalyst-View-Wkhtmltopdf-v0.6.0
Note that #wkhtmltopdf is no longer maintained. This module will soon be deprecated.
#Perl #Catalyst #CPAN
Catalyst::View::Wkhtnltopdf new version uploaded to #CPAN with documentation and bug fixes
https://metacpan.org/release/RRWO/Catalyst-View-Wkhtmltopdf-v0.6.3
#Perl #Catalyst
Replying to
@pndc@social.treehouse.systems
Open source is great because you can keep abandoned projects alive.
But that means somebody has to keep them alive.
For a small organisation with limited resources, relying on abandoned projects is risky because they can't spare the people and time and funds to be the primary custodians.