Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Michael Koerfer

@OT_MacDonald@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Human, anti-fascist, craftsman, whitehat, team science...

24 Followers
25 Following
8 Posts
Joined April 27, 2025
Pronoun::
Human or they/them
Location::
Hidden Meadow
Language::
GER|EN
Open post
Michael Koerfer @OT_MacDonald@infosec.exchange
· 2mo ago

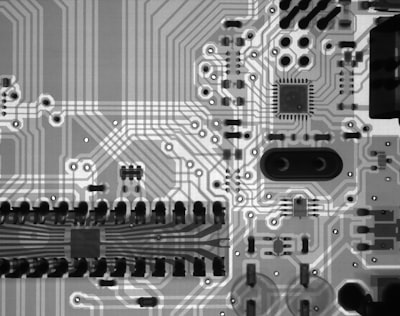
Powerful Hardware Turned into E-Waste

What you're looking at is another unfortunate example of perfectly capable hardware becoming electronic waste long before its technical lifespan is over.

This is the AirTies Air 4960, an AX5400 Wi-Fi 6 mesh extender/access point featuring impressive hardware:

  • Broadcom BCM6752 triple-core ARM Cortex-A7 SoC (up to 1.5 GHz)
  • Broadcom BCM43684 4x4 Wi-Fi 6 radio with 160 MHz channel support
  • Dual-band Wi-Fi 6 (802.11ax)
  • Two Gigabit Ethernet ports
  • Around 4.5 W power consumption

From a technical perspective, this device is still more than capable of delivering excellent performance in many home and enterprise networking scenarios.

  • The Real Issue

The hardware isn't obsolete, the software ecosystem is intentionally locked down.

Many devices like this are heavily restricted by manufacturers or Internet Service Providers (ISPs), preventing owners from repurposing them once official support ends or the service contract expires.

Meanwhile, open-source firmware projects such as OpenWrt, DD-WRT and Tomato have demonstrated for years that networking hardware can remain secure, functional, and useful far beyond its commercial lifecycle.

Unfortunately, locked bootloaders, proprietary firmware, missing documentation, and closed-source drivers often make that impossible.

Sustainability Is Also About Software Freedom

We regularly discuss sustainability, circular economy, and reducing electronic waste.

Yet perfectly functional networking equipment ends up in recycling bins, not because the hardware has failed, but because users are prevented from installing alternative software.

  • The hardware already exists.
  • The raw materials have already been mined.
  • The manufacturing energy has already been spent.

In many cases, all that's missing is the freedom to install an alternative operating system.

  • A Better Approach

I would like to see manufacturers embrace a more open ecosystem by providing:

  • Unlockable bootloaders
  • Public hardware documentation
  • Support or at least tolerance for open-source firmware
  • Longer software support lifecycles

This would benefit users, enterprises, developers, the open-source community, and ultimately the environment.

Not every retired device is obsolete, many are simply made obsolete through artificial restrictions.

#OpenSource #OpenWrt #DDWRT #WiFi6 #Networking #Sustainability #CircularEconomy #RightToRepair #EmbeddedLinux #Broadcom #eWaste #Technology
24
4
21
0
Open post
Michael Koerfer @OT_MacDonald@infosec.exchange
· 3mo ago
1
0
0
0
Open post
Michael Koerfer @OT_MacDonald@infosec.exchange
· 2mo ago
U-Boot, a widely used open-source bootloader, is reported to contain six security vulnerabilities that allow attackers to run malicious code or crash devices during the boot process. The flaws are in the Flattened Image Tree (FIT) signature verification mechanism, which ensures that only trusted firmware images load. Because the vulnerabilities trigger before the operating system starts, they can bypass standard security protections and allow for persistent malware setup. https://beyondmachines.net/event_details/u-boot-bootloader-flaws-allow-stealthy-pre-boot-code-execution-b-d-7-x-u/gD2P6Ple2L #openwrt #cybersecurity #tplink #glinet
U-Boot Bootloader Flaws Allow Stealthy Pre-Boot Code Execution
BeyondMachines

U-Boot Bootloader Flaws Allow Stealthy Pre-Boot Code Execution

Binarly researchers discovered six vulnerabilities in the U-Boot bootloader's FIT signature verification process that allow for arbitrary code execution and denial of service. These flaws affect over 50 stable releases since 2013 and can be exploited to install persistent firmware malware.

0
0
0
0
Open post
Michael Koerfer @OT_MacDonald@infosec.exchange
· 2mo ago
And please, everyone, patch or upgrade your kernels.... https://cybersecuritynews.com/linux-patches-400-kernel-vulnerabilities/ https://lore.kernel.org/linux-cve-announce/ #kernel #linux #linuxkernel
cybersecuritynews.com
0
0
0
0
Open post
Michael Koerfer @OT_MacDonald@infosec.exchange
· 2mo ago
When asked when I’ll be attending #BlackHat, #DEFCON, #BSidesLV, or a #SANS event, my answer is: probably never. It’s not for lack of desire, quite the opposite; I would love to attend. The simple reason is that I am the sole breadwinner supporting my family, and I finance these trips and conferences, as well as my lab and research, entirely out of my own pocket, all while having to take vacation time to attend. Consequently, I have to choose very carefully which events to attend and plan them well in advance. Spontaneous trips are rarely an option for me. Of course, I’m aware of the argument that my company benefits from this, too. That is true, just as they benefit from many of my other activities. However, there is no willingness on their part to contribute financially or organizationally. Instead, there are usually "good reasons" why it isn't possible. That is the reality. Nevertheless, I continue to invest in my #professionaldevelopment because it matters to me.
0
0
0
0
Open post
Michael Koerfer @OT_MacDonald@infosec.exchange
· 1mo ago
Hacking Ubiquiti airMAX devices within line of sight: Unathenticated RCE with kernel privileges. 😈📡၊၊||၊🗼💥 Security researchers Gaston Aznarez, Federico Kirschbaum, and Dan Borgogno earlier this month shared their research on Ubiquiti airMAX Wi-Fi equipment and presented an over-the-air unauthenticated remote code execution (RCE) vulnerability with kernel privileges. Yes, RCE with just line of sight, kilometers away! Super cool :) The research includes a deep dive into Ubiquiti proprietary protocols, hardware security analysis, and details of two critical vulnerabilities in airMAX equipment. Who is affected? According to the authors: 1️⃣ Critical infrastructure (OT) 2️⃣ Government infrastructure 3️⃣ Public safety (CCTV) 4️⃣ Military infrastructure and more... Great presentation. Enjoy the read and share it with... well, pretty much anyone who works with wireless networks at scale. Thanks, and stay safe! More details: Root From Kilometers Away: Ubiquiti AirMax RCE: https://i.blackhat.com/BH-USA-26/Presentations/BHUS26-Aznarez-Root%20From%20Kilometers%20Away-Slide.pdf
i.blackhat.com
0
0
0
0
Open post
Michael Koerfer @OT_MacDonald@infosec.exchange
· 2mo ago
Replying to
@krypt3ia@infosec.exchange A very good idea!
0
0
0
0
Open post
Michael Koerfer @OT_MacDonald@infosec.exchange
· 2mo ago
Replying to
@FourQ@mastodon.online I feel exactly the same way. I’m getting two of these devices from my source and will do my best to get them up and running. One of the best examples of how it’s done right was pcengines. I have several Alix and APU hardware units, from APU 1 to APU 4, in use and for demo purposes; these run reliably with a wide variety of solutions, including off-the-shelf products that are still actively being developed and supported, as well as DIY setups.
0
2
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 18:50:04 UTC