#JScrambler shares a transparent postmortem on how attackers used a stolen #npm publishing token to ship #malware via its official npm package. A must-read for anyone serious about software supply chain security:
#SoftwareSupplyChainSecurity
👇
#jscrambler
3 posts · Last used Jul 17
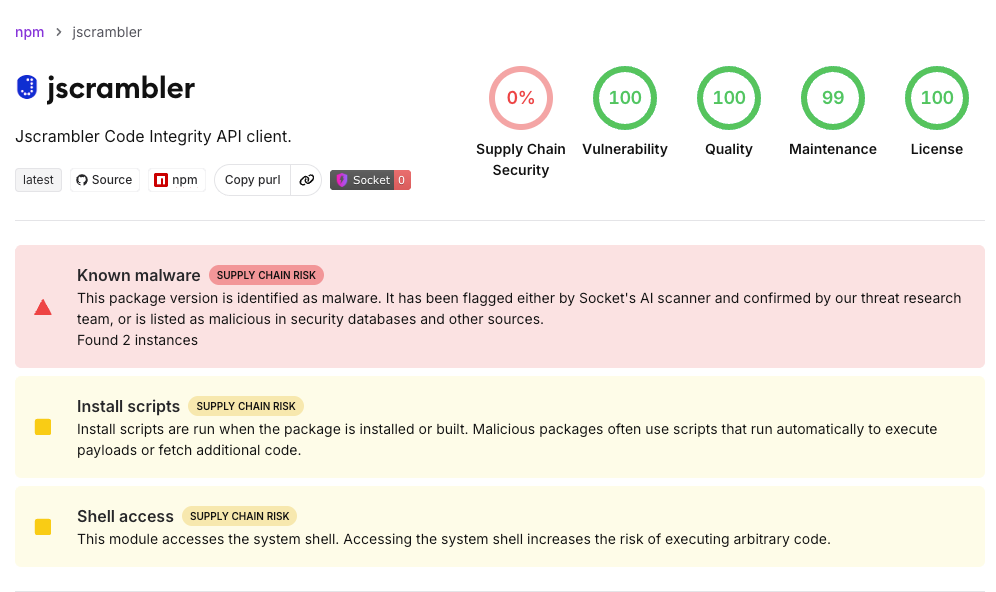
#NPM: A compromised release of the popular #JScrambler npm package introduced hidden #malware binaries that execute automatically during npm install, exposing users to a supply chain attack before any application code runs:
#SoftwareSupplyChainSecurity
👇
You've seen all posts