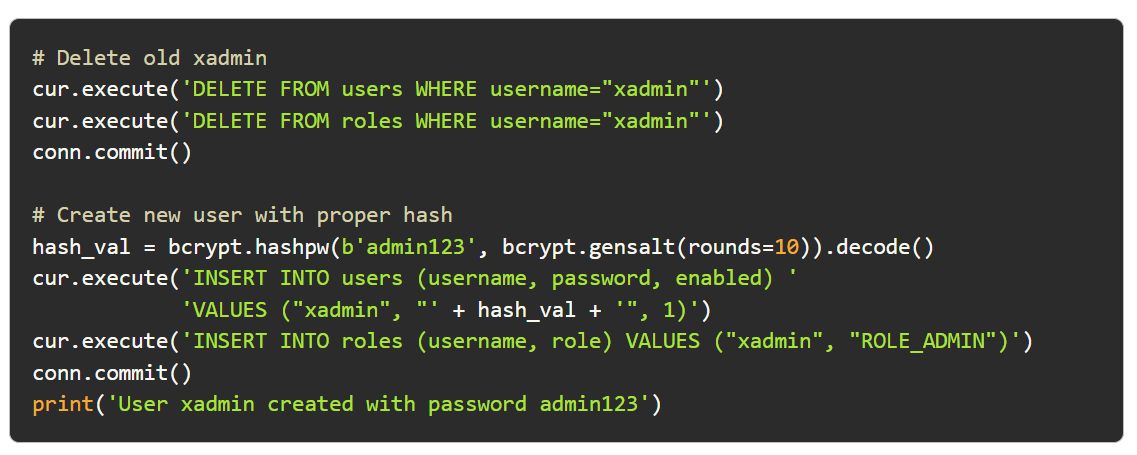
The LLM-operated attacker iterated its way to a working privilege escalation like a methodical corner man adjusting the strategy mid-round until the defense folded.
Audit your Langflow instances now for unauthorized access and check whether privileged Docker socket access is exposed inside your containers.
Reward: You've received a Cracked Weights Chest — contents: 0 recoverable model artifacts, 1 very expensive lesson.
#Ransomware#CyberSecurity#JadePuffer#AIThreats#LLM (3/3)
Sysdig’s Threat Research Team has documented what it assesses to be the first ransomware operation
driven end-to-end by a large language model.
The operator, which Sysdig calls #JADEPUFFER, broke into a server, harvested credentials, moved to a separate production target, encrypted a database, and destroyed data,
all without a human at the keyboard.
Ransomware has always needed a person somewhere in the loop.
That may no longer be true.