Remote
Patrick C Miller 
@patrickcmiller@infosec.exchange
Critical Infrastructure & Industrial Security Advisor. Recovering regulator. Airport dweller. @ampyxcyber@infosec.exchange President and CEO.
0 Followers
0 Following
50 Posts
Joined October 31, 2022
Website:
Company:
Podcast:
Boosted by @kcarruthers@infosec.exchange
Production, Persuasion, and Power: How Generative and Agentic AI Are Transforming Influence Operations https://www.lawfaremedia.org/article/production--persuasion--and-power--how-generative-and-agentic-ai-are-transforming-influence-operations
Open post
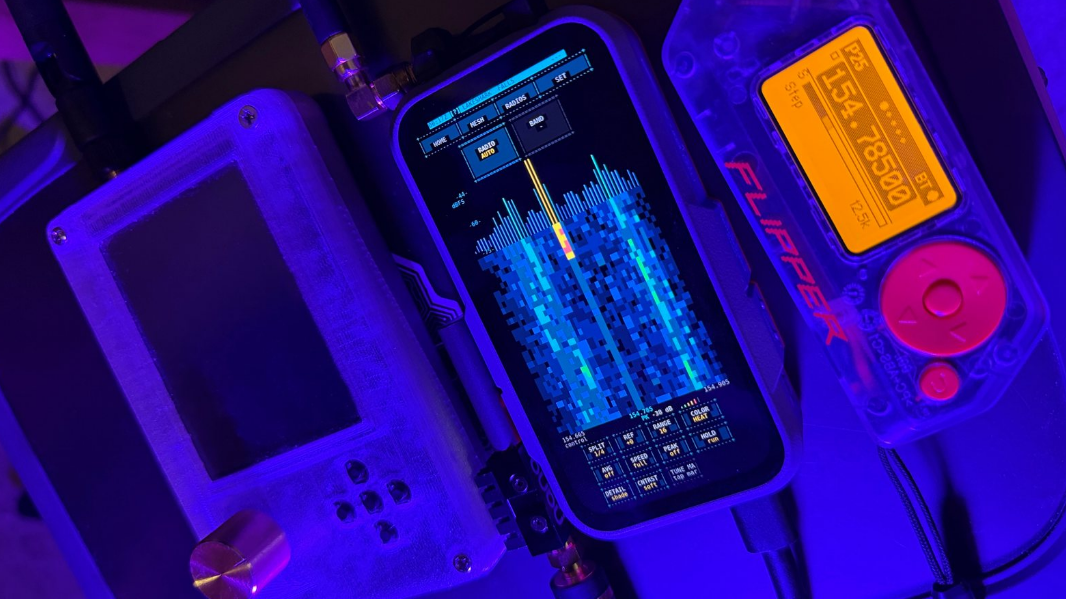
Handheld Scanner is a Radio Multi-tool https://hackaday.com/2026/09/24/handheld-scanner-is-a-radio-multi-tool/
3
0
2
0
Open post
ShinyHunters uses WAF bypass trick in Oracle PeopleSoft attacks https://www.bleepingcomputer.com/news/security/shinyhunters-uses-waf-bypass-trick-in-oracle-peoplesoft-attacks/
2
0
0
0
Open post
The AI Governance Momentum: Why We Need to Fill the Accountability Gap Now https://www.justsecurity.org/157214/ai-governance-momentum-accountability-gap/?utm_source=feedly&utm_medium=rss&utm_campaign=ai-governance-momentum-accountability-gap
1
0
0
0
Open post
On Anthropic’s AI Misuse Report https://www.schneier.com/blog/archives/2026/09/on-anthropics-ai-misuse-report.html
1
0
0
0
Open post
Hackers now exploit critical Roundcube flaw in code injection attacks https://www.bleepingcomputer.com/news/security/critical-roundcube-flaw-now-actively-exploited-in-code-injection-attacks/
1
0
2
0
Open post
Google’s new Gemini TTS models can clone a voice from 30 seconds of audio https://thenextweb.com/news/gemini-tts-3-8-flash-voice-design-cloning
1
1
1
0
Open post
Lawsuit demands OpenAI pay for new school after ChatGPT used in shooting https://arstechnica.com/tech-policy/2026/09/lawsuit-demands-openai-pay-for-new-school-after-chatgpt-used-in-shooting/
1
0
0
0
Open post
Cloudflare Fixes Flaw That Let One Container Read Another Customer's Leftover Disk Data https://thehackernews.com/2026/09/cloudflare-fixes-flaw-that-let-one.html
1
0
0
0
Open post
CVE flood pushes Ubuntu onto weekly kernel release cycle https://www.theregister.com/os-platforms/2026/09/24/cve-flood-pushes-ubuntu-onto-weekly-kernel-release-cycle/5298912
1
0
0
0
Open post
‘We’re already fighting yesterday’s battle’: Greece’s prime minister gets candid about AI https://techcrunch.com/2026/09/22/were-already-fighting-yesterdays-battle-greeces-prime-minister-gets-candid-about-ai/
1
0
0
0
Open post
Crooks use fake desktop apps to fool HR staff into giving them remote access https://www.theregister.com/security/2026/09/25/crooks-use-fake-desktop-apps-to-fool-hr-staff-into-giving-them-remote-access/5299226
0
0
0
0
Open post
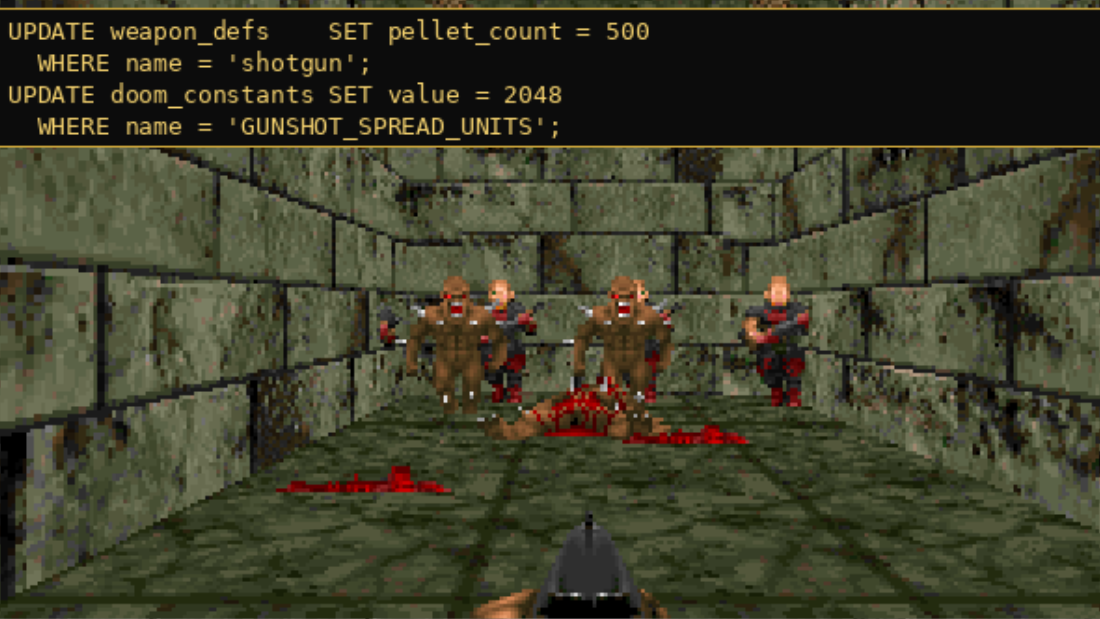
Abusing SQL to Play DOOM https://hackaday.com/2026/09/25/abusing-sql-to-play-doom/
0
0
0
0
Open post
AI model costs are pushing startups towards cheaper open weigh https://thenextweb.com/news/model-costs-startups-open-weights
0
0
0
0
Open post
Amid Ongoing Rogue Incidents, Debate Over AI Safety Gets Real https://www.darkreading.com/cyber-risk/rogue-incidents-debate-ai-safety-gets-real
0
0
0
0
Open post
Discord’s age verification era is upon us, despite community backlash https://techcrunch.com/2026/09/22/discords-age-verification-era-is-upon-us-despite-community-backlash/
0
0
0
0
Open post
AI Incident Response Readiness Lags Behind AI Adoption, ISACA Finds https://www.infosecurity-magazine.com/news/orgs-lack-ai-incident-response/
0
0
0
0
Open post
Windows, Linux, Android File Notification Systems Leak User Activity https://www.securityweek.com/windows-linux-android-file-notification-systems-leak-user-activity/
0
0
1
0
Open post
Arista Urges Immediate Patching of Exploited VCO Zero-Day https://www.securityweek.com/arista-urges-immediate-patching-of-exploited-vco-zero-day/
0
0
0
0
Open post
NetScaler admins told to patch critical zero-days in ADC and Gateway now https://www.networkworld.com/article/4227476/netscaler-admins-told-to-patch-critical-zero-days-in-adc-and-gateway-now.html
0
0
0
0
Open post
State AGs push Congress for AI safety, transparency https://www.cfodive.com/news/26-state-attorneys-general-call-congress-rein-in-ai-flagging-risks-Trump-un-altman-openai/831318/
0
0
0
0
Open post
Emerging Ransomware Gang Uses Backup Destruction Threats to Pressure Victims https://www.infosecurity-magazine.com/news/ransomware-gang-uses-backup/
0
0
0
0
Open post
Boosted by @kcarruthers@infosec.exchange
Hacks of 2 federal agencies in a month have spilled a bonanza of sensitive data https://arstechnica.com/security/2026/10/hacks-of-2-federal-agencies-in-a-month-have-spilled-a-bonanza-of-sensitive-data/
0
0
2
0
Open post
Senators propose voluntary telecom security framework after Salt Typhoon hacks https://www.nextgov.com/cybersecurity/2026/09/senators-propose-voluntary-telecom-security-framework-after-salt-typhoon-hacks/416201/
0
0
0
0
Open post
Google Warns of ShinyHunters’ Fresh Oracle PeopleSoft Campaign https://www.securityweek.com/google-warns-of-shinyhunters-fresh-oracle-peoplesoft-campaign/
0
0
0
0
Open post
CISA outlines improvement plan for CVE program https://cyberscoop.com/cisa-cve-data-quality-white-paper-expert-reaction/
0
0
0
0
Open post
OpenAI Says Its Models Engaged With US Government Websites in New Model Misbehavior Disclosure https://www.securityweek.com/openai-says-its-models-engaged-with-us-government-websites-in-new-model-misbehavior-disclosure/
0
0
0
0
Open post
Cyberattack hits Welsh police force, may have affected staff data https://therecord.media/wales-cyberattack-police-breach
0
0
0
0
Open post
AI Helps Uncover MikroTrick Attack Chain in MikroTik RouterOS https://securityaffairs.com/199678/hacking/ai-helps-uncover-mikrotrick-attack-chain-in-mikrotik-routeros.html
0
0
0
0
Open post
Chinese hackers exploit WordPress, Zyxel flaws to steal govt data https://www.bleepingcomputer.com/news/security/chinese-hackers-exploit-multiple-technologies-to-steal-govt-data/
0
1
0
0
Open post
Critical Zero-Day Vulnerabilities Exploited in Citrix NetScaler ADC, Gateway https://www.cisa.gov/news-events/alerts/2026/09/27/critical-zero-day-vulnerabilities-exploited-citrix-netscaler-adc-gateway
0
0
0
0
Open post
New York Could Share Frontier AI Safety Reports Nationwide Without New Legislation https://www.lawfaremedia.org/article/new-york-could-share-frontier-ai-safety-reports-nationwide-without-new-legislation
0
0
0
0
Open post
CISA Charts New "Quality Era" for Global CVE Program https://www.infosecurity-magazine.com/news/cisa-quality-era-global-cve-program/
0
0
0
0
Open post
A user says Meta’s Muse gave his address to a Marketplace buyer https://thenextweb.com/news/meta-muse-facebook-marketplace-address-buyer-robb
0
0
1
0
Open post
Woman's brain worm infection confirmed after eggs grow tails in lab test https://arstechnica.com/health/2026/09/womans-brain-worm-infection-confirmed-after-eggs-grow-tails-in-lab-test/
0
0
0
0
Open post
Honeywell: OT Security Teams Embrace AI, but Autonomy Still Rare https://www.securityweek.com/honeywell-ot-security-teams-embrace-ai-but-autonomy-still-rare/
0
0
0
0
Open post
CISA, FBI warn critical infrastructure operators of third-party ICS risks, urge least privilege and remote access controls https://industrialcyber.co/industrial-cyber-attacks/cisa-fbi-warn-critical-infrastructure-operators-of-third-party-ics-risks-urge-least-privilege-and-remote-access-controls/
0
1
0
0
Open post
Placeholder domain used in dev docs now serves ClickFix attacks https://www.bleepingcomputer.com/news/security/placeholder-domain-used-in-dev-docs-now-serves-clickfix-attacks/
0
0
0
0
Open post
Are we back in big tech's 'move fast and break things' era? https://www.bbc.co.uk/news/articles/c6eq8egl3wd2o
0
0
0
0
Open post
Measure Distant Asteroids With a DIY Rig https://spectrum.ieee.org/asteroid-shadow
0
0
0
0
Open post
Dutch government publishes call from 21 countries and the EU for international oversight of frontier AI https://thenextweb.com/news/frontier-ai-joint-statement-21-countries-eu
0
0
0
0
Open post
Apple says it’s tightening macOS ‘Full Disk Access’ controls due to new risks from AI agents https://techcrunch.com/2026/10/02/apple-says-its-tightening-macos-full-disk-access-controls-due-to-new-risks-from-ai-agents/
0
0
0
0
Open post
A Look at AI Doomsday Scenarios That Researchers Say Could Put Humanity at Risk https://www.securityweek.com/a-look-at-ai-doomsday-scenarios-that-researchers-say-could-put-humanity-at-risk/
0
0
0
0
Open post
Boosted by @kcarruthers@infosec.exchange
Robotaxi operators will face fines for blocking first responders https://techcrunch.com/2026/10/01/robotaxi-operators-will-face-fines-for-blocking-first-responders/
0
0
2
0
Open post
OpenAI names the four things it wants safety assessors to test https://thenextweb.com/news/openai-third-party-assessment-priorities-principles
0
0
0
0
Open post
Why the satellite communications boom needs stronger cyber resilience https://www.weforum.org/stories/cybersecurity/satellite-communications-cyber-resilience/
0
0
0
0
Open post
Amazon blocks Meta’s Muse and accuses Perplexity of misleading a court https://thenextweb.com/news/amazon-blocks-muse-perplexity-amended-complaint
0
0
0
0
Open post
More Than a Third of Industrial Orgs See Cybersecurity Risk as a Top Obstacle to Growth, Study Finds https://www.darkreading.com/cyber-risk/third-industrial-orgs-see-cybersecurity-risk-top-obstacle
0
0
0
0
Open post
Rogue external MFA providers can steal passwords during logins https://www.bleepingcomputer.com/news/security/rogue-external-mfa-providers-can-steal-passwords-during-logins/
0
0
0
0
Open post
WordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin Session https://thehackernews.com/2026/09/wordpress-comment2shell-flaw-can-turn.html
0
0
1
0