Elektrine
EN
Log in Register
Paige Chat Timeline Gallery Friends Lists Email Drive DNS Resolver Domains VPN Kairo Nerve
Remote

Dissent Doe :cupofcoffee:

@PogoWasRight@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Blogger/journalist at databreaches.net and pogowasright.org. As a retired healthcare professional, breaches in the healthcare sector are my priority.

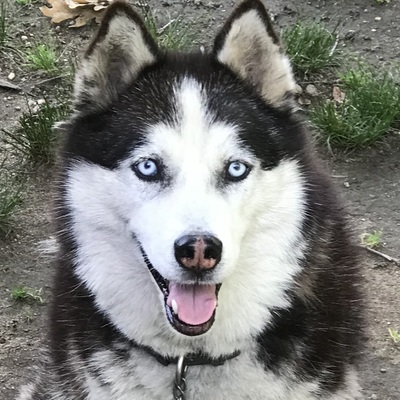
The header pic is Indy, a Siberian husky we rescued in 2016 after I read how nobody wanted her because she was so difficult. She is now living her best life and is a mushball with me.

3211 Followers
1444 Following
50 Posts
Joined November 07, 2022
#DataBreaches:
https://www.databreaches.net
#Privacy:
https://www.pogowasright.org
Have a news tip?:
Signal: Dissent.73
Email:
Breaches@DataBreaches.net
Email:
Breaches@protonmail.ch
Pronouns:
She/Her
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2h ago
Replying to @realhackhistory@chaos.social
@realhackhistory@chaos.social Yeah... but I do distinguish between ShinyHunters and Scattered and Lapsus$ even though they collaborated. And if you were watching them, you may remember times when Shiny showed up and deleted a lot of their stuff or told them to knock it off. It was like herding cats or misbehaving children. And I do think that Shiny announcing they were all one was a huge mistake for ShinyHunters. He even acknowledged that to me months later.
1
1
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 19h ago
What's going on with ShinyHunters? First they accuse Clop of stealing their zero-day for Oracle, then they start hitting medical sector, then they deface and threaten Clop, and now we learn they ratted out TeamPCP? Something's very different.
3
2
2
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 5d ago
I'm always curious to see what cyber insurers are doing on coverage for different scenarios. The Revolut incident reportedly has some insurers re-thinking. Matthew Sellers reports: "Most social engineering endorsements are triggered by a transfer of funds, not a transfer of data. A scam where nothing is paid out but a large volume of identity and biometric data leaves the building can fall between a crime policy, built for financial loss, and a data breach policy, often built around unauthorised access rather than a fraudulent-but-convincing request. Brokers reviewing fintech and financial services clients’ wording may want to check whether “fraudulent instruction” definitions extend to information requests, not just payment instructions." Source: Insurance Business Magazine: https://www.insurancebusinessmag.com/uk/news/cyber/revoluts-paperwork-breach-shows-why-insurers-are-rethinking-what-counts-as-a-cyber-attack-589775.aspx #databreach #cyberinsurance #Revolut
Revolut's paperwork breach shows why insurers are rethinking what counts as a 'cyber attack'
Insurance Business

Revolut's paperwork breach shows why insurers are rethinking what counts as a 'cyber attack'

Fintech bank handed over customer data after fraudster asked for it

4
1
1
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 5d ago
RE: https://mastodon.social/@brianhonan/117275280843738578 Ooh. Interesting thought, thanks. Have you come across situations in which insurers denied coverage for regulator fines but paid other incident response costs from data breaches?
Open quoted post
Quoting
Brian Honan
@brianhonan@mastodon.social
@PogoWasRight@infosec.exchange They may also want to check if the policies cover fines from regulators resulting from data breaches
Open quoted post
2
0
1
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
In January 2025, the WA attorney general sued T-Mobile over a data breach that affected 2M residents (this was the 79M T-Mobile breach). One of the issues in the litigation was that T-Mobile didn't properly notify those affected of the breach -- it omitted telling them in SMS notifications that their SSN had been acquired. For background, see https://www.atg.wa.gov/news/news-releases/ag-ferguson-files-lawsuit-against-t-mobile-massive-data-breach Now a court has agreed with the state that the text message notifications did not comply with the state's breach notification law: https://www.seattletimes.com/business/t-mobile-violated-wa-data-breach-notification-law-judge-rules/ T-Mobile says it will appeal. #databreach #incidentresponse #notifications #TMobile
22
4
12
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago

The city manager of the City of Coweta is refusing to even contact unnamed threat actors and says the city will not pay any ransom in response to a recent ransomware attack.

Why? Because the city manager was with another city that was attacked; even though that city paid the ransom, it was reinfected two weeks later. So now she is very anti-paying.

Read more at KTUL:
https://ktul.com/news/local/city-of-coweta-refuses-to-pay-ransom-after-system-wide-cyberattack-08-08-2026

And as I previously reported on this incident, the city has an offsite backup they say they can use to restore all city files after they clean the servers of ransomware.

Good for her and the city.

#govsec #ransomware #cybersecurity #databreach

6
0
7
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
"Marco Rubio says the US will deny visas to foreign nationals involved in cybercrime and may extend the restrictions to their immediate families.......... Marco Rubio says the US will deny visas to foreign nationals involved in cybercrime and may extend the restrictions to their immediate families." (see on The Register) Why not allow the suspected criminals to get visas, allow them to fly over here, and then arrest them and prosecute them?
7
3
1
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
NEW by me: The “Anonymous” Tip System That Wasn’t: Three Months Later, Why Hasn’t Navigate360 Notified Anyone? Note: there is a trigger warning at the top of this article as it contains sensitive material from tips submitted to and about students on what were supposed to be "anonymous" tiplines. https://databreaches.net/2026/07/06/the-anonymous-tip-system-that-wasnt-three-months-later-why-hasnt-navigate360-notified-anyone/ This is the longest post I have ever done because people need to be more aware that this was the worst breach EVER in terms of highly sensitive personal information of students and their peers and families. Great thanks to @douglevin@infosec.exchange for his comments and suggestions on the post. @funnymonkey@freeradical.zone @mkeierleber@journa.host @euroinfosec@infosec.exchange @jgreig@ioc.exchange @zackwhittaker@mastodon.social @campuscodi@mastodon.social @politico@newsie.social @dustinvolz@journa.host #databreach #anonymity #infosec #cybersecurity #Navigate360 #P3Campus #P3Global
12
2
9
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Replying to @PogoWasRight@infosec.exchange
I wish this wasn't being handled in a partisan way. Surely Democrat and Republican state attorneys general can agree that questions need answers about this incident. I really wish they had collaborated on this one.
5
2
1
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago

One of the dozens of new #ransomware groups this year is a group calling itself #Orova. Since early May, they appear to have dozens of victims in about half a dozen countries.

Three of the listings are U.S. medical entities, so, of course, I reached out to them to find out more.

My new report:

Cardiology Associates of Port Huron remains silent although they were allegedly hacked and had patient data stolen in June.

https://databreaches.net/2026/08/06/cardiology-associates-of-port-huron-remains-silent-although-they-were-allegedly-hacked-and-had-patient-data-stolen-in-june/

#databreach #healthsec #cybersecurity #extortion #encryption

4
1
5
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
GovTech reoorts on the ITRC's H1 report: "[ITRC]found that 1,029 data compromises generated 471 million breach notices in the first half of the year, with one incident — the breach involving Instructure’s Canvas platform — accounting for 275 million of those notices, or about 58 percent of the total."
5
3
2
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
More than 30 Minnesota water systems targeted in cyberattack: https://www.fox9.com/news/30-minnesota-water-systems-targeted-cyber-attack I haven't seen Handala or any group claim responsibility yet, but it's noteworthy that the quality of drinking water does not appear to have been tampered with. #cyberwar #Handala #criticalinfrastructure #water
4
0
3
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
NEW by me: more analysis of the Navigate360 data breach, this one focusing on Crime Stoppers and crime-oriented tip lines using P3 Global Intel: Crime Stoppers assured people their tips would be anonymous. Then more than 1 million tips leaked: https://databreaches.net/2026/07/24/crime-stoppers-assured-people-their-tips-would-be-anonymous-then-more-than-1-million-tips-leaked/ If anyone has a connection in their state attorney general's office, encourage them to read this and open an investigation. A table in the article shows how many tips were submitted for each chapter of Crime Stoppers that appeared in the dataset. #databreach #cybersecurity #infosec #Navigate360 #CrimeStoppers @zackwhittaker@mastodon.social @campuscodi@mastodon.social @jgreig@ioc.exchange @douglevin@infosec.exchange @ajvicens@mastodon.socialspill.com
4
0
7
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
Another entity files for insolvency after a data breach. Sounds like the data breach was responsible in this case. From ZEGO's notice: "The cyberattack of March 29, 2026, however, impacted our company to an extent that we could not fully compensate for despite our best efforts. The consequences resulted in a production outage of nearly six weeks and significant financial strain. These effects ultimately impacted our financial situation so severely that filing for insolvency became necessary. " https://www.zego-tvz.com/wichtige-information/ I didn't find any group listed as claiming responsibility for this incident. @sawaba@infosec.exchange #databreach #insolvency
5
10
1
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
TFW you finish entering all your new appointments for this week, only to realize you entered them in last week's calendar and now mucked everything up. 😭 🤦‍♀️
3
1
1
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
NEW by me: Fintech firm Nayax investigating breach; The Syndicate claims it acquired 1 billion card records and other important data (It appears there's another TA that I had never heard of before. And note that the TA has offered no POC at this point). https://databreaches.net/2026/07/08/nayax-investigating-breach-the-syndicate-claims-it-acquired-1-billion-card-records-and-other-important-data/ #databreach #fintech #Nayax
5
0
3
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
RE: https://infosec.exchange/@chum1ng0/117044228483502361 You weren't alone, @chum1ng0@infosec.exchange . Their misclassification reportedly affected thousands of blogs: https://cybersecuritynews.com/google-blogger-locked-legitimate-websites/ But this is a good time for you to think about backups and alternatives. :)
2
1
3
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
It has been four months since a hacktivist obtained 8.3 million tips submitted to organizations such as Crime Stoppers and Sandy Hook Promise. What the hacktivist found in terms of lack of security was appalling. In the four months since Navigate360 (the parent company for P3 Global Intel and P3 Campus) learned of the breach, they have made zero public statements after the first day when they said they were investigating. Their wall of silence, and the conspiracy of silence involving programs like Safe2Say, Safe2Tell, SilentWitness, and Crime Stoppers has been unacceptable. No one has been notified, it seems. And we cannot find any state regulator that has been notified, either. DataBreaches wrote about the disgraceful lack of transparency in a new post this week: Broken Promises of Anonymity: Four Months Later, Still No Transparency. Now We’re Seeking Accountability. https://databreaches.net/2026/07/20/broken-promises-of-anonymity-four-months-later-still-no-transparency-now-were-seeking-accountability/ In conjunction with that post, I filed a formal FTC complaint against Navigate360 under Section 5 of the FTC Act and also notified the National Association of Attorneys General, saying that states should be protecting their residents by investigating the breach and incident response. And that's not all. Today, I have filed a complaint with one state attorney general's office and will be filing with others. I will also be publishing a post this week about the Crime Stoppers data in the dataset and the ridiculous response by legal counsel for Crime Stoppers USA to inquiries by DataBreaches about what was being done to improve security. I have not written up anything specific to all of the Canadian data in the dataset, but yes, Canadian crime stoppers and police organizations are in there, too. Take Action: If you know anyone in a state attorney general's office, encourage them to read up on the breach on my site, where I have also published tables with data for easy reference. If you know anyone in the FTC, encourage them to read the complaint I filed and to act on it. If you know any personal injury lawyer who should be handling a massive lawsuit alleging privacy harms, point them to my coverage. Children and adults who tried to be good citizens and relied on promises of anonymity have been put in harm's way. We cannot allow this to be minimized or covered up. @zackwhittaker@mastodon.social @nytimes@mediastodon.com @caparsons@mastodon.social @douglevin@infosec.exchange #databreach #infosec #Navigate360 #CrimeStoppers #Safe2Tell #Safe2Say #SilentWitness #SandyHookPromise #transparency #notification #NAAG #FTC
2
0
2
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
Milford, New Hampshire seems to be dealing with a cyberattack since July 15, but they don’t call it that and haven’t revealed many detail details. A resident wonders whether the breach was caused by a vulnerability he reported to them in May that they did not address. My post about it all: https://databreaches.net/2026/07/21/milford-new-hampshire-confirms-unauthorized-activity-withholds-details-of-suspected-cyberattack/ #govsec #cybersecurity
2
2
2
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago

New York State Department of Financial Services announced on August 5 that Order Express, Inc., a licensed money transmitter, will pay a $250,000 penalty for violations of DFS’s cybersecurity regulation (23 NYCRR Part 500).

Order Express suffered a ransomware attack in 2022, which they reported appropriately. But then the DFS's investigation revealed that the entity did not have adequate cybersecurity risk assessment or plan.

Read more at: https://www.dfs.ny.gov/reports_and_publications/press_releases/pr20260805

#NYSDFS #OrderExpress #databreach #cybersecurity #FinSec #ransomware #riskassessment

1
0
1
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Replying to @hnapel@mastodon.social
@hnapel@mastodon.social That's somewhat lost on me... I never really watched that show more than once or twice. All I remember about it was that there was something about apple pie?
1
0
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
Replying to @sawaba@infosec.exchange
@sawaba@infosec.exchange @adamshostack@infosec.exchange Ah. Well, this is on YOU, then, of course. :) It's fantastic that you had the foresight to start this years ago and that you maintain it. It really is a great resource for any journalist or researcher who wants to fact-check claims about the consequences of breaches.
2
1
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
Replying to @sawaba@infosec.exchange
@sawaba@infosec.exchange @adamshostack@infosec.exchange That was my sense, too. Chapter 11 equivalence. Maybe you should have a Chapter 11/insolvency/wounded but not dead sheet. Because how do we know that a company ever successfully bounces back and doesn't wind up dead after all?
2
2
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Replying to @chum1ng0@infosec.exchange
@chum1ng0@infosec.exchange Yes, Chu, you need to appeal and say there is NOTHING in your blog posts that is malware or any malicious content. Tell them to have an informed human being read the posts and they'll confirm that. @javilopezg@mastodon.social
1
0
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Replying to @chum1ng0@infosec.exchange
@chum1ng0@infosec.exchange Those complaints/reports show that Blogger has a false positive problem/issue. Add your report to it and appeal the blocking.
1
2
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Replying to @chum1ng0@infosec.exchange
@chum1ng0@infosec.exchange Not necessarily. Might be a script looking for certain words type of thing.
1
0
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Replying to @chum1ng0@infosec.exchange
@chum1ng0@infosec.exchange It gives you the link to use to appeal.
1
0
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Replying to @chum1ng0@infosec.exchange
@chum1ng0@infosec.exchange I think they made a mistake. And if they don't undo the block, maybe look at this page to get free help: https://www.trust.org/our-services/legal-services-for-media/
1
1
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Replying to @chum1ng0@infosec.exchange
@chum1ng0@infosec.exchange OK, so you clearly should file an appeal and tell them that although you report about data security incidents, you never include malware or malicious content and to please re-read your posts.
1
4
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Replying to @chum1ng0@infosec.exchange
@chum1ng0@infosec.exchange I responded to your message on Signal, but let's keep this here because it may be a press freedom/ free speech issue. What blog/platform banned your blog? And what reason did they give? And do you have a complete backup that you can upload elsewhere? As I mentioned the other day, there are free legal resources and help for independent media, but first explain more about what happened and why. #pressfreedom @freespeech #censorship (For those of you who don't know, Chu used to report LatAm breaches on DataBreaches.net. It's hard for me to imagine how he would get banned for the kind of reporting he does, but... let's find out. )
1
9
1
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Replying to @husjon@fosstodon.org
@husjon@fosstodon.org I dunno, but I wouldn't be surprised if Trump sued OpenAI for 43 billion dollars or something....
1
0
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Replying to @fuzzyfuzzyfungus@cyberplace.social
@fuzzyfuzzyfungus@cyberplace.social From what I am reading, Democrat attorneys general were not asked to participate or even review the letter. This was apparently intended to be partisan.
1
0
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
Replying to @SteveBellovin@infosec.exchange
@SteveBellovin@infosec.exchange I want to see what they do with the feedback. In the past, I've gotten follow-up phone calls. In this case, I was so upset over the anethesiology situation that I actually have written a request under HIPAA to amend my medical records to remove his terrible recommendation.
2
4
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Replying to @PogoWasRight@infosec.exchange
ShinyHunters says the May attack wasn't them or SLH, so I corrected my post on that point. @bobdahacker@infosec.exchange @campuscodi@mastodon.social
1
0
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Replying to @douglevin@infosec.exchange
@douglevin@infosec.exchange @funnymonkey@freeradical.zone Instructure's most recent update even tells schools that if they discover notifications need to be sent, to contact them and Instructure will make the notifications via Kroll, so yes, it looks like not all notifications have been made. I wonder if ITRC used the "275 million" number from ShinyHunter's leak site claims or some other source.
1
1
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
Replying to @adamshostack@infosec.exchange
@adamshostack@infosec.exchange @sawaba@infosec.exchange My fault. I probably should have mentioned him at the top instead of the bottom.
1
1
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
Replying to @douglevin@infosec.exchange
@douglevin@infosec.exchange @funnymonkey@freeradical.zone @mkeierleber@journa.host @euroinfosec@infosec.exchange @jgreig@ioc.exchange @zackwhittaker@mastodon.social @campuscodi@mastodon.social @politico@newsie.social @dustinvolz@journa.host We both have things going on right now. Let's talk in a few weeks. I have some ideas. I #Navigate360 #P3Campus #CrimeStoppers #Safe2SayPA #Safe2Tell #SandyHookPromise #databreach #hacktivism #Anonymity #Accountability
1
0
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
OT: My health system asked for my feedback about a recent hospital experience. I gave everything a good rating until we got to the survey questions on anesthesia, and I wrote, "The anesthesiologist should be shot and killed....." Well, they asked for feedback. 😡
1
7
1
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Developing: AnMed reports phone and internet outage impacting all 4 hospital locations in South Carolina and Georgia. Emergency rooms remain open. No group has claimed responsibility as yet. #cyberattack #healthsec
0
0
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
Replying to @cwbussard@ioc.exchange
@cwbussard@ioc.exchange are you having trouble with the RSS feed? Email me your IP address address and I’ll whitelist it. Unfortunately, the. CF remains necessary because I continue to get DDoS attacks when I drop it.
0
0
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2h ago
Replying to @realhackhistory@chaos.social
@realhackhistory@chaos.social Well, the threats against Nixon and Larsen really caused chaos, and leaking some USgov info. After Jubair and Flowers were arrested and detained, things calmed down a bit, but still not a good look.
0
0
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 14h ago
Replying to @realhackhistory@chaos.social
RE: https://chaos.social/@realhackhistory/117300415989405928 @realhackhistory@chaos.social So the shift in behavior I notice with ShinyHunters has also been seen in other groups. It seems to me that we should be paying more attention to this to figure out how to use it to aid in disruption, and not just write it off as so many kids being "nuts."
Open quoted post
Quoting
[realhackhistory@home]#
@realhackhistory@chaos.social
@PogoWasRight@infosec.exchange I’d also say this needs to be viewed against the backdrop of increased rivalry in the ransomware / extortion scene, less victims are paying and the groups are at each others throats. DragonForce has defaced other groups extortion blog sites in the past for instance, and Russian groups have threatened each other publicly of late in ways they would not previously have.
Open quoted post
0
1
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
Replying to @SteveBellovin@infosec.exchange
@SteveBellovin@infosec.exchange 😂
0
0
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
Replying to @amvinfe@infosec.exchange
@amvinfe@infosec.exchange I have no idea what to make of all that. Do you believe any of it?
0
1
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 1mo ago
Replying to @octothorpe@mastodon.online
@octothorpe@mastodon.online (1) if they're employees for tax records, (2) for customers who want to finance a phone and they'll do a credit check, and (3) to verify identity if people call with a support request. 4).... ??? I dunno.
0
0
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 18h ago
Replying to @realhackhistory@chaos.social
@realhackhistory@chaos.social Did you see the 2020 - 2023 ShinyHunters as "nuts?"
0
1
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 3h ago
Replying to @realhackhistory@chaos.social
@realhackhistory@chaos.social In them, no. Monitoring them, yes. And of course, they ultimately claimed it was all a big disinformation and distraction ruse.
0
1
0
0
Open post
Dissent Doe :cupofcoffee: @PogoWasRight@infosec.exchange
· 2mo ago
Replying to @SteveBellovin@infosec.exchange
@SteveBellovin@infosec.exchange You're right. I brought it with me to the pre-surgical appointment for an upcoming surgery and they didn't know what to do with it. They finally decided to scan it in, but that is probably not going to trigger the HIPAA review.
0
2
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)
  • Source code

Legal

  • Terms of Service
  • Privacy Policy
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 17:08:53 UTC